



Premium File
523 Q&A
$76.99$69.99
Microsoft Azure Security AZ-500 Exam Questions & Answers, Accurate & Verified By IT Experts
Instant Download, Free Fast Updates, 99.6% Pass Rate
AZ-500 Premium File: 523 Questions & Answers
Last Update: Sep 06, 2026
AZ-500 Training Course: 73 Video Lectures
AZ-500 PDF Study Guide: 635 Pages
$79.99
Microsoft Azure Security AZ-500 Exam Screenshots
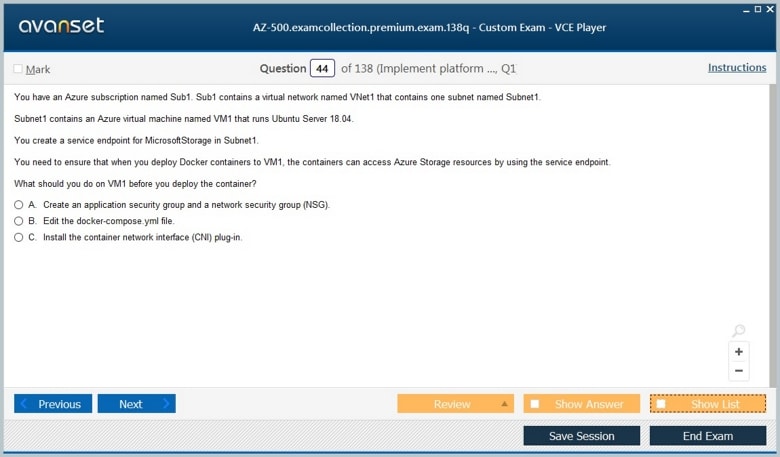
Microsoft Azure Security AZ-500 Practice Test Questions in VCE Format
Microsoft Azure Security AZ-500 Practice Test Questions, Exam Dumps
Microsoft AZ-500 (Microsoft Azure Security Technologies) exam dumps vce, practice test questions, study guide & video training course to study and pass quickly and easily. Microsoft AZ-500 Microsoft Azure Security Technologies exam dumps & practice test questions and answers. You need avanset vce exam simulator in order to study the Microsoft Azure Security AZ-500 certification exam dumps & Microsoft Azure Security AZ-500 practice test questions in vce format.
AZ-500, Microsoft Azure Security Technologies, retired on August 31, 2026. It was the exam behind Microsoft Certified: Azure Security Engineer Associate and for years covered identity and access, networking, compute, storage, database security, security operations, and cloud workload protection. The exam can no longer be scheduled, so current learners should not treat an AZ-500 study plan as an active certification path.
The AZ-500 exam remains useful as historical security-engineering context because many of its principles are durable. Least privilege, network segmentation, secure workloads, data protection, Defender for Cloud, monitoring, and incident-oriented thinking still matter. Microsoft has replaced the credential with SC-500, Cloud and AI Security Engineer Associate, which expands the role toward modern cloud and AI workload protection.
The right way to study AZ-500 material now is to preserve the security model while updating the platform and credential context. Think of the old exam as a map of Azure security foundations, then move current certification preparation to SC-500. That approach avoids two mistakes: discarding valuable knowledge simply because an exam retired, or assuming old objectives still represent Microsoft's current security-engineer role.
AZ-500 emphasized Microsoft Entra identities, privileged roles, authentication controls, access reviews, and authorization to Azure resources. Those concepts remain central because attackers often seek credentials and permissions rather than exploiting infrastructure directly. Security engineers need to understand the difference between proving identity and authorizing actions, then reduce privilege, enforce stronger authentication, and monitor risky behavior.
Build a small identity lab with standard users, privileged administrators, groups, and a workload identity. Apply least-privilege Azure roles and test what each identity can actually do. Use the Microsoft Entra ID model to trace sign-in and access decisions. Then introduce a Conditional Access control or privileged workflow. The goal is to make identity a measurable security boundary rather than an assumed property of account names.
The retired exam covered virtual network security, network security groups, application security groups, Azure Firewall, private connectivity, DDoS protection, and secure administrative access. The enduring principle is to know which traffic is required and deny unnecessary paths. Broad networks with permissive rules make later security analysis difficult because every system can potentially reach every other system.
Create two application subnets and define permitted flows before writing any rule. Then implement NSGs and test effective behavior. The comparison between network and application security groups helps explain address-based and workload-grouping approaches. Add a firewall or private endpoint where justified, but avoid assuming that more security products automatically create better security. Clarity of allowed traffic is more important than the number of controls.
Compute security requires hardening the workload as well as the Azure resource. Virtual machines, containers, and application platforms each expose different responsibilities. Security controls can include hardened images, patching, endpoint protection, disk encryption, just-in-time access, vulnerability management, managed identities, and secure configuration. A resource can be isolated at the network layer and still be vulnerable through outdated software or excessive local privilege.
Threat-model a virtual machine from provisioning through retirement. Ask where the image came from, how administrators connect, how patches are applied, which identity the workload uses, where secrets live, what endpoint telemetry is collected, and how the system is decommissioned. Repeat the exercise for a managed application or container workload. This comparison teaches the shared-responsibility shift that occurs as more infrastructure management moves to the platform.
AZ-500 included securing storage and databases, which requires more than enabling encryption. Engineers need to control who can access data, from which networks, using which credentials, and under what auditing policy. They must also protect keys or secrets and ensure that recovery mechanisms do not become an unmonitored path to sensitive information. Data security should follow the information from application request through storage and backup.
Choose a storage service and make it private by default. Replace account-wide credentials with identity-based access where practical, restrict network exposure, and enable logging. Then test a denied request to verify that the control is real. The Azure RBAC model is useful here because data-plane permissions and management-plane permissions should be granted deliberately rather than assumed to be the same.
Cloud security posture management identifies misconfigurations, weak controls, exposed resources, and attack paths that may not be obvious from one workload team's view. AZ-500 candidates needed to understand Defender for Cloud capabilities and how recommendations influence security posture. The modern lesson is to treat findings as prioritized engineering work, not a score to maximize blindly. Context matters: a recommendation may be urgent for an internet-facing production service and lower priority for an isolated disposable lab.
Review a set of Defender for Cloud recommendations and classify them by exposure, business impact, exploitability, and remediation effort. Then fix one control and verify the signal changes. The distinction between Defender for Cloud and Microsoft Sentinel is also useful: posture and workload protection are related to, but not identical with, the SIEM and incident-operations function.
A security engineer needs logs and detections that support decisions. Alerts without context create fatigue, while missing telemetry leaves incidents unexplained. Azure activity, identity events, network flows, workload alerts, Defender signals, and centralized analytics can contribute to an investigation. The old exam's security-operations content remains valuable because prevention will never eliminate every suspicious event.
Take one simulated incident, such as a suspicious administrator sign-in followed by a network-rule change. Determine which logs prove the sign-in, which records show the resource change, and how a security team would correlate the activity. Broader Microsoft Sentinel context helps frame how distributed signals can support investigation. The objective is to build an evidence chain that answers what happened and what should be contained.
Microsoft identifies Cloud and AI Security Engineer Associate as the direct replacement for the retired Azure Security Engineer Associate. That evolution reflects a broader environment: security engineers now protect cloud platforms alongside AI services, models, data flows, agents, and the identities that connect them. Traditional Azure controls remain relevant, but the threat model has expanded to include prompt-driven actions, model access, AI data exposure, and newer workload patterns.
Candidates moving from old AZ-500 notes should create a transition matrix. Keep identity, network, compute, data, posture, and monitoring foundations, then add the AI and cross-cloud areas required by the Cloud and AI Security Engineer Associate path. This is more useful than attempting to stretch an old objective list until it resembles the new exam.
The Azure Security Engineer Associate credential remains important historically, and holders may still have it on their transcript while it is valid. That does not change the fact that the exam retired. New candidates need current documentation and the SC-500 path. Service behavior, defaults, threat patterns, and Microsoft's security portfolio continue to evolve.
Use old AZ-500 labs to practice least privilege, segmentation, secure workloads, data protection, posture management, and investigation. Verify every implementation against current Azure guidance. When a lab depends on a retired feature or old portal flow, rebuild the control using the current service. The learning objective is security reasoning, not preservation of a historical interface.
Key and secret management deserves explicit practice because credentials often become the weak link in otherwise secure architectures. Identify every place a workload needs a password, certificate, token, or key, then ask whether the platform can replace that secret with a managed identity. Where a secret is unavoidable, centralize storage, restrict retrieval, rotate it, and monitor access. Security designs should make credential exposure difficult and recovery from compromise straightforward.
Private connectivity is another durable AZ-500 theme. A service that supports a private endpoint can often be removed from direct public exposure, but the change introduces DNS, routing, and operational dependencies. Test a private-access design from both allowed and denied networks. Verify that the application still resolves the correct address and that administrators understand how to troubleshoot it. Security improvements that cannot be operated reliably often get bypassed later.
Incident response should be rehearsed with containment in mind. If a workload identity is suspected of compromise, determine how to disable or restrict it, which secrets or credentials must be rotated, what network paths should be blocked, and which logs must be preserved. Then decide how the service returns to normal operation. This connects identity, network, data, and monitoring controls into one security workflow instead of studying each in isolation.
The move to SC-500 also expands the threat model around AI. Model endpoints, agents, training or grounding data, tool permissions, and AI-driven automation introduce new paths for data exposure or unsafe action. Traditional principles still apply—least privilege, segmentation, secure secrets, monitoring, and governance—but they must be applied to components that can make probabilistic decisions or invoke tools on a user’s behalf. That is why the successor credential is more than a rename.
Security architecture should also account for exceptions. Emergency access, legacy integration, vendor support, and temporary troubleshooting can require broader permissions or connectivity than the steady-state design allows. Define how an exception is approved, time-limited, logged, and removed. If an emergency control becomes permanent because no one owns the rollback, it quietly erodes the least-privilege model. Practicing exception handling helps bridge textbook security controls with the operational reality that SC-500 candidates will encounter in cloud and AI environments.
AZ-500 is retired, but its strongest lessons still form part of modern Azure security engineering. Keep the identity, network, workload, data, posture, and monitoring foundations, then move current certification preparation to SC-500 so that cloud and AI security are studied together.
Go to testing centre with ease on our mind when you use Microsoft Azure Security AZ-500 vce exam dumps, practice test questions and answers. Microsoft AZ-500 Microsoft Azure Security Technologies certification practice test questions and answers, study guide, exam dumps and video training course in vce format to help you study with ease. Prepare with confidence and study using Microsoft Azure Security AZ-500 exam dumps & practice test questions and answers vce from ExamCollection.
Purchase Individually
Microsoft AZ-500 Video Course
Top Microsoft Certifications










Top Microsoft Certification Exams
Site Search:

SPECIAL OFFER: GET 10% OFF

Pass your Exam with ExamCollection's PREMIUM files!
SPECIAL OFFER: GET 10% OFF
Use Discount Code:
MIN10OFF
A confirmation link was sent to your e-mail.
Please check your mailbox for a message from support@examcollection.com and follow the directions.

Download Free Demo of VCE Exam Simulator
Experience Avanset VCE Exam Simulator for yourself.
Simply submit your e-mail address below to get started with our interactive software demo of your free trial.
AZ-500 Premium File: 348 valid i pass score 800 . 1 LAb 11task 29/07/2022
premium dump file is valid i pass 800 , have exam 1 lab 8 task
Does anyone passed the exam recently with premium dump? Is it still valid? Thanks
Has anyone used this for their az500 exam in 2022?
Are there any labs or simulations in this exam?
Is premium dump still valid? anyone recently passed exam?
Premium file helps but there is a lot of new content on this exam. Passed this morning, there was about 10 new questions and a new case study. Didn't get any lab simulation questions. You will need good knowledge of the topics until the premium file is updated with the new questions
Premium dumps was really helpful. Passed today. dumps valid
Inglés
Hello everyone, the premium dump file is valid, I have scheduled to take the exam next week, can you confirm if there are laboratories?
The dump Questions will include the Renewal Questions soon?
The labs have to do with Vnets, Users access, Firewall, NSGs, Log Analytic Workspaces, Keyvault, SQL Security, SQL Auditing, Email Notifications, Azure Backup. I cannot remember the specifics, but more or less these are the topics. Please note that there were no Powershell or CLI questions.
I successfully passed the AZ-500 exam using the premium bundle. All the questions in the test came from the premium file, and the content in the course covered most of the details of the exam. The Microsoft AZ-500 exam contains one lab with 12 tasks from the Azure Portal, no Power Shell or ARM template like (connect VNET to ASG, add domain to Azure AD, create rules and e-mail notification, assign access to specific users on storage account, encrypt storage account by creating kayvault key & secret, configure inbound NSG on VM) – that is what I remember. Good luck for you all!
The premium dumps are 99% Valid. I passed the AZ-500 test yesterday. I had 2 new questions on Key Vault and 12 lab questions. Hands-on experience with the Azure Portal was also required, I advise to practice the Azure Portal Lab before attempting the exam to know the details.
I can agree that the premium file is valid. I passed with 810. There were 3 new questions and there were no simulations during the test. However, I managed to deal with all of the questions.
I passed the AZ-500 exam with 800 points today using the premium file. These practice questions helped me a lot during my preparation period. I was able to cover all the topics with the help of the official study guide and then test my skills with the help of the materials from ExamCollection. Thank you for these high-quality products!
I passed the exam using the premium dump, it is valid but not all the questions from the dump.
I got new questions about Azure Sentinel.
good luck
Passed today, premium still valid but lot of new questions regarding Sentinel, blueprints and azure bastion in peered VNETs
Passed on 17 of march. Premium is still valid had only one new question.
Passed today. Premium file is still valid and 3 new questions. All portal tasks (12) from the dump. Pay attention to the portal warnings and wait enough until newly created object to be shown.
Premium file is still valid, only some new question. I had 50 question, 1 scenario, 1 Lab with 12 task. Thanks examcollection!
I passed az500 today and premium file is 100% valid. Thanks exam collection 👍.
Dump is 100 % valid.Passed today with 84 % score..90 % queations came from the Dump.Labs also covered in the dump
Passed today 80% from premium dump, 3 new questions and few labs were new
Hi All
I am writing on 07-FEB-2020, am using the premium dump 132q and online material. I will let you all know how it goes.
Best of luck to those writing
Any recent success?
Is the premium dump still valid? Anyone sat the exam recently?
Can anyone please confirm what is the current version going on in premium file?
Premium Dumps 99% Valid, Passed yesterday with 2 new questions on multiple choice on KeyVault.
12 Lab Questions, small tasks but required Hands-On Experience with the Azure Portal (practice the Azure portal Lab before attempting the exam to know which blades to go during exam)
Premium Dumps 99% Valid, Passed with 770 today.
14 Lab Questions, small tasks but required Hands-On Experience with the Azure Portal
Passed exam last week. Latest premium dump (132q) is valid and contains lab questions
The Premium file 132 Questions contain lab?
Premium is valid for the Multiple choice, hot spot, drag and drop, etc questions. Labs are not in the premium file.