
Pass Your Cisco CyberOps Associate Certification Easy!
Cisco CyberOps Associate Certification Exams Questions & Answers, Accurate & Verified By IT Experts
Instant Download, Free Fast Updates, 99.6% Pass Rate.
Understanding Cisco Cybersecurity Operations Fundamentals (CBROPS)
Includes 482 Questions & Answers
$69.99
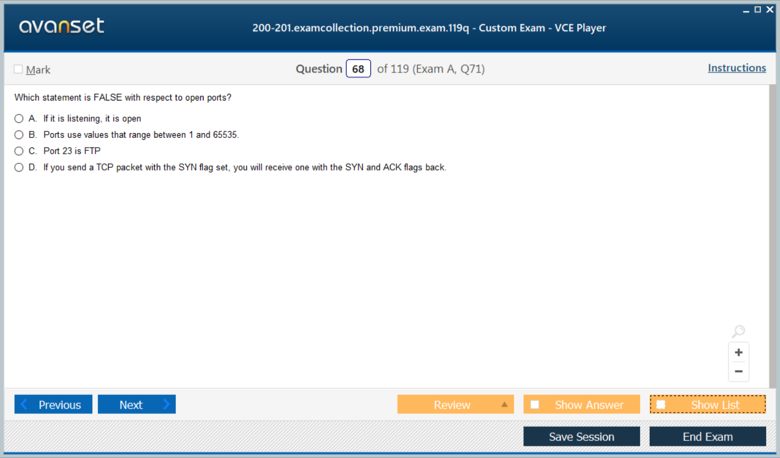
Cisco CyberOps Associate Certification Exams Screenshots
CyberOps Associate Product Reviews
Download Free CyberOps Associate Practice Test Questions VCE Files
| Exam | Title | Files |
|---|---|---|
Exam 200-201 |
Title Understanding Cisco Cybersecurity Operations Fundamentals (CBROPS) |
Files 2 |
Cisco CyberOps Associate Certification Exam Dumps & Practice Test Questions
Prepare with top-notch Cisco CyberOps Associate certification practice test questions and answers, vce exam dumps, study guide, video training course from ExamCollection. All Cisco CyberOps Associate certification exam dumps & practice test questions and answers are uploaded by users who have passed the exam themselves and formatted them into vce file format.
CyberOps Associate: The Legacy Name Behind CCNA Cybersecurity
CyberOps Associate remains a familiar search term, but Cisco changed the credential’s naming in two stages. Effective January 21, 2025, Cisco renamed CyberOps Associate to Cybersecurity Associate as the 200-201 exam moved to its v1.2 update. On February 3, 2026, Cisco renamed Cybersecurity Associate again as CCNA Cybersecurity. Active certification holders carried forward through those branding changes. The underlying 200-201 exam remains central, now presented by Cisco as 200-201 CCNACBR v1.2.
That distinction matters because older study material can still be technically useful while giving candidates outdated branding. The subject did not suddenly become a different discipline. It still centers on security concepts, monitoring, host-based analysis, network intrusion analysis, and security policies and procedures. What changed is how Cisco aligns the credential inside its broader certification framework.
Within Cisco certifications, the current name makes the progression clearer: CCNA Cybersecurity at associate level and CCNP Cybersecurity for deeper investigation, forensics, threat hunting, and incident response work.
The certification is built around the work of a security operations analyst
The exam is best understood from the perspective of a security operations center. A SOC does not exist simply to collect alerts. Analysts have to decide which events matter, connect evidence from different sources, determine whether suspicious activity represents a real incident, and communicate what happened clearly enough that others can respond.
This makes the certification different from a broad security fundamentals credential. Candidates should understand networking and security concepts, but the emphasis is operational: observe, analyze, correlate, escalate, and document.
The SOC analyst role is therefore a useful lens for study. Every topic can be connected back to a question an analyst might need to answer during a live investigation.
Monitoring starts with knowing what normal looks like
Security monitoring is meaningful only when analysts can distinguish expected behavior from anomalies. A login at 9 a.m. from a known workstation may be ordinary. The same account authenticating from an unfamiliar location at 3 a.m., followed by large outbound transfers, deserves a different level of scrutiny.
Baselines do not have to be mathematically sophisticated. They can include expected authentication patterns, normal server-to-server communications, regular administrative activity, typical DNS behavior, ordinary traffic volumes, and known maintenance windows.
The challenge is that normal changes. New applications are deployed, employees travel, cloud services alter infrastructure, and software updates generate different traffic. Analysts need enough context to treat a baseline as evidence rather than an inflexible rule.
Network evidence tells a story across layers
Packets, flows, firewall logs, DNS records, proxy logs, and intrusion alerts describe different parts of the same activity. Candidates should understand how source and destination addresses, ports, protocols, TCP state, DNS queries, HTTP behavior, and encrypted sessions fit together.
A single denied firewall connection may mean very little. Repeated connection attempts across many hosts, followed by a successful session and unusual outbound traffic, may reveal scanning and compromise. The discipline lies in correlation.
ExamCollection’s material on network security logging supports this topic because infrastructure logs often provide the chronology needed to reconstruct how traffic moved through an environment.
Host-based analysis adds process and file context
Network monitoring cannot always explain what happened inside an endpoint. Host telemetry can expose process creation, parent-child relationships, file changes, registry activity, authentication events, service creation, scheduled tasks, command execution, and other evidence that clarifies intent.
For example, an outbound connection to an unfamiliar IP becomes more significant if it follows execution of a script spawned by a document process. A suspicious PowerShell command becomes more meaningful when it is followed by credential access or persistence activity.
Candidates should think in evidence chains rather than isolated indicators. One artifact may be benign; several related artifacts can form a coherent attack narrative.
Intrusion analysis requires protocol knowledge and skepticism
Intrusion-detection systems can identify patterns associated with attacks, but alerts are not verdicts. Signatures can generate false positives. Encrypted traffic can hide payloads. A known-bad pattern may appear in a harmless test. Analysts must evaluate the alert in context.
Protocol knowledge helps. If an alert references DNS tunneling, understand what normal DNS traffic looks like and why unusual query length, frequency, or encoding might matter. If the alert references web exploitation, understand request methods, response codes, headers, and session behavior. If it points to lateral movement, look for authentication and internal connection patterns that support the hypothesis.
The goal is not to memorize every attack signature. It is to reason about what evidence should exist if the alert is accurate.
Policies and procedures turn technical findings into repeatable response
A SOC that improvises every incident will be inconsistent. Security policies, escalation rules, severity definitions, communication procedures, evidence-handling requirements, and response playbooks create repeatability.
The article on cybersecurity policies and procedures is relevant because analysts need to know not only what happened but also what authority they have to act. Can they isolate an endpoint immediately? Must a manager approve account suspension? Who contacts legal or privacy teams? How is evidence preserved?
Good procedures are specific enough to guide action and flexible enough to handle incidents that do not match a perfect template.
Incident response is a cycle, not a single containment action
Incident response extends well beyond detection. Analysts help determine scope, contain activity, support eradication, verify recovery, and capture lessons for future prevention. The process also depends on preserving evidence and coordinating escalation across technical and business teams. Each phase can reveal new evidence that changes the earlier understanding of the incident.
Containment decisions also involve trade-offs. Disconnecting a compromised server may stop attacker activity but destroy volatile evidence or interrupt a critical business process. Leaving it online for observation may create additional risk. Analysts need to understand the technical and organizational consequences of their actions.
This is why documentation matters. A clear timeline and decision record allow responders to explain what was known, what was done, and why.
Zero trust changes the assumptions analysts make about location
Traditional security models often treated the internal network as more trustworthy than the internet. Cloud services, remote work, SaaS, mobile devices, and identity-based access have weakened that boundary. Analysts increasingly evaluate identity, device posture, application context, and behavior rather than relying heavily on network location.
The discussion of SASE and zero trust fits naturally here. For an analyst, zero trust means a connection from an internal IP should not automatically be treated as benign, and a remote connection should not automatically be treated as suspicious. Context determines risk.
Automation can reduce repetitive work, but judgment remains human
SOCs frequently automate enrichment, ticket creation, indicator lookup, containment workflows, and repetitive data gathering. Automation helps analysts spend less time copying information between systems and more time interpreting evidence.
The important distinction is between deterministic tasks and ambiguous decisions. A script can retrieve asset ownership or reputation data reliably. Deciding whether a pattern represents normal administration, insider misuse, or compromise may require business context that a simple workflow does not have.
Cisco’s broader automation direction, descended from the former DevNet Associate track, is increasingly relevant because security analysts who can work with APIs and structured data can scale their investigations more effectively.
Networking fundamentals remain one of the best advantages in cyber operations
Analysts who understand subnetting, routing, VLANs, NAT, DNS, DHCP, TCP sessions, VPNs, and common application protocols can interpret evidence faster. They know whether an address is private or public, whether a path should cross a firewall, whether a port matches the claimed service, and whether a connection pattern is plausible.
This creates a strong relationship with CCNA. CCNA is not a prerequisite for CCNA Cybersecurity, but networking depth makes intrusion analysis and troubleshooting much easier.
The same applies in the opposite direction: network engineers who develop security-analysis skills become better at recognizing when “a network problem” is actually malicious or policy-driven behavior.
Cisco’s certification focuses on the security-operations role through Cisco’s learning framework, but the skills overlap with broader security credentials. CompTIA Security+ provides broad foundational security coverage, while CompTIA CySA+ places greater emphasis on analysis and defensive operations.
These are not interchangeable certifications, and candidates do not need to collect all of them. The useful point is that identity, vulnerability management, logging, threat analysis, incident response, and network evidence are transferable across vendors.
Prepare by reconstructing incidents from evidence
Instead of studying every objective as an isolated definition, build short incident narratives. Start with a phishing event, malware execution, suspicious DNS traffic, credential misuse, or lateral movement. Ask what a firewall might record, what the endpoint might record, what authentication logs might show, what the network sensor might detect, and what action a playbook should trigger.
Practice explaining why one piece of evidence increases or decreases confidence in a hypothesis. That is more valuable than memorizing alert names. The certification rewards candidates who can connect technical observations to an operational decision.
The old CyberOps Associate name will continue to appear in search results and historical materials, but in September 2026 candidates should plan around the current CCNA Cybersecurity identity and current 200-201 blueprint. The enduring skill is not the brand name: it is the ability to turn noisy telemetry into a defensible account of what happened and what should happen next.
ExamCollection provides the complete prep materials in vce files format which include Cisco CyberOps Associate certification exam dumps, practice test questions and answers, video training course and study guide which help the exam candidates to pass the exams quickly. Fast updates to Cisco CyberOps Associate certification exam dumps, practice test questions and accurate answers vce verified by industry experts are taken from the latest pool of questions.


Cisco CyberOps Associate Video Courses
Top Cisco Certifications




Top Cisco Certification Exams
- 200-301
- 350-401
- 300-410
- 350-701
- 300-415
- 350-601
- 300-420
- 300-715
- 810-110
- 350-801
- 350-101
- 350-201
- 200-901
- 350-501
- 200-201
- 400-007
- 300-710
- 100-150
- 500-220
- 350-901
- 300-620
- 820-605
- 300-640
- 300-110
- 300-730
- 800-150
- 300-815
- 300-510
- 300-435
- 300-745
- 700-805
- 100-140
- 100-160
- 300-610
- 300-440
- 500-442
- 300-515
- 300-720
- 300-220
- 300-215
- 300-425
- 500-560
- 300-445
- 300-725
- 010-151
- 300-830
- 500-470
- 300-820
- 300-615
- 700-242
- 700-246
- 500-443
- 700-750
- 300-430
Site Search:



