



Premium File
212 Q&A
$76.99$69.99
Splunk SPLK-1001 Exam Questions & Answers, Accurate & Verified By IT Experts
Instant Download, Free Fast Updates, 99.6% Pass Rate
SPLK-1001 Premium File: 212 Questions & Answers
Last Update: Sep 18, 2026
SPLK-1001 Training Course: 28 Video Lectures
SPLK-1001 PDF Study Guide: 320 Pages
$79.99
Splunk SPLK-1001 Exam Screenshots
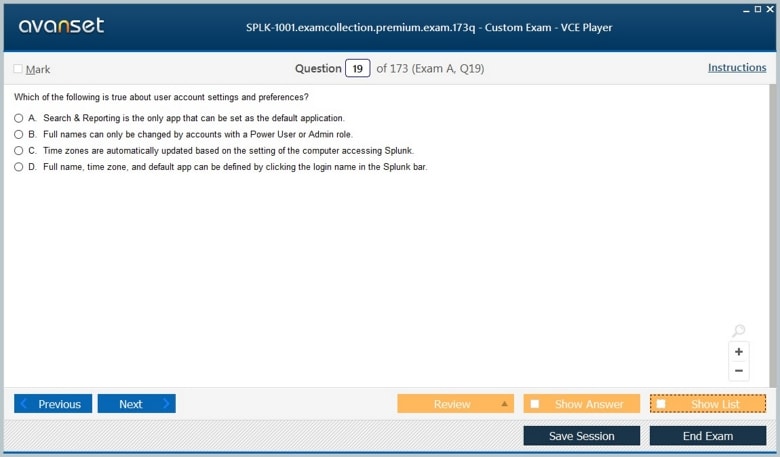
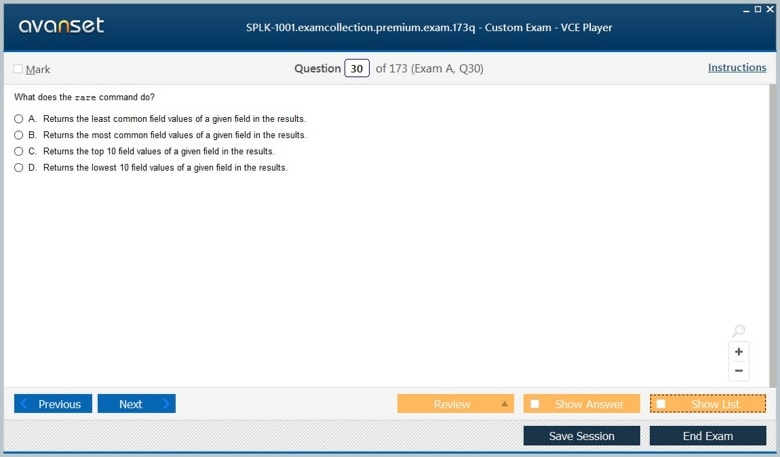
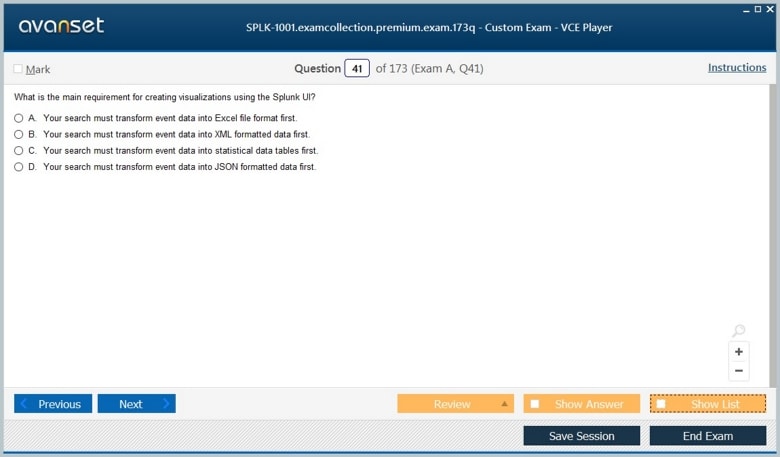
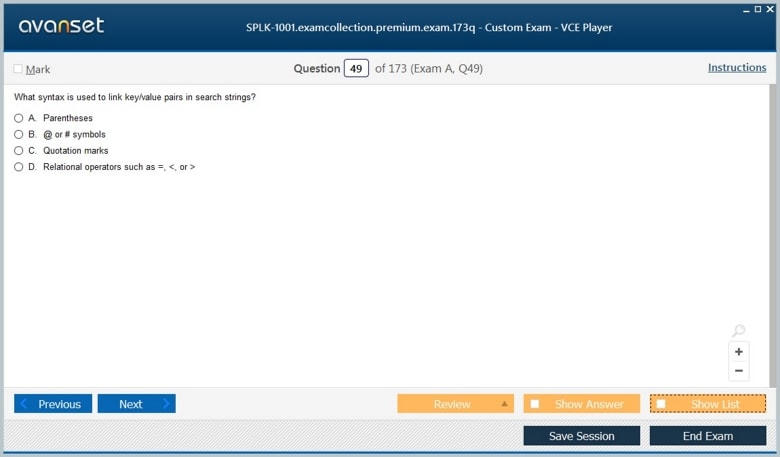
Splunk SPLK-1001 Practice Test Questions in VCE Format
| File | Votes | Size | Date |
|---|---|---|---|
File Splunk.testkings.SPLK-1001.v2026-08-02.by.limin.109q.vce |
Votes 1 |
Size 103.53 KB |
Date Aug 03, 2026 |
File Splunk.onlinetest.SPLK-1001.v2020-10-27.by.harley.99q.vce |
Votes 2 |
Size 91.84 KB |
Date Oct 27, 2020 |
File Splunk.examdumps.SPLK-1001.v2020-04-24.by.stanley.93q.vce |
Votes 2 |
Size 89.47 KB |
Date Apr 24, 2020 |
File Splunk.examlabs.SPLK-1001.v2020-02-07.by.zhangyan.89q.vce |
Votes 4 |
Size 81.44 KB |
Date Feb 07, 2020 |
File Splunk.Prep4sure.SPLK-1001.v2019-10-04.by.Bat.68q.vce |
Votes 4 |
Size 66.58 KB |
Date Oct 09, 2019 |
File Splunk.Actualtests.SPLK-1001.v2019-09-10.by.Owen.43q.vce |
Votes 3 |
Size 52.1 KB |
Date Sep 16, 2019 |
File Splunk.Testking.SPLK-1001.v2019-05-31.by.Roger.27q.vce |
Votes 3 |
Size 34.31 KB |
Date May 31, 2019 |
Splunk SPLK-1001 Practice Test Questions, Exam Dumps
Splunk SPLK-1001 (Splunk Core Certified User) exam dumps vce, practice test questions, study guide & video training course to study and pass quickly and easily. Splunk SPLK-1001 Splunk Core Certified User exam dumps & practice test questions and answers. You need avanset vce exam simulator in order to study the Splunk SPLK-1001 certification exam dumps & Splunk SPLK-1001 practice test questions in vce format.
SPLK-1001 is the exam code associated with Splunk Core Certified User, the optional entry point in Splunk’s certification program. Splunk currently describes the credential as proof that a candidate can navigate the platform, run basic searches, work with fields and lookups, create alerts, and build straightforward statistical reports and dashboards. That scope sounds introductory, but the exam is most useful when preparation focuses on how Splunk turns raw event data into searchable evidence rather than on memorizing interface labels.
The broader Splunk certification family branches quickly into power-user, administration, architecture, cloud, security, and service-intelligence roles. SPLK-1001 therefore matters less as a gatekeeper than as a clean foundation. A candidate who understands time ranges, field behavior, basic SPL pipelines, search modes, result interpretation, lookups, reports, and alerts has the mental model needed for every later Splunk role, even when the later work becomes more operational or architectural.
Splunk’s current Core Certified User track remains active and lists no prerequisites. It is designed for candidates with little or no prior Splunk experience, but that does not make it a vocabulary-only assessment. The strongest preparation uses a small dataset repeatedly: search it, narrow it, extract meaning from fields, summarize it, visualize it, save useful work, and ask what the results really say. The Splunk Core Certified User material is most valuable when read in that practical context.
Splunk is often introduced as a search platform for machine data, but candidates need a more concrete model. Events are stored in indexes and carry metadata such as host, source, and sourcetype in addition to fields found or extracted from the event content. Searches do not begin with a dashboard; they begin with selecting the right data and time range. If a search is aimed at the wrong index, source type, or time window, every later command can be syntactically correct and still produce a misleading result.
A useful exercise is to take one operational question and express it in progressively more precise searches. Start broadly enough to confirm the data exists, then constrain with index metadata and meaningful terms, then inspect fields before summarizing. This approach reduces the common beginner mistake of immediately adding statistical commands without first understanding what events are being matched. The ability to distinguish event selection from result transformation is one of the most durable Splunk skills.
Operational data is time-oriented, and Splunk search behavior reflects that. Candidates should understand relative and absolute time ranges, the difference between event time and when data arrives, and why a useful query can appear empty when the time picker is wrong. A five-minute incident investigation, a seven-day usage trend, and a monthly compliance review can use similar SPL while answering entirely different questions because their temporal boundaries change the evidence set.
Practice should include narrowing and widening the time window deliberately. When a spike appears, zoom into the minutes around it and compare the surrounding baseline. When a scheduled report is intended to summarize the previous day, reason about exactly which events belong in that window. Time discipline also prevents false conclusions when late-arriving data or timestamp parsing issues cause events to appear outside the period where an operator expects them.
Fields are the bridge between raw records and useful analysis. Some fields are available as metadata, some are extracted automatically, and others become meaningful through search-time knowledge. At the user level, candidates should be comfortable recognizing fields in results, selecting useful fields, understanding that field values vary across events, and using field constraints to focus a search. Fields make questions such as “which hosts fail most often?” or “which status code dominates?” possible without reading every raw line.
Field awareness also teaches healthy skepticism. A field name can exist while being absent from many events, populated inconsistently, or extracted differently across sourcetypes. Before building a report, inspect representative events and confirm that the field behaves as assumed. That habit becomes even more important at the SPLK-1002 power-user level, where reusable knowledge objects and richer data normalization depend on trustworthy field meaning.
Splunk’s Search Processing Language is easiest to learn as a pipeline. The initial search selects events; later commands transform, filter, enrich, or summarize the result set. A candidate should be able to look at a short pipeline and explain what each stage changes. That is more valuable than memorizing a long list of commands because unfamiliar searches can then be understood by tracing data through the pipe one operation at a time.
Basic statistical work should feel natural: count events, group by a field, calculate simple measures, sort results, rename fields for readability, and remove noise. The article on learning Splunk efficiently is relevant because command fluency grows faster when learners test small variations and inspect the result after each change instead of trying to write a complex query in one attempt.
Raw events often contain identifiers that are technically precise but operationally unhelpful. A code may represent a region, a product, a user category, or an ownership group. Lookups let Splunk enrich results by matching those values to external reference data. At the user level, the important idea is not the storage mechanics of every lookup type; it is recognizing when enrichment makes a search easier to interpret and when a missing match should be investigated rather than ignored.
For example, an event stream may contain device IDs while an operations team thinks in site names and support tiers. Enriching the data can make a report immediately useful to the people acting on it. Candidates should also understand that enrichment does not repair bad source data. If identifiers are inconsistent, a lookup can expose that problem but cannot magically create reliable joins. Good analysis depends on stable keys and clear ownership of reference information.
A report should begin with a question that deserves repeated answers. Saving a search is useful when it captures a stable analytical need; placing it on a dashboard is useful when several related views help someone monitor or investigate a situation. The visual layer should make comparisons easier, not hide uncertainty. A chart that compresses categories, changes scale unexpectedly, or uses an unsuitable time span can make correct search results harder to understand.
Candidates should practice choosing visualization forms based on the structure of the result. A single trend over time has different needs from a ranked category table. A dashboard panel should also have a meaningful title and a time context that readers can understand. These habits sound editorial, but they are part of accurate operations: visual presentation affects how quickly a person recognizes a pattern and whether the person interprets it correctly.
An alert converts a search condition into a signal that someone or something may need to act. The important reasoning question is what event pattern deserves interruption. A rule that fires on every minor error quickly becomes noise, while a rule that aggregates too much may hide an urgent condition. Even at an introductory level, candidates should understand scheduled versus real-time evaluation conceptually and recognize that thresholds, time windows, and result conditions determine usefulness.
Good alert design begins by defining the response. Who receives the signal? What evidence do they need? Is the condition actionable or merely interesting? These questions keep alert creation connected to operations. The same discipline later appears in security correlation searches and service-intelligence episodes, so SPLK-1001 is a good place to learn that detection quality depends as much on the question as on the syntax.
New users often want to reach a chart as quickly as possible. That skips the most instructive part of Splunk: reading representative raw events and learning how a source expresses success, failure, identity, location, duration, or state. The raw-log analysis mindset applies even outside security. If the analyst does not know what an event means, a clean statistical result can still be semantically wrong.
Use a small sample to identify recurring structure, exceptions, missing values, and changes in format. Then build the search that answers the operational question. This order makes troubleshooting easier because unexpected counts can be traced back to the events that produced them. It also prepares candidates for more advanced work where field extraction, normalization, and data-quality decisions determine whether downstream dashboards and detections can be trusted.
For SPLK-1001, success should mean being able to explain a result from source event to final visualization. Given a search, a candidate should know which data was selected, how time limited it, which fields were used, what each command changed, and why the final report answers the stated question. That end-to-end explanation is a better readiness test than remembering every menu path because interfaces evolve while the analytical model remains stable.
After the user-level credential, the natural progression is the Splunk Core Certified Power User track, where the same foundations become reusable knowledge objects, richer field handling, data models, macros, and more capable searches. Candidates who build careful habits at SPLK-1001 enter that next stage with fewer conceptual gaps and can spend their effort on deeper techniques rather than relearning what their data actually represents.
Go to testing centre with ease on our mind when you use Splunk SPLK-1001 vce exam dumps, practice test questions and answers. Splunk SPLK-1001 Splunk Core Certified User certification practice test questions and answers, study guide, exam dumps and video training course in vce format to help you study with ease. Prepare with confidence and study using Splunk SPLK-1001 exam dumps & practice test questions and answers vce from ExamCollection.
Purchase Individually
Splunk SPLK-1001 Video Course
Top Splunk Certifications

Top Splunk Certification Exams
Site Search:

SPECIAL OFFER: GET 10% OFF

Pass your Exam with ExamCollection's PREMIUM files!
SPECIAL OFFER: GET 10% OFF
Use Discount Code:
MIN10OFF
A confirmation link was sent to your e-mail.
Please check your mailbox for a message from support@examcollection.com and follow the directions.

Download Free Demo of VCE Exam Simulator
Experience Avanset VCE Exam Simulator for yourself.
Simply submit your e-mail address below to get started with our interactive software demo of your free trial.
Pass the exam SPLK-1001
Premium is valid, no new question.
i love answering all the SPLK-1001 practice questions and answers here because they are very similar to the ones ive answered in my real test!!! wouldn’t mind using their other files in the future! :D
WILL I BE USING THEIR VCE FILES AGAIN? DEFINITELY YES!! BASED ON MY PERSONAL EXPERIENCE THEIR MATERIALS ARE MORE RELIABLE COMPARED TO OTHER WEBSITES. I GOT MORE THAN THE PASSING SCORE FOR MY EXAM WITH THE HELP OF THEIR SPLK-1001 DUMPS!
@Kazuko ill also be taking my exam in a couple of weeks and im hoping for the best. i just had a hard time transporting the files to the vce exam player but overall their splk-1001 braindumps are really up to date and useful for my preparation.
@Harper-Rosue Wow!! I hope ill also pass splunk test this week. I already answered some of their vce files for SPLK-1001 exam and so far the free exam questions are very informative. Crossed fingers!!
Im now Splunk Core Certified User!!! Ive been using examcollection vce files for quite some time and I can say that their files are really worth it! ive tried other resources but those wer not so good materials.SPLK-1001 exam dumps are definitely a must try for those wanting to pass their exam!
@Vivaan2266 hi there! their SPLK-1001 vce files are surprisingly very easy to use! just dont forget to also download vce exam simulator which will run the files. you will be guided when using the vce player so nothing to worry !
successfully downloaded their free questions and answers for splk-1001 exam. any tips on how to use it?? this is actually my first time trying their materials and i dont have enough time bec my splunk exam would be next week. tnxx.