
Pass Your Splunk Core Certified Power User Certification Easy!
Splunk Core Certified Power User Certification Exams Questions & Answers, Accurate & Verified By IT Experts
Instant Download, Free Fast Updates, 99.6% Pass Rate.
Splunk Core Certified Power User Certification Exams Screenshots
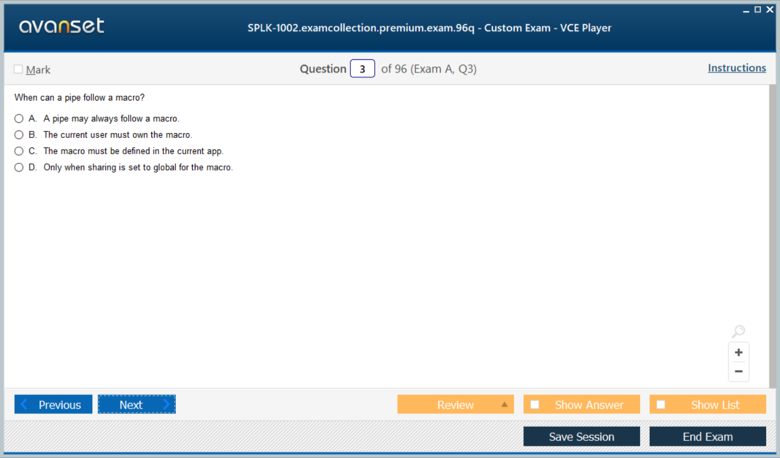
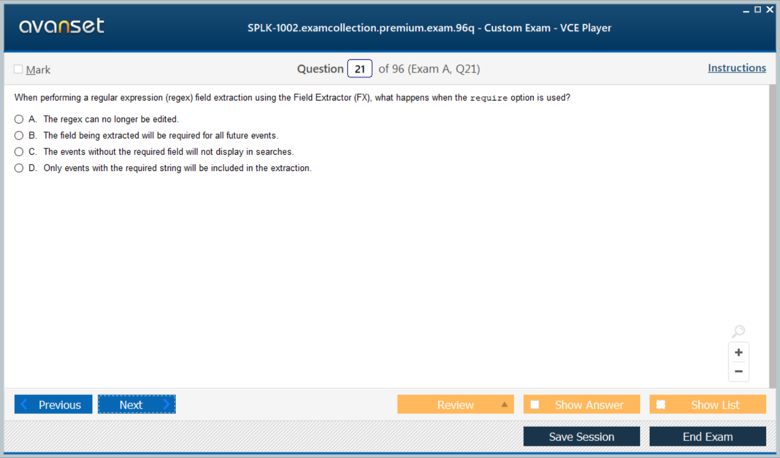
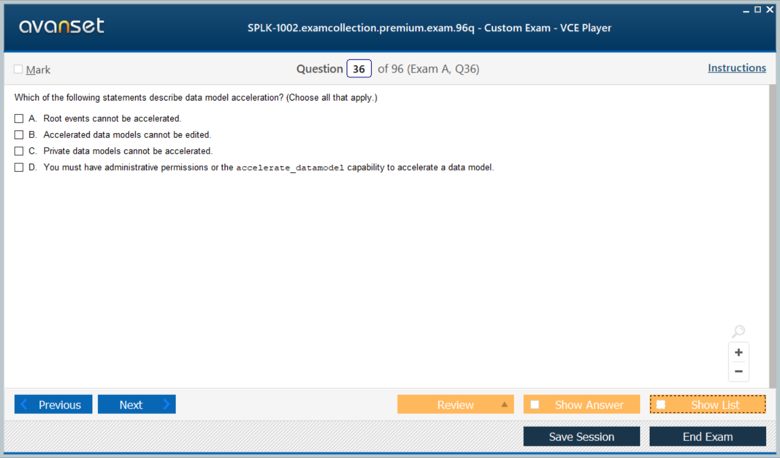
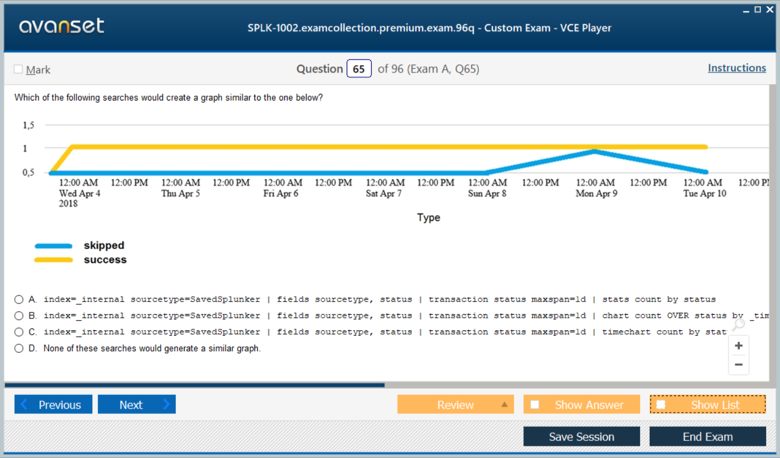
Splunk Core Certified Power User Product Reviews
Download Free Splunk Core Certified Power User Practice Test Questions VCE Files
| Exam | Title | Files |
|---|---|---|
Exam SPLK-1002 |
Title Splunk Core Certified Power User |
Files 3 |
Splunk Core Certified Power User Certification Exam Dumps & Practice Test Questions
Prepare with top-notch Splunk Core Certified Power User certification practice test questions and answers, vce exam dumps, study guide, video training course from ExamCollection. All Splunk Core Certified Power User certification exam dumps & practice test questions and answers are uploaded by users who have passed the exam themselves and formatted them into vce file format.
Splunk Core Certified Power User: From Search Commands to Reusable Knowledge
Splunk Core Certified Power User is an entry-level certification with a deceptively broad practical target: move beyond one-off searches and become someone who can shape events into reusable knowledge, reports, visualizations, correlations, and data models. Splunk’s current certification page lists no prerequisite, a 60-minute exam, and 65 multiple-choice questions. That makes time management relevant, but the more important preparation challenge is learning to recognize what a search pipeline is doing at each stage and which Splunk object should carry logic that will be reused.
The credential sits above basic user fluency while still remaining close to everyday investigation and reporting. The Splunk Core Certified User level focuses on foundational navigation, searching, fields, lookups, alerts, reports, and dashboards. Power User adds greater depth in transforming commands, event correlation, field manipulation, knowledge objects, data models, and normalization. That progression is useful because it shows what the exam is really testing: not just whether you can find events, but whether you can make the search environment more consistent and reusable for others.
The best way to prepare is to work in Splunk. Read raw events, build searches incrementally, inspect fields, deliberately create broken searches, and compare several ways to answer the same question. Each lab should end with an explanation of why the chosen command or knowledge object is appropriate. That reasoning is what survives when the exam scenario changes its field names, sourcetypes, or business context.
Search pipelines become easier when you know what each command does to the result set
Splunk Processing Language is read left to right, but not every command behaves the same way. Some commands filter events, some create or transform fields, some aggregate many events into a smaller result table, and some reshape output for presentation. Power User preparation should build an instinct for the current shape of the data after every pipe. Start with a broad search, add a time range, inspect fields, filter with search or where, calculate a value with eval, aggregate with stats, and then transform the result for a chart. Predict the number and form of rows before you run the next command. That habit prevents a common error: writing syntactically valid SPL that has already discarded the detail needed later in the pipeline.
Transforming commands are not just reporting tools; they change the analytical unit
Commands such as stats, chart, and timechart turn streams of events into aggregated results. The current Power User blueprint explicitly includes transforming commands for visualizations, so candidates should understand grouping fields, aggregation functions, time buckets, split-by fields, and the difference between event-level and summarized data. Build the same question three ways: total errors by host, errors over time, and errors over time split by application. Then explain why each output has a different row structure and what question it answers. When a downstream command expects raw events but receives an aggregate table, the problem is conceptual rather than syntactic. Recognizing that transition is central to reliable Splunk work.
Filtering and calculated fields should make searches clearer, not merely shorter
Power Users need fluency with eval, search, where, fillnull, field aliases, calculated fields, and related techniques for shaping data. The key distinction is when logic belongs in a particular search and when it should become reusable knowledge. If several teams repeatedly calculate the same normalized status, a calculated field or other knowledge object may be better than copying eval expressions into every report. If a filter depends on an aggregate result, where may be appropriate after the transformation. Practice by writing a search that normalizes inconsistent source values, handles missing fields, computes a duration, and filters on the derived result. Then decide which parts should remain local and which would be safer as shared knowledge.
Correlation is about defining what belongs together and over what boundary
Splunk can correlate events by fields, time, transactions, and other patterns. The Power User blueprint gives event correlation significant weight, so candidates should understand why grouping decisions matter. A login followed by a privilege change may be related by user, host, session, and time window; choosing the wrong key can merge unrelated activity or split one real sequence into several fragments. Transaction is useful in some cases but can be more expensive or less flexible than stats-based approaches. Build exercises where the same events are correlated using different fields and time constraints, then inspect what changes. The goal is to reason about identity, sequence, and boundaries rather than memorize a transaction command template.
Knowledge objects are how a Power User turns personal search skill into team leverage
Event types, tags, field aliases, calculated fields, lookups, macros, saved searches, reports, and other knowledge objects let Splunk encode meaning above raw data. A Power User should understand both creation and governance: naming, permissions, scope, dependency, and the risk of hiding important logic in objects that other users cannot discover. The broader Splunk learning path becomes more useful when each object is tied to a reason. A lookup can enrich events with business context; a macro can centralize repeated SPL; an event type can label recurring search conditions; a tag can create cross-source meaning. The exam may ask what object solves a scenario, so study the purpose and side effects of each one.
Data models and normalization create a common analytical surface across inconsistent sources
Large Splunk environments rarely receive perfectly consistent fields from every system. Data models and normalization concepts help analysts work with shared structures even when underlying sources differ. Power User preparation should connect field aliases, tags, calculated fields, event types, and data models to the idea of common semantics. If three security products call the source address src_ip, source, and clientAddress, a normalized model should let a downstream search ask one consistent question. Practice mapping heterogeneous sample data into a common set of fields and then build a report that no longer cares which source produced the event. That exercise demonstrates why normalization is an information-architecture problem, not just an exam vocabulary item.
Dashboards, reports, and workflow actions should lead a user toward a decision
A dashboard is successful when it helps someone notice and act, not when it contains the largest number of panels. Power Users should understand how searches feed reports and visualizations, how tokens or interactions can narrow context where applicable, and how workflow actions can connect a Splunk event to an external operational step. Start with one question such as “Which services are failing the response-time objective?” and build a small dashboard around the decision. Every panel should add evidence: trend, breakdown, affected entities, or drilldown detail. If two panels show the same story in different chart types, remove one. This design habit also improves exam reasoning because it forces you to separate data transformation from presentation.
Permissions and object scope determine whether a correct solution is usable by the intended audience
A search can be perfect for its creator and useless to everyone else if the underlying knowledge objects are private, scoped incorrectly, or dependent on inaccessible resources. Power User study should include the practical difference between personal and app-level knowledge, sharing, ownership, and how object permissions affect reuse. When a report works for one analyst but fails for a teammate, inspect not only the SPL but also the availability of lookups, macros, field extractions, and roles. This is a valuable bridge from analytical work toward administration because it reveals that reusable Splunk content has lifecycle and governance requirements in addition to search logic.
Preparation should move from command drills to complete investigation workflows
The current exam gives 60 minutes for 65 questions, so you need fast recognition of command purpose and object relationships. Short quizzes help, but lab sequences create stronger memory. Ingest or use sample data, run searches, transform results, create an event type, add a tag, build a lookup, define a macro, produce a report, and then normalize the same information into a data model. Compare your work with the skills progression toward deeper Splunk expertise. After Power User, candidates who manage platform health can move toward Splunk Enterprise Certified Admin, while Splunk also offers an Advanced Power User credential for deeper search and dashboard work.
Use the Splunk certification family to keep the role boundary clear. Power User is still primarily about using and structuring Splunk knowledge, not owning every deployment, indexer, forwarder, or infrastructure decision. That distinction makes study more efficient because you can go deep on SPL and knowledge objects without turning the plan into an administrator syllabus.
A prepared Power User can explain not only what a search returns, but how the pipeline produced it, why the fields mean what they mean, where reusable logic should live, and how another analyst can safely use the result. Build that competence in labs and the exam becomes a test of familiar patterns rather than a memory challenge about isolated commands.
For final review, make a small “command-to-question” sheet rather than a dictionary. Put a business question on the left—compare categories over time, keep only rows that meet a calculated condition, correlate events into sessions, enrich events from a lookup—and write the Splunk construct that solves it on the right. Then reverse the exercise: given a command or object, state what kind of problem it is suited to solve and what data shape it expects. This two-way recall is faster under exam pressure than memorizing syntax without purpose.
ExamCollection provides the complete prep materials in vce files format which include Splunk Core Certified Power User certification exam dumps, practice test questions and answers, video training course and study guide which help the exam candidates to pass the exams quickly. Fast updates to Splunk Core Certified Power User certification exam dumps, practice test questions and accurate answers vce verified by industry experts are taken from the latest pool of questions.


Splunk Splunk Core Certified Power User Video Courses
Top Splunk Certifications

Top Splunk Certification Exams
Site Search:



