



Premium File
108 Q&A
$76.99$69.99
Citrix 1Y0-341 Exam Questions & Answers, Accurate & Verified By IT Experts
Instant Download, Free Fast Updates, 99.6% Pass Rate
108 Questions & Answers
Last Update: Oct 09, 2026
$69.99
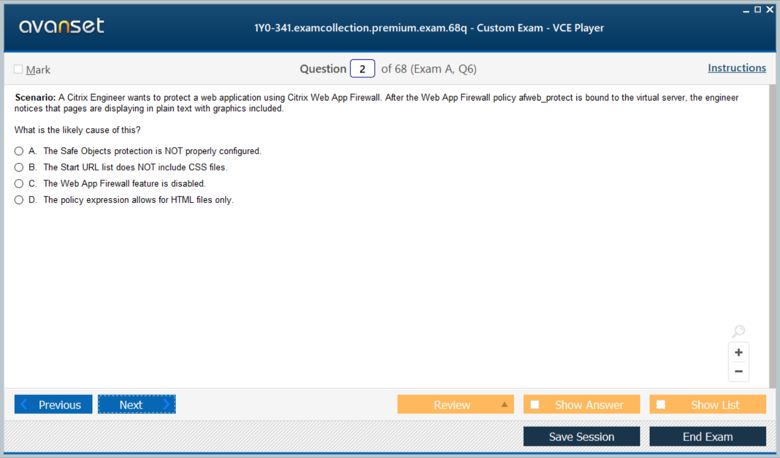
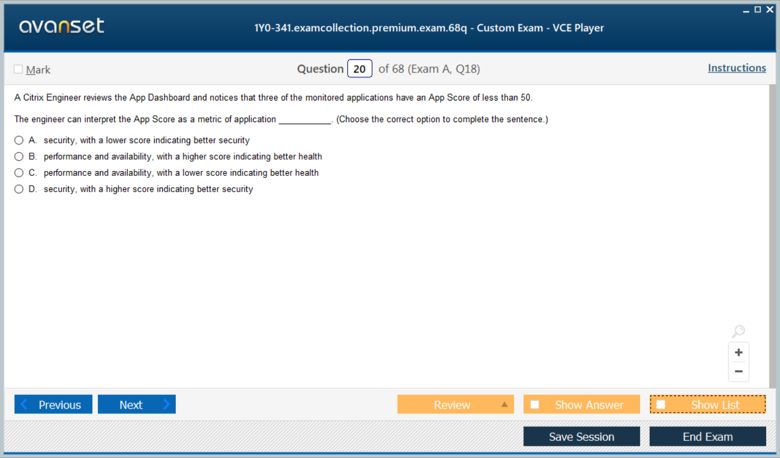
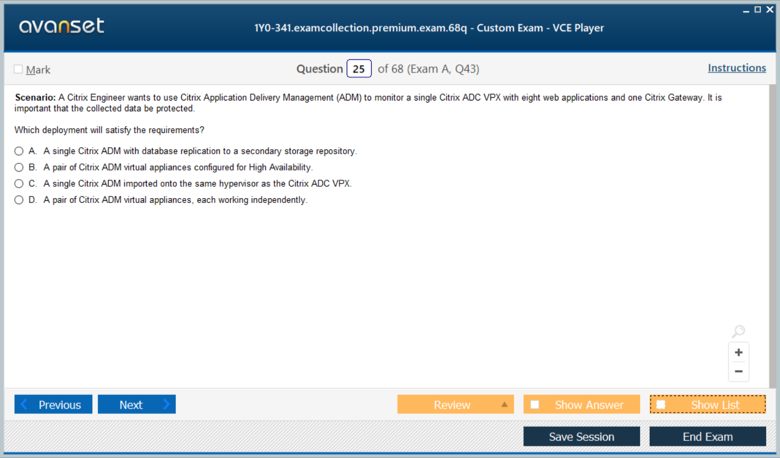
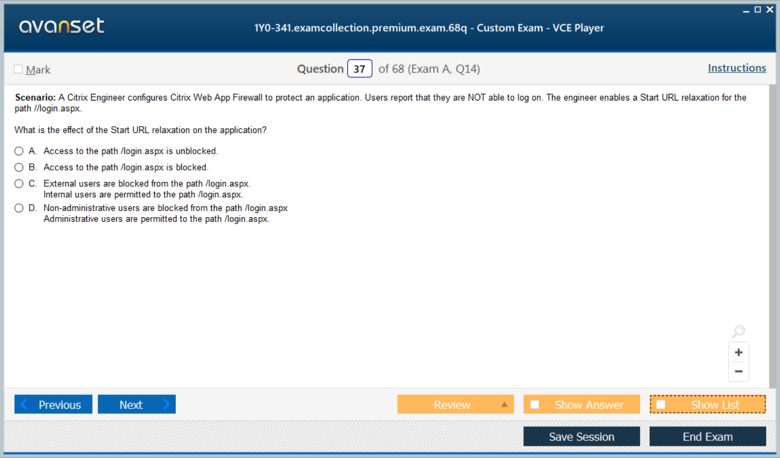
Citrix 1Y0-341 Exam Screenshots
Citrix 1Y0-341 Practice Test Questions in VCE Format
| File | Votes | Size | Date |
|---|---|---|---|
File Citrix.test4prep.1Y0-341.v2026-10-06.by.lijing.37q.vce |
Votes 1 |
Size 58.56 KB |
Date Oct 06, 2026 |
File Citrix.actualtests.1Y0-341.v2021-01-16.by.freya.30q.vce |
Votes 1 |
Size 46.92 KB |
Date Jan 16, 2021 |
Citrix 1Y0-341 Practice Test Questions, Exam Dumps
Citrix 1Y0-341 (Citrix ADC Advanced Topics - Security, Management, and Optimization) exam dumps vce, practice test questions, study guide & video training course to study and pass quickly and easily. Citrix 1Y0-341 Citrix ADC Advanced Topics - Security, Management, and Optimization exam dumps & practice test questions and answers. You need avanset vce exam simulator in order to study the Citrix 1Y0-341 certification exam dumps & Citrix 1Y0-341 practice test questions in vce format.
Citrix 1Y0-341, Citrix ADC Advanced Topics: Security, Management and Optimization, represented the professional networking layer for ADC 13. Its blueprint concentrated on Web App Firewall, advanced authentication and authorization, Application Delivery Management, security controls, and traffic optimization. Those are still important professional skills, but Citrix’s current 2025 professional App Delivery and Security guide now identifies 1Y0-342 for the NetScaler 14.x generation.
That makes 1Y0-341 a transition page rather than a page that should be read as proof of the current exam identity. Citrix continues to host the older preparation guide, which is useful for understanding the ADC 13-era objectives, while the current professional guide uses new NetScaler branding and updated platform terminology. Candidates should preserve the security concepts and discard the assumption that the older code is necessarily what they should schedule today.
Citrix certifications help place the code in context. Associate-level traffic management, historically represented by 1Y0-241, builds the delivery foundation; 1Y0-341 moved into advanced protection, management, and optimization where configuration mistakes can affect both security and availability.
A WAF protects web applications by evaluating HTTP requests and responses against security rules. It can detect patterns associated with SQL injection, cross-site scripting, malformed requests, protocol violations, and other application-layer attacks. The difficult part is that legitimate applications also send unusual payloads, custom headers, encoded data, APIs, file uploads, and framework-specific traffic that can resemble attack patterns.
Professional administration therefore requires more than enabling every signature. The engineer has to understand learning, relaxation, policy bindings, enforcement mode, logging, and the operational effect of false positives. A WAF should move from observation to enforcement through controlled tuning. The general article on web application firewall protection provides useful conceptual context for why application-aware inspection differs from a traditional network firewall.
If a security control blocks legitimate checkout, authentication, API, or business-workflow traffic, the organization may disable the control under pressure. That can create a larger security gap than a carefully tuned policy would have. Administrators should therefore capture the exact request that triggered a violation, identify which rule matched, and decide whether the traffic is valid before creating an exception.
Relaxations need narrow scope. A global bypass for a parameter, URL, or signature may solve the immediate incident but allow malicious input elsewhere. Test the smallest change that permits the expected application behavior, retain logging, and review the exception after application releases. Understanding WAF evasion methods also helps explain why broad exclusions are dangerous: attackers deliberately search for parsing gaps and alternate encodings that weaken enforcement.
Authentication proves identity, authorization decides what that identity can access, and auditing records the resulting activity. In an ADC environment these functions can involve LDAP, RADIUS, SAML, certificates, nFactor-style authentication flows, session policies, and application-specific authorization. The design should identify trust boundaries and failure behavior rather than treating authentication as one checkbox.
Complex authentication flows are best represented as sequences. Which factor runs first? What condition selects the next factor? Which attribute becomes available for authorization? What happens if an identity provider is unavailable? Troubleshooting then follows the same sequence, using logs and traces to determine which stage failed. This is more reliable than changing multiple policy bindings until users can log in again.
Advanced application delivery requires deliberate choices about protocols, ciphers, certificates, key protection, and whether traffic is re-encrypted to the origin. A secure front end can still expose risk if the back-end connection is unencrypted across an untrusted network or if weak protocol choices are accepted for compatibility without a documented reason.
Certificate operations also create availability risk. Expired certificates, missing intermediate certificates, mismatched private keys, and incorrect bindings can take a protected application offline instantly. Professional administrators need monitoring for expiry and a controlled replacement process. Security posture and uptime improve together when certificates are treated as managed infrastructure rather than files that are replaced manually during an emergency.
Citrix Application Delivery Management, now reflected in newer NetScaler management terminology, centralizes visibility and operational control across appliances. It can help with inventory, analytics, configuration, events, and application behavior. Centralization is valuable because trends across multiple devices are difficult to recognize when each appliance is managed independently.
The management plane itself needs security. Administrative roles should follow least privilege, credentials should be protected, and automation or configuration jobs should have clear change ownership. A centralized tool can distribute a good configuration quickly, but it can distribute a bad one just as quickly. Change review and rollback planning therefore become more important as the scale of management increases.
Compression, caching, connection reuse, TCP optimization, and related features can improve delivery efficiency, but they can also complicate troubleshooting if enabled without a clear objective. The administrator should understand which bottleneck a feature addresses and how success will be measured. Faster page load, reduced server connection count, lower bandwidth use, or improved latency should be observable rather than assumed.
Optimization also interacts with application behavior. Caching dynamic or sensitive content incorrectly can create functional or security problems. Compression can change resource usage on the appliance. Connection multiplexing may alter how the origin server sees clients. Advanced practitioners need to evaluate those tradeoffs and keep enough telemetry to reverse a change if the expected benefit does not appear.
A blocked request is useful evidence only if the team can determine which policy caused the block and why. WAF violations, authentication failures, certificate errors, responder actions, and system events should be collected with timestamps and enough context to correlate them with user reports. Packet traces remain valuable because they show what actually crossed each connection boundary.
Good incident handling preserves the difference between a security detection and a confirmed attack. A signature match may be malicious, a false positive, or a malformed but harmless request. The team should use logs, application context, source behavior, and repeated patterns to establish confidence. That discipline reduces both overreaction and the temptation to silence noisy controls without understanding them.
Content switching and responder policies also intersect with security. A responder can block, redirect, or transform handling before a request reaches the application, while content switching can separate applications behind a shared address. These features are useful for reducing exposure and enforcing canonical request paths, but broad expressions can create unexpected matches. Policies should be reviewed with representative traffic and a clear default behavior.
Rate controls and bot-like traffic patterns are another area where application delivery and security meet. An overloaded login or search endpoint may need protection even when requests are syntactically valid. Administrators should distinguish malicious automation from legitimate bursts and understand which layer—WAF, responder policy, application control, or upstream service—is best positioned to enforce the limit.
Backup and recovery of security configuration are easy to overlook. WAF relaxations, authentication policies, certificate bindings, and management settings may represent months of operational tuning. Configuration export, documented dependencies, and tested recovery procedures help ensure that a replacement appliance does not restore only the basic virtual servers while silently losing the controls that made the service secure.
Finally, version upgrades should be treated as security changes, not routine restarts. Signature behavior, supported ciphers, policy syntax, management integration, and default settings can change between releases. A lab or staged upgrade should validate both legitimate application workflows and expected blocking behavior before production traffic is moved to the new version.
Administrative access deserves the same security attention as protected applications. Management interfaces should be reachable only from controlled networks, administrator roles should match job responsibility, and authentication should avoid shared accounts. Configuration changes need attribution because a WAF or authentication incident is much harder to reconstruct when the team cannot determine who changed a policy or certificate binding.
Security teams should also monitor the protected application after policy deployment. A reduction in blocked attacks may mean traffic became cleaner, but it can also mean a rule stopped matching after an application update. Trend review, sample validation, and periodic controlled testing help prove that the enforcement layer is still seeing and handling the threats it was designed to stop.
A final operational concern is backup validation. A saved configuration is useful only when certificates, keys, policy objects, and dependent files can be restored together. Teams should periodically test recovery on a non-production appliance so that a hardware failure does not reveal that the backup omitted the very security objects the service depends on.
The current 1Y0-342 professional guide still emphasizes Web App Firewall, authentication and application security, management, and optimization, but it is written for NetScaler 14.x and current product terminology. Someone who studied 1Y0-341 already has a strong conceptual base, yet should update configuration details, interface workflows, supported features, and the current exam structure before attempting the modern professional certification.
The safest planning rule is simple: use 1Y0-341 to understand the ADC 13 generation and use the current Citrix preparation guide to determine what is examinable now. The value of the older exam lies in the security reasoning it required—understand the application, enforce narrowly, collect evidence, and optimize without weakening protection. Those habits transfer directly even when the exam code and product name change.
Go to testing centre with ease on our mind when you use Citrix 1Y0-341 vce exam dumps, practice test questions and answers. Citrix 1Y0-341 Citrix ADC Advanced Topics - Security, Management, and Optimization certification practice test questions and answers, study guide, exam dumps and video training course in vce format to help you study with ease. Prepare with confidence and study using Citrix 1Y0-341 exam dumps & practice test questions and answers vce from ExamCollection.
Purchase Individually
Top Citrix Certifications
Site Search:

SPECIAL OFFER: GET 10% OFF

Pass your Exam with ExamCollection's PREMIUM files!
SPECIAL OFFER: GET 10% OFF
Use Discount Code:
MIN10OFF
A confirmation link was sent to your e-mail.
Please check your mailbox for a message from support@examcollection.com and follow the directions.

Download Free Demo of VCE Exam Simulator
Experience Avanset VCE Exam Simulator for yourself.
Simply submit your e-mail address below to get started with our interactive software demo of your free trial.