



Premium File
420 Q&A
$76.99$69.99
Palo Alto Networks PCNSA Exam Questions & Answers, Accurate & Verified By IT Experts
Instant Download, Free Fast Updates, 99.6% Pass Rate
PCNSA Premium File: 420 Questions & Answers
Last Update: Sep 24, 2026
PCNSA Training Course: 77 Video Lectures
PCNSA PDF Study Guide: 803 Pages
$79.99
Palo Alto Networks PCNSA Exam Screenshots
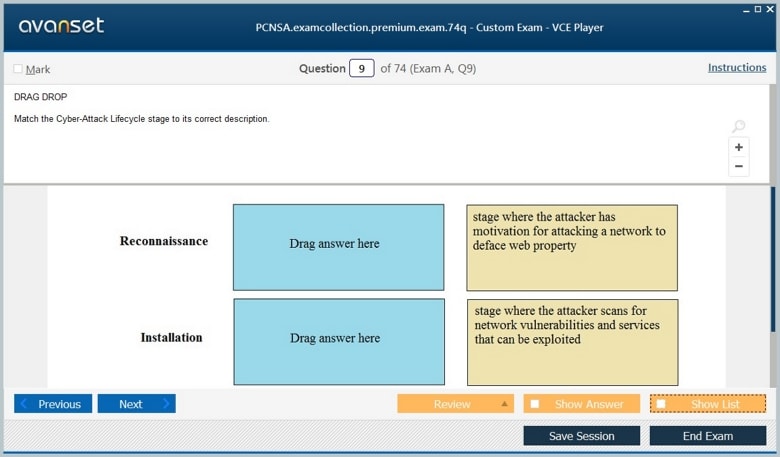
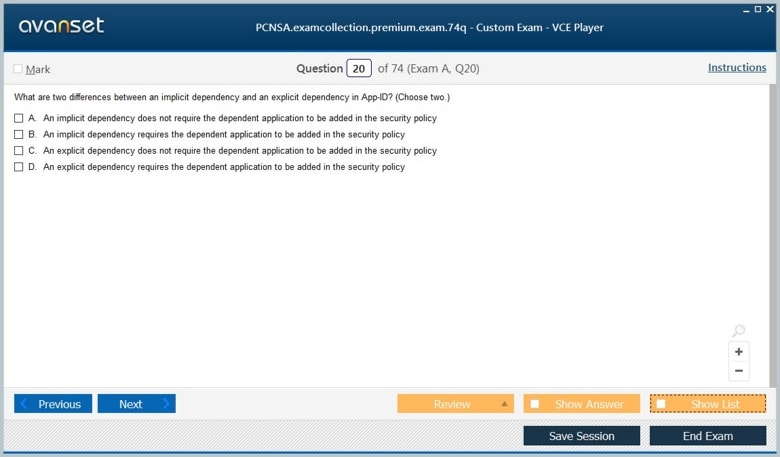
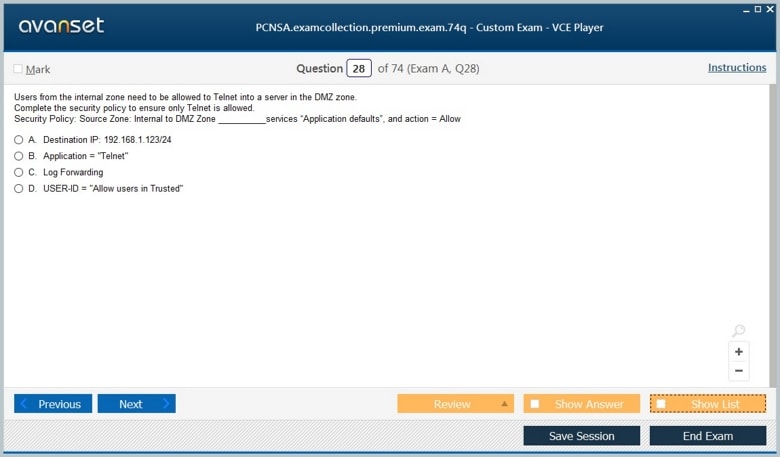
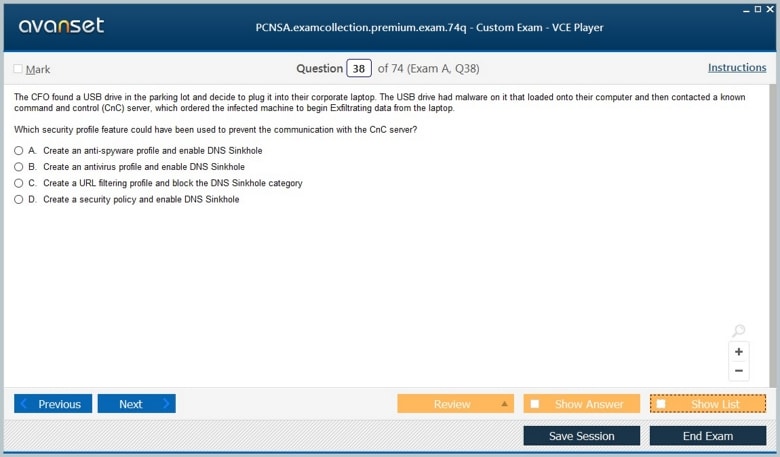
Palo Alto Networks PCNSA Practice Test Questions in VCE Format
| File | Votes | Size | Date |
|---|---|---|---|
File Palo Alto Networks.test4prep.PCNSA.v2026-08-20.by.liuwei.106q.vce |
Votes 1 |
Size 2.06 MB |
Date Aug 20, 2026 |
File Palo Alto Networks.onlinetest.PCNSA.v2022-01-04.by.archie.93q.vce |
Votes 1 |
Size 2.29 MB |
Date Jan 04, 2022 |
File Palo Alto Networks.prep4sure.PCNSA.v2021-10-20.by.wangxiuying.85q.vce |
Votes 2 |
Size 2.86 MB |
Date Oct 20, 2021 |
File Palo Alto Networks.braindumps.PCNSA.v2021-08-02.by.marc.68q.vce |
Votes 1 |
Size 1.13 MB |
Date Aug 02, 2021 |
File Palo Alto Networks.passit4sure.PCNSA.v2021-04-27.by.darcie.62q.vce |
Votes 1 |
Size 1.4 MB |
Date Apr 28, 2021 |
File Palo Alto Networks.realtests.PCNSA.v2020-10-01.by.willow.39q.vce |
Votes 2 |
Size 449.62 KB |
Date Oct 01, 2020 |
File Palo Alto Networks.Prep4sure.PCNSA.v2019-09-11.by.Brant.38q.vce |
Votes 5 |
Size 544.53 KB |
Date Sep 16, 2019 |
File Palo Alto Networks.Braindumps.PCNSA.v2019-04-13.by.Seb.26q.vce |
Votes 5 |
Size 1.04 MB |
Date Apr 14, 2019 |
Palo Alto Networks PCNSA Practice Test Questions, Exam Dumps
Palo Alto Networks PCNSA (Palo Alto Networks Certified Network Security Administrator) exam dumps vce, practice test questions, study guide & video training course to study and pass quickly and easily. Palo Alto Networks PCNSA Palo Alto Networks Certified Network Security Administrator exam dumps & practice test questions and answers. You need avanset vce exam simulator in order to study the Palo Alto Networks PCNSA certification exam dumps & Palo Alto Networks PCNSA practice test questions in vce format.
The PCNSA exam was Palo Alto Networks’ Network Security Administrator certification. It retired on January 31, 2025 as the company moved toward role-based certifications. That retirement ended new PCNSA testing, but it did not make the underlying administration skills obsolete. PAN-OS policy, interfaces, routing, NAT, security profiles, user context, logging, and centralized operations remain central to network-security work.
Palo Alto Networks now distributes those skills across current roles. The Network Security Professional covers broad platform knowledge and entry-level operations, the Network Security Analyst focuses on policy, objects, centralized management, posture, and troubleshooting, and the Next-Generation Firewall Engineer goes deeper into PAN-OS networking, device settings, integration, automation, policy, and NGFW operation. None should be described as PCNSA under a new name.
The right way to use old PCNSA material is therefore selective. Keep the packet-flow reasoning and administrative discipline. Recheck product interfaces, supported features, management architecture, software lifecycle practices, and certification logistics against the current Palo Alto Networks certifications. The durable value lies in understanding how traffic becomes a security decision.
A security policy cannot work if traffic never reaches the expected interface or follows the expected route. Administrators should be able to identify ingress and egress interfaces, security zones, virtual routers, next hops, and return paths before they touch policy. Many apparent firewall-policy failures are routing, addressing, or path-asymmetry problems.
Zones provide a security boundary that is more stable than individual addresses. Good designs group interfaces by trust and function without creating dozens of arbitrary zones that make policy unreadable. The administrator should understand how a flow changes when an interface is moved, a tunnel is introduced, or a routing decision sends traffic through a different egress zone.
Path verification should include return traffic. A session may be allowed outbound yet fail because the return route bypasses the firewall or lands on a different device. Administrators who reason bidirectionally are less likely to solve symptoms with unnecessary policy exceptions.
Interface types also influence behavior. Layer 3, Layer 2, virtual wire, tunnel, loopback, and aggregate interfaces participate in policy and forwarding differently. A learner does not need to memorize every niche deployment, but should understand that the security zone and routing context are determined by interface design, not by the device name printed on a diagram.
When multiple virtual systems or routing contexts are used, troubleshooting must stay inside the correct logical scope. An engineer who checks the global route table while the session belongs to another virtual router can draw the wrong conclusion from perfectly accurate commands.
Rules are easier to maintain when they answer who is communicating, what application is required, where the traffic is going, and why the access exists. Broad source-any to destination-any rules may make an outage disappear, but they create long-term risk and hide the actual dependency that should be authorized.
App-ID and User-ID add context beyond ports and IP addresses. Applications can use dynamic ports or tunnel inside common protocols, while user identity lets policy follow people rather than only subnets. Administrators need to understand how application identification evolves during a session and how identity mapping quality affects rule behavior.
Rule order matters because earlier matches can shadow later intent. Before reorganizing a rulebase, use hit counts, logs, and ownership information. A clean-looking policy set is not automatically a correct one if legitimate flows are hidden behind broad exceptions or if unused-looking rules support rare operational events.
Source and destination NAT change the addresses seen at different points in a session. Administrators should be able to state the original source, original destination, translated source, translated destination, ingress zone, and egress zone for an expected flow. If those values are vague, NAT troubleshooting becomes guesswork.
Policy evaluation and NAT interaction can confuse new administrators because the firewall uses specific pre- and post-translation values at different stages. A useful practice is to draw the packet before translation, the selected NAT rule, and the packet after translation. Then compare that expected path with session and traffic-log evidence.
Overlapping rules and service settings can create subtle errors. A more general NAT rule may match before a specific one, or a translated service may not align with the application behavior expected by security policy. Change one variable at a time and verify the session table rather than repeatedly editing multiple rules.
An allow rule only permits communication; security profiles determine how that permitted traffic is inspected. Antivirus, anti-spyware, vulnerability protection, URL controls, file analysis, DNS protection, and other services add different forms of detection and enforcement. Administrators should understand what evidence each control sees and what action it can take.
Encrypted traffic creates a visibility tradeoff. TLS decryption can expose threats and data that would otherwise be opaque, but deployment must account for privacy, legal requirements, certificate trust, unsupported applications, performance, and exception handling. A decryption policy that breaks critical applications will quickly be bypassed, so testing and staged rollout matter.
The evolution from basic packet filtering to application-aware inspection is part of the broader story described in modern firewall architecture. PCNSA-era knowledge remains relevant because administrators still need to know which layer is making a decision and why.
Security profiles should be attached according to policy intent. For example, a rule permitting outbound web access may need URL, malware, vulnerability, DNS, and file-analysis controls, while an internal management rule may require different inspection and logging. Reusing one universal profile everywhere can create unnecessary breakage or leave blind spots.
Traffic and threat logs show what the firewall actually observed. The principles of network-security logging matter because timestamps, source and destination fields, application identification, rule names, actions, threat details, and device context allow an administrator to test assumptions about policy behavior.
Logging should support a question. If an application fails, filter for the source, destination, and time window, then identify the matching rule and session outcome. If a threat profile blocks traffic, inspect the threat event and determine whether the detection is expected, false positive, or evidence of compromise. Opening a log viewer without a hypothesis usually produces noise.
Retention and centralized collection affect investigations. A locally stored event that rolls over quickly may disappear before an incident is noticed. Centralized logging can preserve evidence and correlate multiple firewalls, but only if devices are reporting correctly and timestamps are synchronized.
Panorama and newer centralized management approaches allow teams to manage objects, policy, templates, logs, and operational state across many devices. The advantage is consistency. The risk is blast radius: one shared object or template change can affect dozens or hundreds of firewalls.
Administrators need to understand inheritance, device groups, templates, scope, and the difference between configuration stored in the manager and configuration actually enforced on a firewall. A successful commit to a management system does not by itself prove that every target device received and applied the change.
Change control should include dependency review, staged rollout, validation, and rollback. Before editing a shared object, find where it is referenced. Before changing a template variable, identify which devices inherit it. Centralization rewards disciplined operators and punishes casual experimentation.
Commit discipline is part of administration. Review candidate configuration, understand warnings, use descriptive change records where available, and confirm that the final running configuration reflects the intended state. In shared environments, two administrators changing the same objects can create conflicts that are invisible if each person thinks only about the local edit.
Define the expected flow first: source, destination, application, port, ingress interface, ingress zone, route, NAT, security rule, inspection profile, egress interface, and return path. Then determine the first point where observed behavior differs from that expectation. This method narrows the problem before configuration changes are made.
Session information, counters, packet captures, route lookups, logs, and policy tests answer different questions. Use the least invasive source that can validate the next assumption. Capturing packets is powerful, but a session table or route lookup may solve the problem faster and with less operational overhead.
Remote-access problems also require protocol fundamentals. The concepts in VPN architecture and tunneling help distinguish authentication, tunnel establishment, routing, policy, and application issues. A tunnel being “up” does not prove user traffic is taking the right path.
DNS is another common dependency that can masquerade as a firewall problem. If an application connects by name, compare name resolution from the client with the destination actually seen in the session. Split DNS, stale records, proxy resolution, and service discovery can send traffic to an address that no longer matches the policy or NAT design.
An administrator who needs broad platform familiarity can start with the Network Security Professional exam. Someone responsible for objects, policies, centralized operations, posture improvement, and troubleshooting is closer to Network Security Analyst. Engineers who configure PAN-OS networking, device settings, integrations, automation, and firewall operations align more closely with NGFW Engineer.
Do not recreate a retired PCNSA study plan by memorizing old interface screenshots or exam percentages. Build a lab with two security zones, routing, NAT, application-aware rules, threat profiles, logging, and centralized changes. Break one dependency at a time and practice proving the cause with evidence.
PCNSA still describes a recognizable level of Palo Alto Networks administration, but it is now historical certification language. Treat it as a foundation of skills, not a scheduling target. The current role-based program offers a clearer way to demonstrate the specific operations, analysis, or engineering work you perform today.
Go to testing centre with ease on our mind when you use Palo Alto Networks PCNSA vce exam dumps, practice test questions and answers. Palo Alto Networks PCNSA Palo Alto Networks Certified Network Security Administrator certification practice test questions and answers, study guide, exam dumps and video training course in vce format to help you study with ease. Prepare with confidence and study using Palo Alto Networks PCNSA exam dumps & practice test questions and answers vce from ExamCollection.
Purchase Individually
Palo Alto Networks PCNSA Video Course
Top Palo Alto Networks Certifications


Top Palo Alto Networks Certification Exams
Site Search:

SPECIAL OFFER: GET 10% OFF

Pass your Exam with ExamCollection's PREMIUM files!
SPECIAL OFFER: GET 10% OFF
Use Discount Code:
MIN10OFF
A confirmation link was sent to your e-mail.
Please check your mailbox for a message from support@examcollection.com and follow the directions.

Download Free Demo of VCE Exam Simulator
Experience Avanset VCE Exam Simulator for yourself.
Simply submit your e-mail address below to get started with our interactive software demo of your free trial.
@Ben_J. their dumps for PCNSA exam are free! but of course to run these files you’ve got to also download the avanset exam simulator--- which is a paid one. but all in all, its worth the shot honestly! using their files is such a breeze and even very interactive...
Beyond happy and grateful to have tried ExamCollection! Their exam dumps for PCNSA were shockingly almost the same as at my actual exam! I tried both their free exam questions and premium bundle, and everything was just amazing! XOXO
@Ben_J. you won’t regret availing their free PCNSA braindumps mate! least 50 percent of the questions were part of my exam, which is definitely a great thing! and yes, just like what @keithkraken1980 said, you’d only be paying a small amount for the vce exam player.
Wud anyone confirm if their PCNSA vce files are really free of charge? I got some from other sites but was disappointed bec there wer hidden charges!! And are these really good? Wud definitely appreciate your replies. Thanks!
good supplementary resources for exam prep. but of course its advisable that you fully understand the concepts of the exam first before using their PCNSA exam dumps. also make sure you use other materials when studying so you’ll have a higher chance of acing your exam!
never had a hard time answering their practice questions.everything was just seamless from downloading their vce files for PCNSA exam to transporting it to the vce exam simulator! im praying that the questions will be more or less the same with the real exam..