



Premium File
458 Q&A
$76.99$69.99
Palo Alto Networks PCNSE Exam Questions & Answers, Accurate & Verified By IT Experts
Instant Download, Free Fast Updates, 99.6% Pass Rate
PCNSE Premium File: 458 Questions & Answers
Last Update: Oct 27, 2026
PCNSE Training Course: 142 Video Lectures
PCNSE PDF Study Guide: 658 Pages
$79.99
Palo Alto Networks PCNSE Exam Screenshots
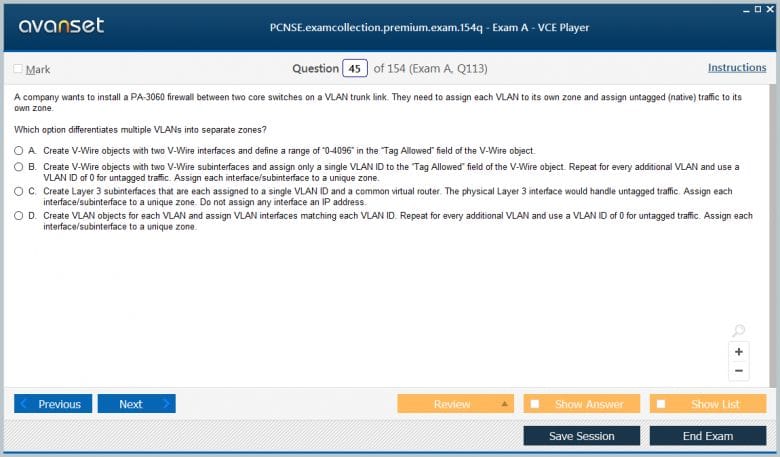
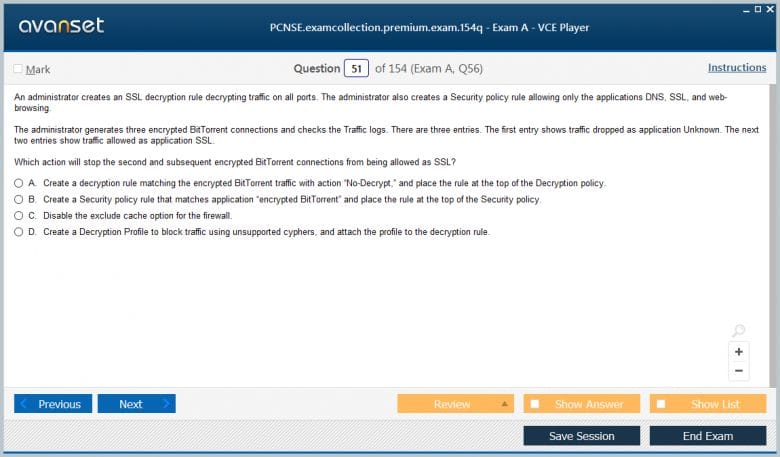
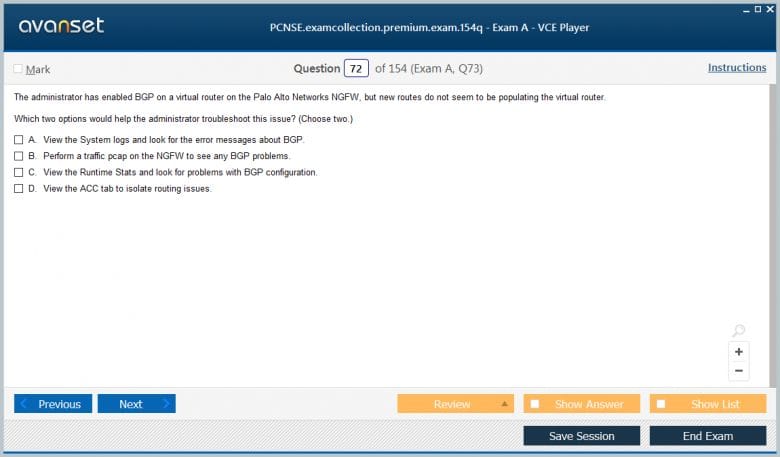
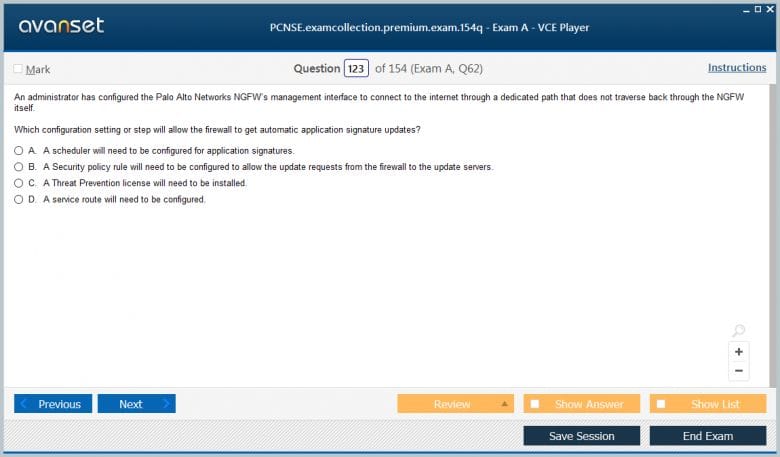
Palo Alto Networks PCNSE Practice Test Questions in VCE Format
Palo Alto Networks PCNSE Practice Test Questions, Exam Dumps
Palo Alto Networks PCNSE (Palo Alto Networks Certified Network Security Engineer) exam dumps vce, practice test questions, study guide & video training course to study and pass quickly and easily. Palo Alto Networks PCNSE Palo Alto Networks Certified Network Security Engineer exam dumps & practice test questions and answers. You need avanset vce exam simulator in order to study the Palo Alto Networks PCNSE certification exam dumps & Palo Alto Networks PCNSE practice test questions in vce format.
The PCNSE exam was one of Palo Alto Networks’ best-known legacy credentials. The Palo Alto Networks Certified Network Security Engineer exam retired on July 31, 2025 as the certification program shifted to job-role validation. Palo Alto Networks also stated that there is no direct one-for-one replacement because the old exam emphasized broad product knowledge while the new framework divides work by role.
The engineering skills behind PCNSE remain highly relevant. Current paths include Network Security Professional for broad platform operations, Network Security Analyst for policy and centralized operations, Next-Generation Firewall Engineer for deep PAN-OS deployment and administration, and Network Security Architect for senior design work. The right destination depends on what an engineer actually does.
An old PCNSE study guide can still serve as a technical checklist if it is treated cautiously. Routing, NAT, policy, App-ID, User-ID, threat prevention, decryption, VPNs, high availability, Panorama, logging, and troubleshooting are durable subjects. Product versions, interface paths, management options, and exam logistics are the parts that should be rebuilt from current sources.
Engineers need to know how a packet is classified, routed, translated, matched to policy, inspected, and recorded. That sequence is the backbone of troubleshooting. When a flow fails, the most useful question is not “which setting looks wrong?” but “at which processing stage did observed behavior first diverge from expectation?”
Build the flow with concrete values: source and destination addresses, application, protocol, ingress interface and zone, route and egress interface, NAT rule, security rule, user mapping, security profiles, and return path. Then use session data and logs to validate each assumption. This prevents random changes that create new problems while the original cause remains.
Engineers should also understand asymmetric and multi-path behavior. A session may enter one firewall and return through another path, or routing changes may cause the egress zone to differ from design assumptions. Stateful devices depend on seeing the traffic necessary to maintain session context.
Application identification can change during a session as more traffic becomes visible. Engineers should understand how that affects policy and logging, especially when an initial classification is generic and later becomes specific. Troubleshooting should compare the application seen at session start with the final classification rather than reading only one snapshot.
Static routing is simple until the environment grows. Dynamic routing introduces reachability exchange, preference, filtering, summarization, redistribution, and convergence behavior. Engineers should understand what route is selected and why, as well as what happens when a neighbor, circuit, tunnel, or next hop fails.
Policy-based forwarding can intentionally override the routing table for selected traffic, which makes troubleshooting more complex. A route lookup may appear correct while PBF sends the session elsewhere. Operational discipline requires checking all mechanisms that can influence forwarding rather than assuming the routing table is the whole decision.
Route redistribution deserves caution because mistakes can spread quickly. Use explicit filters, tagging, and route controls. A firewall participating in several routing domains should not become an accidental transit path or leak routes between environments that were meant to remain isolated.
Source NAT enables private systems to reach external networks, while destination NAT publishes internal services through alternate addresses or ports. Engineers should be able to reason about original and translated values at every point in the session and understand which values the security policy evaluates.
Large environments add complications such as NAT pools, address exhaustion, overlapping networks, twice NAT, load balancers, cloud gateways, and partner allowlists. Monitoring translated-session capacity and documenting external dependencies can prevent outages that appear unrelated to firewall policy.
During migration, NAT is often the hardest configuration to validate because translated addresses are embedded outside the firewall. DNS records, certificates, SaaS allowlists, partner configurations, and monitoring systems may all depend on a public address. Successful engineering therefore includes dependency discovery, not just correct syntax.
Destination NAT for published services introduces another layer: the security rule often needs to be reasoned about using the original destination while routing ultimately delivers to the translated host. Engineers should practice reading session output until the original and translated tuples are immediately clear.
App-ID lets policy describe applications rather than only ports, while User-ID connects activity to users and groups. These capabilities are powerful only when the underlying identification is reliable. Engineers need to understand application dependencies, SSL visibility, identity sources, and the effect of unknown or incomplete classification.
Security profiles add threat prevention to an allowed session. Anti-spyware, vulnerability protection, malware inspection, URL controls, DNS protections, and file analysis each observe different evidence. A profile that blocks traffic should be investigated at the layer responsible rather than “fixed” by removing inspection from the rule.
Policy should be reviewed over time. Applications change, owners change, user groups change, and temporary rules linger. Hit counts and logs help, but deletion decisions should consider seasonal or disaster-recovery traffic. Mature engineering treats policy as maintained software rather than a one-time installation.
Encrypted traffic can hide malware, command-and-control, data loss, and application details. TLS decryption restores visibility, but it also creates certificate, privacy, compliance, compatibility, and performance requirements. Engineers need a policy for what should be decrypted, what must be exempt, and how exceptions are reviewed.
Forward proxy and inbound inspection have different trust and key-management implications. Certificate chains must be trusted by endpoints, and applications using certificate pinning or unusual TLS behavior may fail. Rollouts should begin with representative users and applications, with clear metrics for breakage and security visibility.
Decryption troubleshooting should separate certificate problems from routing, policy, and application problems. Browser trust errors, handshake failures, unsupported cipher behavior, and application rejection can look like generic connectivity failures unless the engineer traces the TLS negotiation deliberately.
Certificate operations deserve their own runbook. Track certificate purpose, issuer, private-key location, expiration, trust distribution, and renewal ownership. Decryption outages are frequently certificate-lifecycle outages rather than firewall software defects, and they are preventable when ownership is explicit.
An HA pair is only one part of service resilience. Engineers need to understand control-link health, state synchronization, interface monitoring, path monitoring, failover triggers, and how upstream and downstream networks react. A successful firewall failover that leaves stale routes or neighbor state can still create an outage.
Split-brain and partial-failure scenarios deserve testing. A node may remain powered on while losing a critical path, management interface, or synchronization link. The design should define which failures trigger takeover and how the team distinguishes device failure from external network failure.
Maintenance procedures matter as much as emergency failover. Software upgrades, content updates, hardware replacement, and configuration changes should preserve state where possible and include validation. Teams that only test HA during real incidents learn too late that an assumption was wrong.
Upgrade testing should include HA behavior. Confirm compatibility, content prerequisites, session synchronization, routing convergence, and management connectivity before the maintenance window. Readiness also includes enough disk space and a recovery path if a node fails to return after reboot.
Centralized management introduces shared objects, device groups, templates, template variables, logging, and coordinated deployment. Engineers must understand inheritance and scope because the same configuration object can influence many firewalls. A small edit can have a large blast radius.
Operational state should be checked at the managed device, not only in the manager. A configuration may commit centrally but fail to push, partially apply, or produce device-specific errors. Deployment workflows should include per-device validation and a clear view of which version of configuration is actually enforced.
Logs are the evidence layer for that validation. The fundamentals in network-security logging help engineers correlate traffic, threats, configuration changes, and device state across a distributed environment.
Automation can improve consistency but should expose its intended delta before it pushes changes. Whether the tool is an API script, infrastructure pipeline, or management workflow, engineers should be able to preview scope, validate dependencies, detect drift, and roll back. Fast automation magnifies both good engineering and bad assumptions.
Engineers who primarily configure PAN-OS networking, device settings, integrations, objects, policies, and firewall operations are closest to NGFW Engineer. Those managing policy and posture centrally may align with Network Security Analyst. Broad network-security platform operators can use Network Security Professional, and design-focused senior engineers can progress toward Network Security Architect.
This is why Palo Alto Networks cautioned against asking for a single “replacement” for PCNSE. The retired credential bundled multiple responsibilities. The new portfolio makes the candidate decide whether the work is operations, analysis, engineering, or architecture.
A strong 2026 preparation plan should therefore start with the current Palo Alto Networks certifications, identify the target role, and build a lab around that role. Keep PCNSE’s disciplined packet-flow and troubleshooting habits, but measure progress through current tasks: design a path, deploy policy, automate repeatable changes, validate logs, simulate failure, and explain the evidence.
Engineers should also practice explaining a failure to someone who cannot see the CLI. A concise incident note should state the affected flow, the failed processing stage, the evidence, the change made, and the verification result. Clear communication is part of engineering because it lets operations, application owners, and security teams make coordinated decisions.
Keep a small library of known-good baselines: route tables, HA state, expected system resources, management connectivity, log-forwarding health, and representative session outputs. During an incident, comparison with a baseline can reveal the unusual condition faster than scanning every configuration page from scratch.
Go to testing centre with ease on our mind when you use Palo Alto Networks PCNSE vce exam dumps, practice test questions and answers. Palo Alto Networks PCNSE Palo Alto Networks Certified Network Security Engineer certification practice test questions and answers, study guide, exam dumps and video training course in vce format to help you study with ease. Prepare with confidence and study using Palo Alto Networks PCNSE exam dumps & practice test questions and answers vce from ExamCollection.
Purchase Individually
Palo Alto Networks PCNSE Video Course
Top Palo Alto Networks Certifications


Top Palo Alto Networks Certification Exams
Site Search:

SPECIAL OFFER: GET 10% OFF

Pass your Exam with ExamCollection's PREMIUM files!
SPECIAL OFFER: GET 10% OFF
Use Discount Code:
MIN10OFF
A confirmation link was sent to your e-mail.
Please check your mailbox for a message from support@examcollection.com and follow the directions.

Download Free Demo of VCE Exam Simulator
Experience Avanset VCE Exam Simulator for yourself.
Simply submit your e-mail address below to get started with our interactive software demo of your free trial.
is the premium dump still valid?
passed today with the premium. not 100%, but still very close.
Gave Exam last week and passed. premium is 90% updated
Is the premium dumps valid enough to pass the exam?
Is these dumps valid ? Answers are correct ?
Premium is valid. Not 100% but enough to pass.
The premium dump is %100 valid. Just use the questions
Is this dump still valid?
Is this exam question version 8 or 9?
Whether Premium Dump is valid ?
why no one is answering? any one can confirm this dump is valid or not please?
Thanks
Which is the latest dumps for pcnse 9 and valid till now?
Please someone share your comments which dump is valid. I'm going to write this month end
Is this exam question version 8 or 9?
Palo Alto Networks PCNSE Tests
Regards
Any body passed from this dumps
Guys,
is anyone tried that Premium dump as i'd like to buy it but im not sure it's 100% to pass or not can any one comfirm that
Is the PCNSE premium VCE valid?
is this exam for PAN OS 8 or PAN OS 9 ? Is this still valid ??
I am going to write exam this week Saturday (14th Sep 2019).Please confirm the dump is valid , I have purchased Aug 5th 2019
Premium dumps are 100% valid.passed on 10 August
Is the Dump still valid, i'm looking to pass the exam in auguste ?
Is this above dumps are valid?. I'm planning to take exam on this week. Pls update.
Is this valid?
Help me, what version is exam PCNSE?
I have passed PCNSE today with premium dumps its valid.
Is this dump still valid?
Has anyone auditioned in the past few days?
Premium is 100 % valid, but i checked answers. Just use the questions.
Exam valid. took test on june 3rd.
You may not pass with only free Dumps. Premium Dump is still valid, passed today.
Premium's are valid 100%. test taken on 28th May
Premium Dump is valid, Took exam today (12th May) and passed.
this is dump pcnse 8 or 8.1?
Please advise me this dump is correct or not?
PCNSE Premium
It's PCNSE 8 Version ???
@jefferson which dumps did you use?
Hi, I'm from Peru I bought the dump here and passed the exam with an average of 84%, there are some questions that are incorrect but more than 80% are good and that helped me to pass the exam. I just gave it on February 23 and all the questions of that dump came to me.
Is there anyone who passed PCNSE using premium dump ?
Free PCNSE once asnwers are wrong. How do we know actual dump is correct?
is the premium file still valid ?
Is there anyone who passed PCNSE using Exam Collection dumps
?
Is the PCNSE premium VCE valid?