



Premium File
60 Q&A
$76.99$69.99
Salesforce Certified Identity and Access Management Designer Exam Questions & Answers, Accurate & Verified By IT Experts
Instant Download, Free Fast Updates, 99.6% Pass Rate
60 Questions & Answers
Last Update: Sep 11, 2026
$69.99
Salesforce Certified Identity and Access Management Designer Exam Screenshots
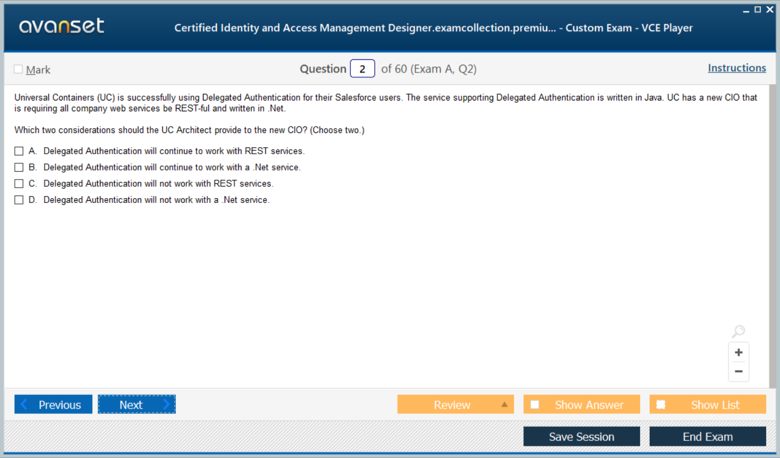
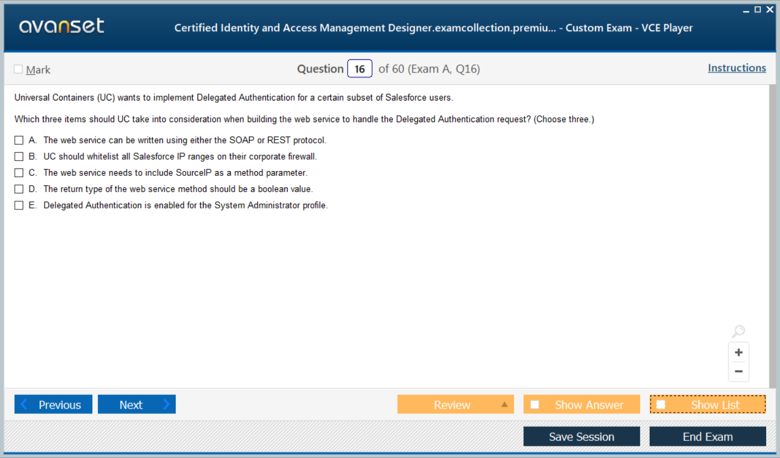
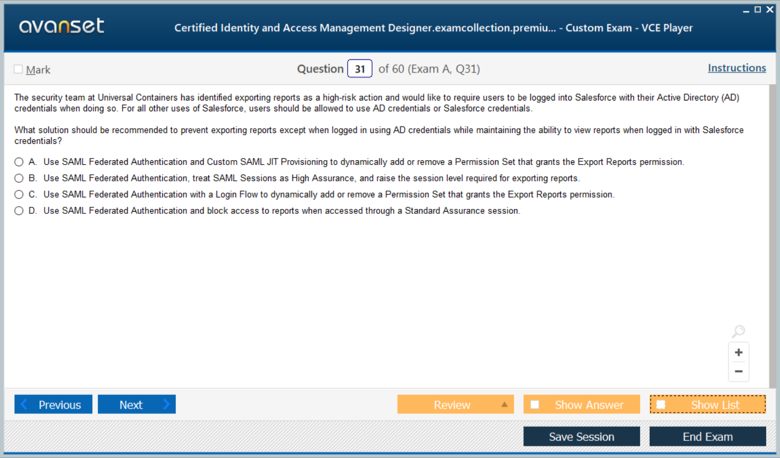
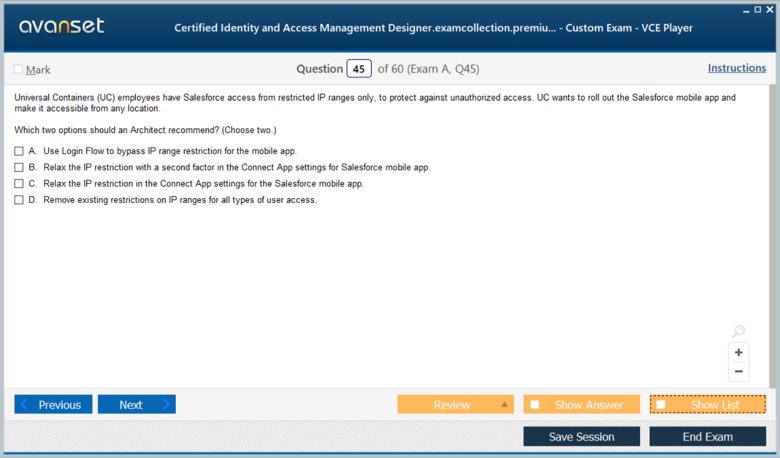
Salesforce Certified Identity and Access Management Designer Practice Test Questions in VCE Format
| File | Votes | Size | Date |
|---|---|---|---|
File Salesforce.test-king.Certified Identity and Access Management Designer.v2026-08-14.by.leah.37q.vce |
Votes 1 |
Size 63.58 KB |
Date Aug 14, 2026 |
File Salesforce.test-king.Certified Identity and Access Management Designer.v2020-03-17.by.william.30q.vce |
Votes 2 |
Size 49.51 KB |
Date Mar 17, 2020 |
Salesforce Certified Identity and Access Management Designer Practice Test Questions, Exam Dumps
Salesforce Certified Identity and Access Management Designer (Certified Identity and Access Management Designer) exam dumps vce, practice test questions, study guide & video training course to study and pass quickly and easily. Salesforce Certified Identity and Access Management Designer Certified Identity and Access Management Designer exam dumps & practice test questions and answers. You need avanset vce exam simulator in order to study the Salesforce Certified Identity and Access Management Designer certification exam dumps & Salesforce Certified Identity and Access Management Designer practice test questions in vce format.
The Salesforce Certified Identity and Access Management Designer exam is a legacy title from the earlier Salesforce architect program. In December 2021, Salesforce renamed this credential Identity and Access Management Architect as part of a broader effort to distinguish architecture certifications from the newer Designer role family. The current catalog goes one step further and presents the active credential as Salesforce Certified Platform Identity and Access Management Architect.
That naming sequence can confuse candidates who find an old exam guide and assume it refers to a discontinued specialty. It does not represent a separate modern track. The old Designer blueprint belongs to the same architectural lineage as today’s Salesforce Platform Identity and Access Management Architect certification, although current platform behavior and exam framing should always take priority over a historical document.
Within Salesforce certifications, the lasting value of this credential is its focus on trust boundaries. Candidates must understand how identities are established, federated, provisioned, authorized, monitored, and retired across Salesforce and connected systems. The title changed, but those questions remain central to enterprise architecture.
Older Identity and Access Management Designer resources often contain strong explanations of federation, SAML, OAuth, connected apps, social sign-on, external identity, and provisioning. Those concepts are still relevant because the underlying standards and architectural problems persist. What ages fastest is the exact user interface, product naming, default behavior, and list of supported configuration options.
A disciplined candidate should treat old material as a source of concepts and scenarios, then verify implementation details in current Salesforce documentation. If a tutorial tells you where to click but cannot explain the trust relationship being created, it is fragile knowledge. If it explains who signs an assertion, who validates it, which identifier is mapped, and where authorization happens, the lesson can survive several product releases.
The historical title did not describe visual or experience design. Identity architects evaluate competing patterns and make recommendations based on security, scale, usability, lifecycle, and organizational ownership. They decide whether Salesforce should trust an external identity provider, act as an identity provider itself, use delegated authorization for an integration, or create external identities through a branded registration flow.
Those decisions require trade-offs. Centralized workforce identity can improve consistency but creates a critical dependency on the enterprise identity provider. Self-registration can reduce support work but increases the need for duplicate detection and verification. Long-lived integrations can be reliable but become risky when credentials are not rotated. Architecture is about understanding those consequences before implementation.
An enterprise rarely has one kind of user. Employees, contractors, partners, customers, service accounts, administrators, and integration processes may all access Salesforce differently. The architect should classify those populations and define the assurance each one needs. Administrative users may require stronger controls than a low-risk public community user, while a machine integration needs a noninteractive flow entirely.
This prevents the organization from forcing one authentication pattern onto every use case. Password-based login, federated SSO, social identity, certificate-based access, and OAuth flows solve different problems. The architecture should state why a pattern is appropriate, what dependency it creates, and how the user recovers when the normal path fails.
In a SAML flow, the identity provider authenticates the user and the service provider relies on a signed assertion. That sounds simple until organizations introduce multiple domains, several identity providers, certificate rotation, inconsistent identifiers, or users who belong to more than one business unit. Legacy exam scenarios were valuable because they forced candidates to reason through those complications instead of memorizing a setup wizard.
A good design specifies the identifier used to locate the Salesforce user, the attributes carried in the assertion, the certificate lifecycle, and the failure path. It also defines how a new user is created when just-in-time provisioning is allowed and which attributes the identity provider is permitted to control. Trust should be explicit rather than inferred from a successful login.
OAuth is commonly introduced as an API authorization standard, but Salesforce supports several flows for different client types. An interactive browser application, a trusted server, a mobile client, and an unattended integration do not have the same credential-storage or user-interaction characteristics. The architect needs to choose a flow that fits the client instead of selecting whichever example is easiest to copy.
Scopes, token expiration, refresh behavior, revocation, and secret or certificate storage are part of the architecture. A token with broad access and no clear owner can outlive the project that created it. Legacy study material should therefore be modernized by asking a lifecycle question for every credential: who issues it, where is it stored, how is it rotated, and how is access removed?
Creating accounts is only half of identity lifecycle management. Organizations need a reliable source for employment or relationship status and a process that disables access when that status changes. Manual user creation can work at small scale but becomes error-prone when thousands of employees, partners, or customers are involved.
Just-in-time provisioning can reduce administrative work, but it moves important decisions into federation. Directory-driven provisioning can make workforce lifecycle more consistent, but only if the source attributes are accurate. The architect should also consider dormant accounts, transfers, role changes, and users who return after a period away. Identity lifecycle is continuous rather than a one-time onboarding step.
When customers or partners access Salesforce through digital experiences, identity cannot be separated from the external-user data model. The Salesforce Experience Cloud Consultant domain illustrates this overlap: a user’s contact, account, license, and sharing relationship influence what happens after authentication succeeds.
Legacy Community-era examples may use older terminology, but the architectural problem is still current. Decide how users register, how duplicate people are detected, how an existing identity is linked, and what happens when a partner changes organizations. A clean login flow can still create a security problem if the resulting user is associated with the wrong account or sharing context.
Identity providers often send attributes such as department, role, location, or group membership. Those attributes can help automate Salesforce access, but they also create a dependency. If an upstream group assignment grants a powerful permission set, the directory process has effectively become part of Salesforce authorization governance.
Architects should define which attributes can influence access and who owns their accuracy. High-risk entitlements may deserve additional approval inside Salesforce rather than being accepted automatically. The Salesforce Platform Sharing and Visibility Architect discipline becomes relevant when identity-derived permissions interact with complex record access.
Federation and integration designs often depend on certificates, keys, client secrets, or other credentials that eventually expire or require rotation. An architecture is not complete if the implementation team knows how to configure them once but the operations team has no inventory, owner, or renewal process.
Candidates should think about monitoring and handoff. Which certificates are approaching expiration? Who owns the connected app? How is a secret rotated without downtime? How does the team test the new trust material before the old one is removed? Many real identity outages occur because routine lifecycle work was not treated as part of architecture.
Identity systems generate useful evidence: login events, federation errors, authorization failures, connected-app activity, administrative changes, and identity-provider logs. The architect should decide what needs to be retained and how events from different systems can be correlated. Without that evidence, teams may be unable to distinguish an attack from a simple configuration error.
Troubleshooting also benefits from a layered approach. Start with the user’s intended path, then identify each trust boundary and decision point. Determine whether the failure is authentication, user lookup, provisioning, session creation, or authorization. This method is more reliable than changing several settings at once until the login happens to work.
The old Designer exam emerged when enterprise SSO was often the dominant identity project. Modern architectures also need to account for APIs, external communities, mobile clients, automation, service identities, stronger MFA expectations, conditional access, and more distributed cloud estates. The credential’s evolution into a Platform architect title reflects that broader environment.
Even so, the core mental model has not changed: identify actors, define trust, minimize privilege, manage lifecycle, preserve evidence, and design recovery. The Salesforce Identity and Access Management Architect naming that followed the 2021 rename is a useful bridge between historical Designer resources and the current Platform title.
One useful way to translate the old Designer blueprint is to redraw each scenario as a trust map. Mark the authoritative identity source, relying applications, federation protocols, provisioning path, token or certificate boundaries, and the point at which Salesforce permissions take over. That exercise exposes assumptions that are easy to miss in feature-oriented study material. It also makes the legacy credential relevant to the current architect role because the durable skill is explaining who trusts whom, for what purpose, with which evidence, and how that trust is withdrawn.
A productive way to use legacy material is to take an old architecture scenario and redesign it with current Salesforce capabilities. Keep the business problem constant but re-evaluate the protocol choice, user model, MFA, provisioning, connected-app policy, certificate handling, and external-user experience. This reveals which principles were durable and which implementation assumptions have aged.
Then create failure cases: a certificate expires, an employee transfers departments, a partner user changes companies, a token is compromised, a social identity duplicates an existing contact, or an integration continues running after its owner leaves. If the design explains prevention, detection, and recovery across those events, the candidate has extracted the real value of the old Identity and Access Management Designer credential rather than merely preserving its terminology.
Go to testing centre with ease on our mind when you use Salesforce Certified Identity and Access Management Designer vce exam dumps, practice test questions and answers. Salesforce Certified Identity and Access Management Designer Certified Identity and Access Management Designer certification practice test questions and answers, study guide, exam dumps and video training course in vce format to help you study with ease. Prepare with confidence and study using Salesforce Certified Identity and Access Management Designer exam dumps & practice test questions and answers vce from ExamCollection.
Purchase Individually
Top Salesforce Certifications


Top Salesforce Certification Exams
Site Search:

SPECIAL OFFER: GET 10% OFF

Pass your Exam with ExamCollection's PREMIUM files!
SPECIAL OFFER: GET 10% OFF
Use Discount Code:
MIN10OFF
A confirmation link was sent to your e-mail.
Please check your mailbox for a message from support@examcollection.com and follow the directions.

Download Free Demo of VCE Exam Simulator
Experience Avanset VCE Exam Simulator for yourself.
Simply submit your e-mail address below to get started with our interactive software demo of your free trial.