



Premium File
1097 Q&A
$76.99$69.99
Isaca CISA Exam Questions & Answers, Accurate & Verified By IT Experts
Instant Download, Free Fast Updates, 99.6% Pass Rate
CISA Premium File: 1097 Questions & Answers
Last Update: Sep 06, 2026
CISA Training Course: 74 Video Lectures
CISA PDF Study Guide: 1141 Pages
$79.99
Isaca CISA Exam Screenshots
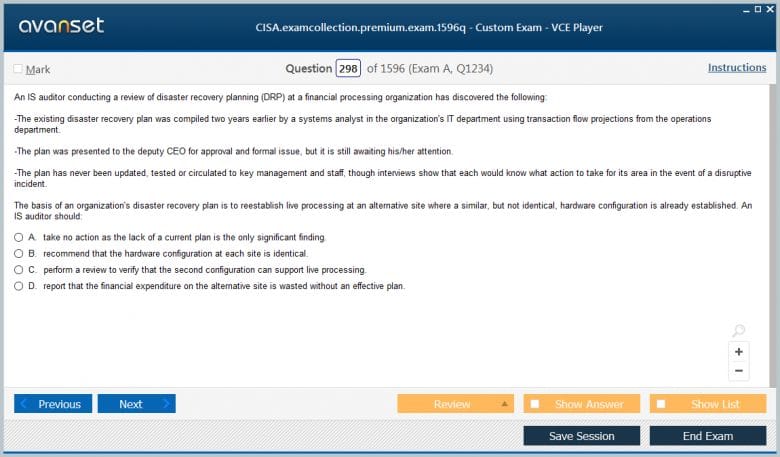
Isaca CISA Practice Test Questions in VCE Format
| File | Votes | Size | Date |
|---|---|---|---|
File Isaca.braindumps.CISA.v2026-08-21.by.miles.2079q.vce |
Votes 1 |
Size 8.74 MB |
Date Aug 21, 2026 |
File Isaca.examanswers.CISA.v2021-10-28.by.liuwei.2026q.vce |
Votes 1 |
Size 9.23 MB |
Date Oct 28, 2021 |
File Isaca.selftestengine.CISA.v2021-09-09.by.stanley.1975q.vce |
Votes 1 |
Size 7.2 MB |
Date Sep 09, 2021 |
File Isaca.selftesttraining.CISA.v2021-07-08.by.lixia.1957q.vce |
Votes 1 |
Size 8.1 MB |
Date Jul 08, 2021 |
File Isaca.selftesttraining.CISA.v2021-04-06.by.james.1910q.vce |
Votes 1 |
Size 8.41 MB |
Date Apr 06, 2021 |
File Isaca.test-king.CISA.v2020-10-08.by.mason.1457q.vce |
Votes 2 |
Size 7.03 MB |
Date Oct 08, 2020 |
File Isaca.pass4sureexam.CISA.v2020-03-23.by.mohammed.1103q.vce |
Votes 3 |
Size 6.34 MB |
Date Mar 25, 2020 |
File Isaca.Braindumps.CISA.v2015-03-30.by.Beaulah.1178q.vce |
Votes 6 |
Size 2.39 MB |
Date Mar 30, 2015 |
File Isaca.Visualexams.CISA.v2014-12-10.by.Moorish.595q.vce |
Votes 15 |
Size 1013.02 KB |
Date Dec 10, 2014 |
Archived VCE files
| File | Votes | Size | Date |
|---|---|---|---|
File ISACA.Certkey.CISA.v2011-06-10.by.Davidson.625q.vce |
Votes 2 |
Size 816.22 KB |
Date Jun 13, 2011 |
File ISACA.Braindump.CISA.v2010-06-17.by.Bams.100q.vce |
Votes 2 |
Size 175.19 KB |
Date Jun 20, 2010 |
File ISACA.Braindump.CISA.v2010-06-17.by.Bams.600q.vce |
Votes 1 |
Size 972.51 KB |
Date Jun 20, 2010 |
File ISACA.ExamMatrix.CISA.v2010-05-01.by.Shravan.133q.vce |
Votes 1 |
Size 115.26 KB |
Date May 02, 2010 |
File ISACA.SelfTestEngine.CISA.v2010-02-25.by.Taylor.44q.vce |
Votes 1 |
Size 44.43 KB |
Date Feb 24, 2010 |
Isaca CISA Practice Test Questions, Exam Dumps
Isaca CISA (Certified Information Systems Auditor) exam dumps vce, practice test questions, study guide & video training course to study and pass quickly and easily. Isaca CISA Certified Information Systems Auditor exam dumps & practice test questions and answers. You need avanset vce exam simulator in order to study the Isaca CISA certification exam dumps & Isaca CISA practice test questions in vce format.
Certified Information Systems Auditor (CISA) remains ISACA’s flagship audit certification and currently uses a 150-question exam across five domains. The active outline weights Information Systems Auditing Process at 18%, Governance and Management of IT at 18%, Information Systems Acquisition, Development and Implementation at 12%, Information Systems Operations and Business Resilience at 26%, and Protection of Information Assets at 26%. The current structure reflects the 2024 job-practice update and remains the live blueprint in 2026.
CISA is an experience-based certification. ISACA currently requires five or more years of professional information-systems auditing, control, or security experience for certification, although candidates may sit the exam before they have completed the experience requirement and must apply within five years after passing. That separation matters: the exam tests professional judgment across audit and technology, while the certification process validates that the candidate has also worked in the field.
An audit plan should begin with objectives, risk, scope, and criteria rather than with a checklist of controls. Auditors need to understand the business process, technology environment, regulatory obligations, prior findings, changes, dependencies, and management concerns before deciding what to test. Risk-based planning directs limited assurance resources toward areas where failure could materially affect objectives, data, compliance, customers, or operations.
The auditor also needs independence and professional skepticism. Management may provide useful explanations and evidence, but the auditor must determine whether that evidence is sufficient, reliable, relevant, and obtained from an appropriate source. The approved CISA preparation material can support review strategy, while the exam itself rewards the ability to distinguish evidence from assertion.
Professional standards and ethics shape how that work is performed. Auditors need to protect confidentiality, avoid conflicts of interest, maintain competence, document judgments, and communicate limitations rather than overstating assurance. Independence is organizational as well as personal: reporting lines, budget authority, restrictions on scope, and prior operational responsibilities can all affect whether an auditor can evaluate an area objectively. Exam scenarios often become clearer when the candidate asks whether the proposed action would compromise independence or bypass appropriate governance.
Policies, screenshots, logs, tickets, configurations, contracts, reports, interviews, data extracts, observation, and re-performance can all support an audit conclusion. Their strength depends on source, completeness, timing, objectivity, and whether they directly address the control or risk being tested. A screenshot supplied by the control owner may be weaker than a system-generated population obtained independently; an interview can explain process but rarely proves consistent operation on its own.
Sampling and data analytics help auditors examine large populations, but they introduce their own assumptions. The auditor must know whether the population is complete, how the sample was selected, whether exceptions are representative, and whether transformations changed the data. Automated analysis can increase coverage while still producing false assurance if input data is incomplete or the test logic does not match the audit objective.
AI and automated analytics can expand audit coverage, but they also create new evidence questions. An auditor using a model to classify transactions or prioritize anomalies should understand the data population, transformation steps, model limitations, human review process, and possibility of systematic false negatives. Automation can help identify unusual patterns and test entire populations; it does not transfer professional responsibility to the tool. The auditor still needs to decide whether the method is appropriate for the objective and whether the results are sufficiently reliable to support a conclusion.
CISA candidates need to understand organizational structure, strategy, architecture, risk, policies, standards, privacy, data governance, vendor management, performance, and quality. The auditor does not design the enterprise’s governance system, but must evaluate whether responsibilities, oversight, and information support sound decisions. A control can operate exactly as documented yet still be inadequate if the policy or governance objective is weak.
The relationship to CGEIT is useful: CGEIT approaches governance from the perspective of those directing and overseeing enterprise technology, while CISA asks how an auditor would obtain evidence that governance and management mechanisms are appropriately designed and operating. COBIT 2019 provides one recognized framework for structuring those governance and management objectives.
Auditors need enough knowledge of project governance, development methods, requirements, testing, configuration, release, migration, data conversion, and post-implementation review to evaluate whether new systems are introduced in a controlled manner. Agile and DevOps change the cadence of delivery, but they do not remove the need for authorization, traceability, segregation where appropriate, testing, secure configuration, and evidence of deployment.
Common audit questions include whether requirements are approved, whether developers can change production directly, whether emergency changes are reviewed, whether test data exposes sensitive information, whether migration reconciles completely, and whether failed releases can be recovered. The auditor should evaluate the control objective and risk rather than insist on one development methodology.
The largest current CISA domains include operations and business resilience. Auditors may evaluate asset management, capacity, scheduling, interfaces, databases, configuration, patching, incident and problem management, service levels, logging, backups, continuity, and disaster recovery. The central question is whether critical information systems can operate reliably and recover within business requirements—not whether every operational procedure looks identical across teams.
Business impact analysis should connect processes to recovery priorities and dependencies. Recovery objectives need to be achievable through architecture, backups, alternate facilities, suppliers, communications, and tested procedures. The approved business continuity and disaster recovery discussion can deepen the technical context, while CISA emphasizes the evidence needed to conclude whether plans are complete, current, and tested.
Resilience evidence should include more than the existence of a plan. Auditors can examine whether recovery assumptions match current infrastructure, whether backups are isolated and restore-tested, whether recovery teams know their roles, whether suppliers participate where necessary, and whether exercises expose unresolved dependencies. A successful tabletop discussion is useful but does not prove that data can be restored within the required time. Conversely, a technically successful recovery test may still be weak if business owners were not involved in validating priorities and acceptable data loss.
CISA auditors need working security knowledge because controls cannot be assessed in abstraction. Identity and access management, privileged access, network segmentation, endpoint protection, encryption, key management, physical security, cloud configuration, mobile devices, monitoring, awareness, testing, incident response, and forensics can all appear in the current outline. The auditor’s role is to determine whether controls reduce risk and whether evidence supports that conclusion.
A technical finding needs business context. An unpatched system may be critical because it is internet-facing and handles sensitive data, or less urgent because it is isolated and scheduled for retirement. Likewise, a strong authentication control can still fail if joiner/mover/leaver processes leave stale access. CISA questions often reward the answer that first establishes risk, scope, evidence, or root cause rather than the answer that immediately deploys a technical fix.
Organizations increasingly rely on SaaS, public cloud, managed services, APIs, and external data processors. Auditors need to understand shared responsibility, service organizations, contracts, assurance reports, complementary customer controls, data location, exit provisions, and concentration risk. The CCAK certificate goes deeper into cloud-specific assurance, while CISA keeps cloud within the broader audit universe.
Privacy creates another cross-cutting audit area. Personal information may be collected, replicated, analyzed, retained, transferred, and deleted across many systems. Auditors should test governance, data inventories, access, consent or lawful use, retention, subject-right processes, vendor controls, and incident response where applicable. CDPSE is more implementation-focused; CISA remains concerned with whether the organization can demonstrate effective control.
Third-party assurance requires more than collecting a SOC report or certification. Auditors should confirm that the report period, services, locations, control objectives, and subservice organizations match the organization’s actual use. Exceptions need to be evaluated for relevance, and complementary user-entity controls must be mapped to internal owners. Contractual audit rights, incident notification, resilience obligations, data handling, and exit provisions can close gaps that a standardized assurance report does not address.
A candidate should repeatedly ask: what is the objective, what is the risk, what evidence would be sufficient, who is accountable, and what should the auditor do first? That mindset helps with questions where several answers are plausible. CISA is not simply a security test, project-management test, or controls glossary. It examines how an independent assurance professional evaluates technology in business context.
CISA exam preparation and other ISACA certifications provide useful context for candidates planning their next steps. Candidates should still use the live ISACA outline as the authoritative boundary for preparation because domain content can be updated. As of October 2026, the 150-question five-domain structure described above remains current.
Reporting is part of the audit process rather than an administrative ending. A useful finding connects a condition to agreed criteria, explains cause where evidence supports it, describes the resulting risk or impact, and presents a recommendation or agreed action that addresses the underlying issue. Root cause matters because repeatedly correcting individual exceptions can leave the process weakness intact. Follow-up should verify that management actions were implemented and that residual risk is understood rather than assuming closure because a due date passed.
Go to testing centre with ease on our mind when you use Isaca CISA vce exam dumps, practice test questions and answers. Isaca CISA Certified Information Systems Auditor certification practice test questions and answers, study guide, exam dumps and video training course in vce format to help you study with ease. Prepare with confidence and study using Isaca CISA exam dumps & practice test questions and answers vce from ExamCollection.
Purchase Individually
Isaca CISA Video Course
Top Isaca Certifications


Top Isaca Certification Exams
Site Search:

SPECIAL OFFER: GET 10% OFF

Pass your Exam with ExamCollection's PREMIUM files!
SPECIAL OFFER: GET 10% OFF
Use Discount Code:
MIN10OFF
A confirmation link was sent to your e-mail.
Please check your mailbox for a message from support@examcollection.com and follow the directions.

Download Free Demo of VCE Exam Simulator
Experience Avanset VCE Exam Simulator for yourself.
Simply submit your e-mail address below to get started with our interactive software demo of your free trial.
Is the premium is valid dump?
Premium is valid
Are cisa premium file is still valid??
@emerson, well…using them is not a must, but! If you want to see the exam structure and what is gonna be tested, they are highly recommended to be used…… I just passed my exam with the help of these CISA exam dumps and should say they are what will make you pass this assessment….. all the best!
hi guys….is it a must to prepare with these dumps for CISA exam??? will I fail if I don’t use them?
@Toby67, i passed this test some days ago and can say that questions and answers for CISA exam are valid and updated. they reflect the actual contents well and that is why practicing with them helped me pass… study these files with an open mind as you seek to understand the concepts then you will definitely ace this assessment. wish you luck!
Hi! can some recent exam takers please comment on the validity of these CISA practice questions and answers. did they help you pass this exam?
@sean_paul, yes they are. these isaca cisa practice tests really saved me when I took this exam. thanks to them, i knew how to answer the exam questions because almost all of them were familiar for me. these files are some of the best materials i used during my preparation… so i recommend them 100%!
are these vce files for CISA exam up to date?
Can anyone confirm that the premiums dumps are valid please?
Are CISA premium dump valid?
Are these dumps valid? Can anyone please tell us?
Is this valid ? did anyone pass recently