
Pass Your Isaca CISA Certification Easy!
Isaca CISA Certification Exams Questions & Answers, Accurate & Verified By IT Experts
Instant Download, Free Fast Updates, 99.6% Pass Rate.
$69.99
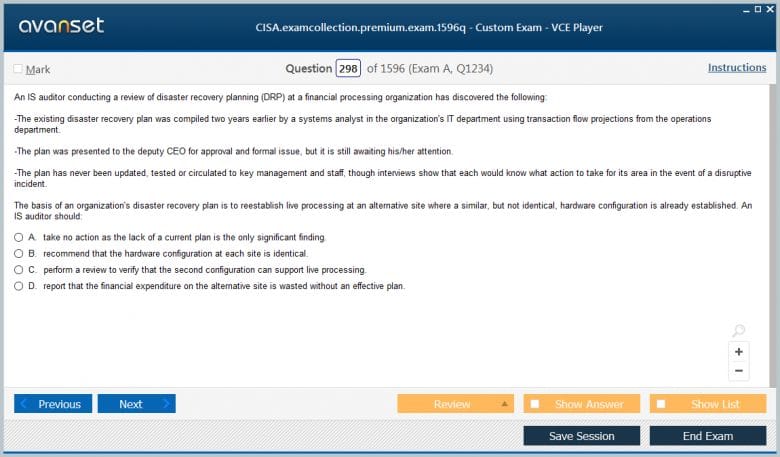
Isaca CISA Certification Exams Screenshots
CISA Product Reviews
Download Free CISA Practice Test Questions VCE Files
| Exam | Title | Files |
|---|---|---|
Exam CISA |
Title Certified Information Systems Auditor |
Files 29 |
Isaca CISA Certification Exam Dumps & Practice Test Questions
Prepare with top-notch Isaca CISA certification practice test questions and answers, vce exam dumps, study guide, video training course from ExamCollection. All Isaca CISA certification exam dumps & practice test questions and answers are uploaded by users who have passed the exam themselves and formatted them into vce file format.
CISA: Turning Technology Risk into Audit Evidence
The Certified Information Systems Auditor credential is designed for professionals who need to evaluate whether technology supports business objectives, protects information, operates reliably, and is governed with appropriate accountability. The current CISA exam contains 150 questions across five job-practice domains, but the real challenge is not the number of topics. It is learning to approach technical situations as an auditor: identify the objective, understand the risk, determine the expected control, evaluate evidence, and communicate the significance of what was found.
CISA is one of the anchor credentials in the ISACA certifications. It also serves as a foundation for newer specialist paths such as Advanced in AI Audit, where active CISA holders already satisfy the core audit-credential prerequisite. That progression reflects CISA's enduring role: it establishes the information-systems assurance discipline that can then be extended into emerging technologies.
The exam begins with the audit process, not with technology trivia
Domain 1 covers the information systems auditing process. Candidates should understand planning, standards, risk-based scoping, evidence, sampling, analytics, reporting, follow-up, and professional judgment. The exam often presents several technically plausible actions and asks which is most appropriate from an audit perspective. The best answer is usually the one that preserves independence, addresses the highest relevant risk, and produces sufficient and reliable evidence.
Audit sequencing matters. An auditor normally understands objectives and risks before selecting procedures. Testing a control without knowing what risk it is supposed to address can produce activity without assurance. Likewise, a finding is not simply a control failure; it should explain condition, criteria, cause, consequence, and management response in a way that supports decision-making.
CISA exam preparation is most useful when it reinforces the reasoning behind audit choices rather than reducing the credential to exam mechanics. Candidates should repeatedly connect objectives, risks, controls, evidence, findings, and follow-up until that sequence becomes natural.
Governance and management of IT connect business and technology
The second domain asks whether IT is directed and controlled in a way that supports enterprise goals. Candidates need to understand governance structures, policies, roles, performance management, resource allocation, enterprise architecture, vendor management, risk management, data governance, and continuity planning.
This is where CISA differs from a purely technical security certification. A system can be well configured and still be poorly governed. An organization may have strong firewalls but weak ownership of critical applications, uncontrolled technology procurement, unclear accountability for third parties, or an architecture that no longer supports strategic priorities. The auditor must be able to identify these structural weaknesses.
Systems acquisition and development require control before go-live
Domain 3 covers acquisition, development, implementation, and change. Candidates should understand project governance, requirements, feasibility, development methodologies, testing, migration, conversion, release, and post-implementation review. The central audit question is whether controls are built into the lifecycle rather than bolted on after deployment.
Requirements are especially important. If business, security, privacy, resilience, and regulatory needs are not defined early, later testing may verify that the system works while missing whether it works safely and compliantly. Auditors should also understand segregation of duties within development and deployment, source control, change approval, environment separation, test evidence, and rollback planning.
Agile and DevOps do not eliminate governance. They change the cadence and automation through which controls operate. A mature audit approach examines pipelines, approvals, automated testing, access controls, logging, and exception management rather than demanding a waterfall process simply because it is easier to document.
Operations and resilience are about sustained reliability
Domain 4 moves into day-to-day technology operations: job scheduling, incident and problem management, change, capacity, backup, disaster recovery, service levels, infrastructure, databases, cloud services, and operational monitoring. Candidates should think about whether the environment can deliver required services consistently and recover when disruption occurs.
Business continuity and disaster recovery questions often test priorities. Recovery objectives should come from business impact analysis rather than from what technology teams find convenient. Recovery time objectives, recovery point objectives, dependencies, alternate processing, backup integrity, and testing all need to align with business needs.
Operational evidence also matters. A policy that says backups occur is weaker than logs showing successful backups, restoration tests, exception handling, and periodic validation. Auditors should continually ask what proves a control is operating, not merely whether documentation says it exists.
Protection of information assets is broader than cybersecurity tooling
The fifth domain covers security, privacy, identity, network protection, cryptography, physical security, vulnerability management, monitoring, incident response, and data protection. The domain is broad because information assets can be compromised through people, process, technology, or third parties.
Access control is a good example. The auditor should understand authentication, authorization, privileged access, account lifecycle, segregation of duties, and monitoring. Yet the most important question may be governance: who approves access, how entitlements are reviewed, whether terminated users are removed promptly, and whether exceptions are tracked. Technical configuration and business ownership have to work together.
CISA, CISM, and CRISC are related but not interchangeable
Candidates often compare CISA with CISM and CRISC. CISA looks at systems through the lens of audit and assurance. CISM focuses on managing an enterprise information security program. CRISC focuses on identifying, assessing, responding to, and monitoring enterprise IT risk. The same organization may need all three perspectives.
The difference becomes clear in a control scenario. A CISM-oriented professional may design and operate the security program. A CRISC-oriented professional may frame the risk, treatment, metrics, and reporting. A CISA-oriented professional independently evaluates whether governance and controls are adequate and effective. The knowledge overlaps, but the professional responsibility changes.
CISA also connects naturally to broader internal audit
Information systems audits rarely exist in isolation. A revenue process may depend on ERP configuration, interfaces, identity controls, database integrity, third-party services, and manual approvals. Professionals with the Certified Internal Auditor credential bring a wider internal-audit perspective, while CISA adds depth in technology and information systems assurance.
The relationship is formally recognized by The IIA's CIA Challenge pathway for qualified active CISA holders. That does not make the credentials equivalent, but it demonstrates how strongly information-systems audit is connected to the broader assurance profession.
Study by tracing risk through complete scenarios
A weak preparation method is to memorize hundreds of isolated facts. A stronger method is to study end-to-end scenarios. Take a cloud migration, ERP implementation, outsourced payroll service, payment platform, or identity modernization program. Ask how governance should work, what risks matter, which controls should exist, how implementation should be tested, what operational evidence should be available, and how security and resilience should be assessed.
Then change the facts. What if the vendor is critical? What if the system processes regulated data? What if development is agile? What if recovery objectives are aggressive? What if administrators have excessive access? CISA questions frequently reward the candidate who can identify which fact changes the audit priority.
When two answers both appear reasonable, consider sequence and responsibility. Auditors normally gather sufficient evidence before concluding. Management owns risk and controls; auditors assess them. High-risk issues generally take priority over low-impact procedural imperfections. Root cause is more useful than symptoms. Preventing a problem is often stronger than detecting it later, but detective controls may still be appropriate when prevention is impractical.
The goal is not to guess what ISACA “likes.” It is to internalize a coherent audit approach. Once candidates consistently distinguish management responsibility from audit responsibility, connect tests to risk, and prefer evidence-based conclusions, many difficult questions become easier to reason through.
Cloud platforms, AI systems, APIs, third-party software, automated workflows, and data-driven products have reduced the boundary between “IT risk” and ordinary business risk. Auditors increasingly need to understand both. CISA remains valuable because it trains professionals to examine that intersection without becoming trapped in product-specific details.
The strongest candidate is therefore not the person who memorizes the most acronyms. It is the person who can look at a complicated technology environment and ask disciplined questions about governance, risk, controls, evidence, resilience, and accountability. That mindset is what turns technical knowledge into assurance.
Third parties and cloud services change the evidence model
Modern CISA work often involves services the audited organization does not operate directly. Cloud platforms, SaaS applications, payment processors, managed service providers, and outsourced development teams can all perform critical controls. The auditor therefore needs to understand contracts, service commitments, assurance reports, responsibilities, subcontractors, incident obligations, access to evidence, and the organization's own monitoring of the provider.
A common mistake is to treat a vendor assurance report as the end of the audit. Third-party reports have scope, period, control, and user-entity assumptions that must be evaluated. The organization may still be responsible for complementary controls such as identity administration, configuration, data classification, or incident escalation. Vendor risk also changes over time as services, subprocessors, and business dependence evolve.
CISA exam strategy is useful when building exam fluency, but candidates should practice reading assurance evidence critically. The correct question is not whether documentation exists; it is whether the available evidence actually supports the audit objective.
Audit analytics should strengthen evidence, not replace skepticism. Data analytics can expand audit coverage by identifying unusual transactions, duplicate payments, access anomalies, timing patterns, or populations that do not conform to expected rules. Yet a large dataset is not automatically reliable evidence. The auditor should understand data origin, completeness, transformation, extraction logic, field definitions, and whether the population represents the process being audited.
Analytics is most valuable when it changes the quality of inquiry. A pattern may identify where to test further, help select a targeted sample, or reveal an exception population that deserves root-cause analysis. The auditor still needs to validate significance and avoid confusing correlation with control failure.
ExamCollection provides the complete prep materials in vce files format which include Isaca CISA certification exam dumps, practice test questions and answers, video training course and study guide which help the exam candidates to pass the exams quickly. Fast updates to Isaca CISA certification exam dumps, practice test questions and accurate answers vce verified by industry experts are taken from the latest pool of questions.


Isaca CISA Video Courses
Top Isaca Certifications


Top Isaca Certification Exams
Site Search:



