Premium File
642 Q&A
$76.99$69.99
IIA IIA-CIA-Part3 Exam Questions & Answers, Accurate & Verified By IT Experts
Instant Download, Free Fast Updates, 99.6% Pass Rate
IIA-CIA-Part3 Premium File: 642 Questions & Answers
Last Update: Sep 24, 2026
IIA-CIA-Part3 Training Course: 170 Video Lectures
$74.99
IIA IIA-CIA-Part3 Exam Screenshots
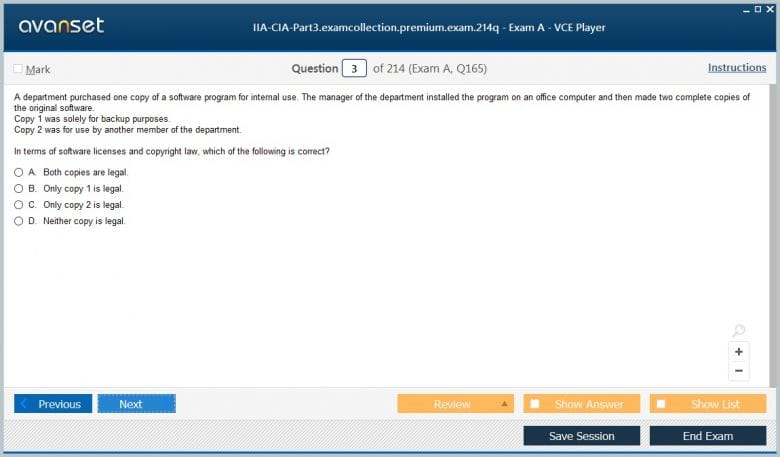
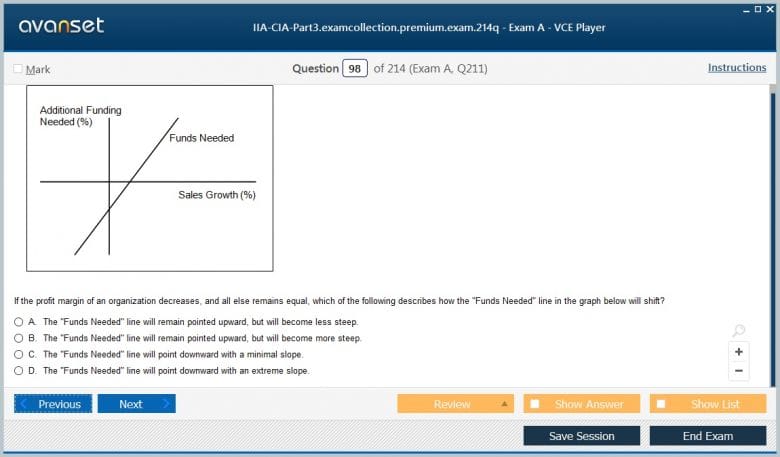
IIA IIA-CIA-Part3 Practice Test Questions in VCE Format
| File | Votes | Size | Date |
|---|---|---|---|
File IIA.train4sure.IIA-CIA-Part3.v2026-09-09.by.hamza.214q.vce |
Votes 1 |
Size 3.42 MB |
Date Sep 09, 2026 |
File IIA.test-inside.IIA-CIA-Part3.v2022-01-10.by.benjamin.186q.vce |
Votes 1 |
Size 2.85 MB |
Date Jan 10, 2022 |
File IIA.prep4sure.IIA-CIA-Part3.v2021-04-28.by.toby.171q.vce |
Votes 1 |
Size 230.45 KB |
Date Apr 28, 2021 |
File IIA.Prepaway.IIA-CIA-Part3.v2019-03-15.by.Gary.128q.vce |
Votes 3 |
Size 166.5 KB |
Date Mar 18, 2019 |
IIA IIA-CIA-Part3 Practice Test Questions, Exam Dumps
IIA IIA-CIA-Part3 (Certified Internal Auditor - Part 3, Business Analysis and Information Technology) exam dumps vce, practice test questions, study guide & video training course to study and pass quickly and easily. IIA IIA-CIA-Part3 Certified Internal Auditor - Part 3, Business Analysis and Information Technology exam dumps & practice test questions and answers. You need avanset vce exam simulator in order to study the IIA IIA-CIA-Part3 certification exam dumps & IIA IIA-CIA-Part3 practice test questions in vce format.
CIA Part 3 is the final stage of the Certified Internal Auditor pathway and, under the 2025 syllabus, is titled “Internal Audit Function.” Unlike Part 2, which concentrates on performing an engagement, Part 3 looks from the chief audit executive and function-management perspective: strategy, resources, the risk-based audit plan, coordination, quality, communication, risk acceptance, and follow-up.
The 2025 blueprint is materially different from older versions that gave Part 3 a large business-knowledge component. Current preparation should therefore follow the IIA’s updated syllabus rather than an old assumption that Part 3 is mainly finance, IT, and general business. The exam now focuses on how a professional internal audit function is organized, directed, measured, and held accountable.
A chief audit executive has to turn the function’s mandate into operating methods, staffing, budget, technology, and a sustainable mix of assurance and advisory work. That requires decisions about internal staff, co-sourcing, external providers, specialization, training, supervision, and performance. Resource planning is not only a budgeting exercise; it is a judgment about whether the function has enough collective competence to address the organization’s risk profile.
Methodology should also evolve. Changes in regulation, technology, business model, standards, stakeholder expectations, or recurring quality findings can justify revising audit procedures and tools. A mature function does not preserve a method merely because it was approved years ago. It monitors whether the method continues to produce timely, reliable assurance.
Capacity planning includes more than headcount. The chief audit executive needs an appropriate mix of industry knowledge, audit technique, technology capability, communication skill, leadership, and specialist expertise. Some needs can be met through hiring and development; others may justify guest auditors, co-sourcing, or external specialists. The governance issue is transparency: when resources are insufficient for the approved plan or emerging risks, the consequences should be communicated rather than hidden through narrower procedures that make completion statistics look better.
The current weighting shows how strongly the exam has moved toward function management: Internal Audit Operations accounts for 25 percent, the Internal Audit Plan for 15 percent, Quality of the Internal Audit Function for 15 percent, and Engagement Results and Monitoring for 45 percent. Part 3 remains a 100-question, 120-minute multiple-choice examination. Nearly half of the blueprint therefore concerns what happens after or across engagements—communicating results, monitoring actions, understanding residual risk, and ensuring unresolved issues reach the right level of governance.
The redesign also explains what happened to the old Part 3 topics. Under the 2019 syllabus, Part 3 devoted separate domains to business acumen, information security, information technology, and financial management. The IIA did not conclude that those subjects stopped mattering. Instead, the 2025 syllabus integrates them into the contexts where internal auditors use them: planning and performing engagements in Part 2 and managing the internal audit function in Part 3. Candidates still need enough business and technology knowledge to recognize risk, but the exam now asks them to apply it through an internal-audit lens.
That difference should shape practice. A technology question may really be about whether the audit plan covers an emerging system risk, whether the function has the competence to review it, or whether another assurance provider’s work can be relied upon. A financial-management issue may appear because it affects risk assessment, performance measures, or an engagement conclusion. The strongest preparation connects technical facts to audit responsibility instead of studying the former business-knowledge domains as a separate general-management exam.
Internal audit needs a strategy that supports the organization without becoming management. The strategy should reflect the mandate, stakeholder expectations, business objectives, risk-management practices, and available resources. Mission and vision statements can clarify direction, but they need to be translated into priorities, capability plans, technology investment, and measures that show whether the function is delivering useful assurance.
Strategy is not static. Major acquisitions, new technology, regulatory change, restructuring, risk events, or shifts in board concern can require revision. The chief audit executive should be able to explain why the function is investing in particular skills or coverage and how those choices improve assurance over the risks that matter most.
The audit plan should emerge from an understanding of the organization’s objectives, risk universe, management risk assessments, regulatory obligations, prior results, emerging issues, stakeholder input, and the work of other assurance providers. A rotating schedule that audits every department every three years may provide coverage, but it is not automatically risk-based if the risk profile changes much faster than the rotation.
The plan also has to be achievable. The chief audit executive should identify resource gaps, communicate the consequences of inadequate capacity, and update the plan when risk changes. Board approval or oversight of the plan does not transfer responsibility for managing the function; it provides governance over priorities, resources, and whether internal audit can fulfill its mandate.
Risk-based planning also has a time dimension. A plan approved at the start of a year can become obsolete after an acquisition, regulatory change, cyber incident, restructuring, new product, major control failure, or shift in strategy. The chief audit executive should maintain a process for sensing those changes and proposing plan adjustments. Flexibility does not mean abandoning governance; significant changes should be communicated through the agreed oversight process so the board understands both the new priorities and what work is being deferred.
Organizations may have compliance, risk management, quality, security, external audit, regulatory review, and other assurance providers. Internal audit should understand their work, assess whether it is reliable, and coordinate where appropriate to reduce duplication and identify gaps. Reliance is not automatic simply because another function calls itself assurance. Competence, objectivity, scope, methodology, evidence, and quality all matter.
The IIA’s Three Lines perspective helps clarify roles. Internal audit can use or consider work from first- and second-line functions while remaining independent from their management responsibilities. The chief audit executive should know where assurance coverage is strong, where it overlaps, and where significant risk has no credible assurance at all.
A quality assurance and improvement program evaluates conformance with the Global Internal Audit Standards and the effectiveness of the internal audit function. Ongoing monitoring, periodic self-assessment, and external assessment each play a role. The objective is not to collect quality paperwork; it is to identify whether methodology, supervision, competence, reporting, and governance arrangements produce reliable professional work.
Nonconformance must be communicated when it affects the function’s scope or operation. The chief audit executive should understand what happened, its impact, actions being taken, and what the board or senior management needs to know. Quality findings should feed improvement plans and may require changes to methodology, training, resources, or governance.
Quality assessment should distinguish conformance from effectiveness. A function can follow documented procedures yet still fail to focus on the organization’s most important risks, communicate too slowly, or lack the competence needed for complex work. Conversely, a useful engagement does not excuse systematic nonconformance with professional standards. The quality program should therefore evaluate methodology and outcomes together, identify root causes of weaknesses, track improvement, and provide the board with a credible view of whether the function is operating as intended.
Internal audit functions often measure cycle time, plan completion, recommendation closure, stakeholder feedback, quality results, budget performance, staff development, and coverage of key risks. Metrics can support accountability, but they can also create bad incentives. A target for “percent of plan completed,” for example, may encourage teams to avoid necessary scope changes or emerging-risk work merely to protect the number.
Useful indicators therefore need context and targets that reflect the function’s objectives. A balanced set can include efficiency, quality, stakeholder relevance, capability, and risk coverage. The chief audit executive should explain what each measure says, what it does not say, and how it informs decisions rather than treating the scorecard as the value of internal audit itself.
Part 3 requires the chief audit executive perspective on reporting results, assessing residual risk, and communicating when management accepts a level of risk that may be unacceptable to the organization. The first step is not automatic escalation to the board. The issue should be discussed with appropriate senior management, understood in context, and escalated through the proper governance process if it remains unresolved.
The chief audit executive also needs protocols for significant errors or omissions in final communications and for reporting findings that management has already resolved. Communication should remain accurate, objective, clear, concise, constructive, complete, and timely. The audience may change, but the evidence supporting the conclusion should not.
Internal audit should monitor whether agreed management actions are implemented and whether the response actually addresses the risk. Completion evidence matters. A ticket marked closed or a policy marked revised does not prove that the control now operates effectively. Depending on risk, follow-up may involve documentation review, targeted retesting, data analysis, management confirmation, or a later engagement.
If management does not implement an agreed action, the function should understand the reason and reassess residual exposure. Delay may be justified by changed priorities, but repeated inaction can require escalation. Follow-up should therefore distinguish administrative status from risk status: an overdue action is important because of the exposure that remains, not simply because a due date was missed.
Current CIA Part 1 2025 teaches the professional foundation, and CIA Part 2 2025 teaches the engagement. Part 3 asks what happens when those responsibilities must be managed across an entire function. The broader CIA pathway becomes much easier to understand when each part is treated as a change in level of responsibility rather than a disconnected syllabus.
Use the current IIA Part 3 blueprint to organize study around operations, strategy, the risk-based plan, coordination, quality, performance, communication, residual risk, and follow-up. The IIA exam inventory can keep related ExamCollection pages connected, but current first-party material should control any standards, language-transition, testing, or policy detail. Practice scenarios should ask what the chief audit executive should do next and which governance relationship makes that action appropriate.
Part 3 scenarios often become easier when the candidate identifies the decision level before choosing an answer. Engagement teams decide how to perform assigned work; the chief audit executive allocates resources, establishes methodology, coordinates assurance, maintains quality, and communicates function-level issues; the board approves or oversees key governance matters; management owns operations and risk responses. Many distractors are plausible actions assigned to the wrong party. Mapping the decision to the accountable role is therefore as important as knowing the technical concept.
Go to testing centre with ease on our mind when you use IIA IIA-CIA-Part3 vce exam dumps, practice test questions and answers. IIA IIA-CIA-Part3 Certified Internal Auditor - Part 3, Business Analysis and Information Technology certification practice test questions and answers, study guide, exam dumps and video training course in vce format to help you study with ease. Prepare with confidence and study using IIA IIA-CIA-Part3 exam dumps & practice test questions and answers vce from ExamCollection.
Purchase Individually
IIA IIA-CIA-Part3 Video Course
Top IIA Certifications

Top IIA Certification Exams
Site Search:

SPECIAL OFFER: GET 10% OFF

Pass your Exam with ExamCollection's PREMIUM files!
SPECIAL OFFER: GET 10% OFF
Use Discount Code:
MIN10OFF
A confirmation link was sent to your e-mail.
Please check your mailbox for a message from support@examcollection.com and follow the directions.

Download Free Demo of VCE Exam Simulator
Experience Avanset VCE Exam Simulator for yourself.
Simply submit your e-mail address below to get started with our interactive software demo of your free trial.