
Pass Your ECCouncil CEH Certification Easy!
ECCouncil CEH Certification Exams Questions & Answers, Accurate & Verified By IT Experts
Instant Download, Free Fast Updates, 99.6% Pass Rate.
$69.99
CEH Product Reviews
Great network security coverage
"I have recently passed the 312-50 CEH exam with the premium VCE dump. Questions are real, and the stuff works! Some questions weren't 100% the same, but the file prepares you for them. I especially appreciated questions on network architecture and related security flaws in the braindump, and I got them all right on the actual exam.
Brandon L."
Just great
"This is a very practical exam and tests your overall competencies as an ethical hacker, so I was very skeptical if it could be passed by using a vce dump. Turned out, it could, and I passed with over 80%. Lots of threat and threat prevention questions, network architecture and vulnerability areas. The vce dump was great, I really recommend Examcollection for this and other exams.
Christopher Y."
I passed
"I've had a nice experience with the 312-50 exam braindump from Examcollection. Not all, but vast majority of questions were exactly the same as what I saw on the exam, and the rest were quite similar. I have truly benefited from the interactive learning experience and advanced network infrastructure questions in my CEH exam preparation. It feels good to pass a challenging exam, so thanks Examcollection!
Trevor U."
Think like a hacker!
"I used this dump, too and I also passed. I was worried about some practical questions and scenarios - whether or not they would be the same on the actual exam. In truth, they were very similar - and differed by very minor details, so they didn't throw me off balance. I also loved the dump for all those security and threat prevention questions - very useful! The thing is, there is plenty of info about online security, but most of it is from a company point of view. This certification exam makes you think like a hacker: this is the point. This braindump has really helped me adjust my mindset... and of course real exam questions were priceless!
Joe F."
I passed!!!
"I am very excited and relieved to tell you that I am now a certified ethical hacker! I studied a lot to pass the 312-50 exam, and certainly Examcollection file was not the only solution I used. However, it was highly useful as it provided me with an exam preview - and real questions! This is a tough exam, with real life scenarios and challenges. Premium VCE file from Examcollection helped me pass with an 86% score!!
Andrew B."
Download Free CEH Practice Test Questions VCE Files
| Exam | Title | Files |
|---|---|---|
Exam 312-50 |
Title CEH Certified Ethical Hacker (312-50v9) |
Files 49 |
Exam 312-50v10 |
Title Certified Ethical Hacker v10 Exam |
Files 9 |
Exam 312-50v11 |
Title Certified Ethical Hacker v11 Exam |
Files 7 |
Exam 312-50v12 |
Title Certified Ethical Hacker v12 Exam |
Files 1 |
Exam 312-50v13 |
Title Certified Ethical Hacker v13 |
Files 1 |
Exam EC0-350 |
Title ECCouncil Certified Ethical Hacker v8 |
Files 7 |
ECCouncil CEH Certification Exam Dumps & Practice Test Questions
Prepare with top-notch ECCouncil CEH certification practice test questions and answers, vce exam dumps, study guide, video training course from ExamCollection. All ECCouncil CEH certification exam dumps & practice test questions and answers are uploaded by users who have passed the exam themselves and formatted them into vce file format.
CEH v13: Ethical Hacking with a Broader Operational Lens
EC-Council’s Certified Ethical Hacker remains one of the most recognizable entry points into structured offensive-security training. The current program is CEH v13 / CEH AI, while EC-Council’s official knowledge-exam prefix remains 312-50. The version-labeled 312-50v13 destination is therefore useful for current v13 preparation, but the “v13” suffix should not be mistaken for EC-Council’s official exam-code format. The curriculum adds AI-related material while retaining reconnaissance, scanning, enumeration, vulnerability analysis, system compromise, web attacks, wireless security, malware, cloud technologies, and defensive awareness.
CEH sits within EC-Council certifications as a broad offensive-security credential. The objective is to expose candidates to the attack lifecycle and the tools and techniques used to identify weaknesses while keeping the work inside authorized and ethical boundaries.
CEH is broad before it is deep
The certification covers many domains, which is both its strength and a common preparation problem. Candidates can encounter networking, operating systems, web applications, wireless technologies, cloud environments, cryptography, malware, social engineering, vulnerability management, and penetration-testing concepts in the same study path. The exam therefore rewards strong foundations and the ability to recognize techniques in context.
Ethical hacking and information security begin with authorization, defined scope, and responsible reporting. CEH is not simply about executing tools; candidates need to understand why a technique is permitted, what evidence it produces, and how the result should be communicated.
Reconnaissance, scanning, and enumeration build the attack path
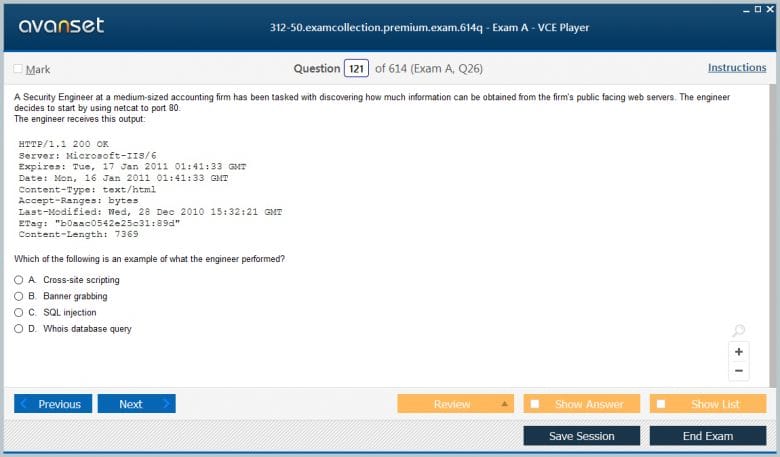
Attackers and penetration testers begin by learning about the target. Passive reconnaissance can reveal domains, technologies, exposed information, employees, and public infrastructure without directly interacting with protected systems. Active reconnaissance goes further by probing services and hosts.
Candidates should understand why information gathered early changes later decisions. Identifying a web application, remote-access gateway, cloud service, or exposed management interface narrows the attack surface. The skill is not memorizing dozens of commands; it is knowing what question each technique answers.
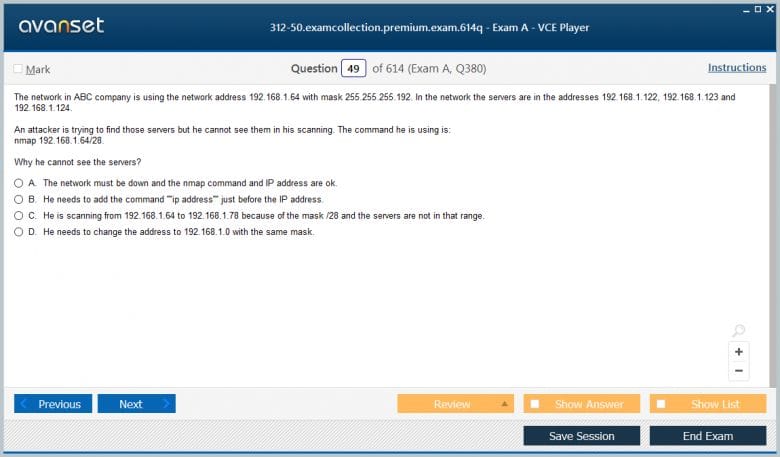
Network scanning identifies hosts, ports, and services. Enumeration attempts to extract more specific information such as users, shares, service details, or protocol data. Tools such as Nmap are useful, but the exam expects candidates to interpret results rather than treat a scan as an end in itself.
The practical lesson in Nmap-based scanning can help candidates understand why scan type, timing, target behavior, and interpretation matter. A discovered port is a clue, not a vulnerability by itself.
Vulnerability assessment and exploitation are different activities
Vulnerability assessment identifies and prioritizes weaknesses. Exploitation demonstrates what an attacker can actually achieve. CEH candidates should distinguish between a scanner finding, a validated vulnerability, and a successful exploit. False positives, environmental controls, compensating measures, and version differences all affect real risk.
Reviewing vulnerability assessment helps reinforce that distinction. A professional tester does not report a scanner output as if it were proof of compromise. Findings should be verified and explained in terms of impact.
Web applications require their own attack model
Modern organizations expose significant functionality through web applications and APIs, so CEH includes common web weaknesses and attack techniques. Candidates should understand input validation, authentication, session handling, access control, injection, client-side behavior, and misconfiguration.
Web application penetration-testing checklists help prevent important classes of weakness from being ignored while the tester follows evidence from the target. They work best as coverage controls, not as instructions to test every application mechanically.
Malware and social engineering show different routes to compromise
CEH does not require candidates to become malware reverse engineers, but it does expect familiarity with malware categories, persistence, command-and-control behavior, delivery methods, and evasion. Understanding malware helps candidates connect exploitation to what happens after initial access.
Malware analysis techniques deepen this area by connecting file and process behavior to indicators, persistence, command-and-control activity, and defensive opportunities. CEH does not require full reverse-engineering depth, but candidates should be able to reason about what different malware behaviors imply.
Security controls can be bypassed when attackers persuade users to disclose information, approve access, open malicious content, or ignore warnings. CEH therefore includes social-engineering concepts alongside technical attacks. Candidates should understand phishing, impersonation, pretexting, baiting, and the role of reconnaissance in making attacks convincing.
Defensive thinking matters here. The right response is not to assume users can be trained never to make mistakes. Organizations need layered controls such as strong authentication, process verification, least privilege, email defenses, and monitoring.
Cloud, identity, and AI expand the modern attack surface
CEH v13 exists in an environment where identities, APIs, cloud services, and SaaS platforms are as important as traditional network hosts. Misconfigured access, exposed storage, weak credentials, overly broad permissions, and insecure automation can create attack paths without a classic perimeter breach.
Candidates who want deeper cloud-security specialization can look toward Certified Cloud Security Engineer. CEH provides offensive context; CCSE focuses more directly on protecting and operating cloud environments.
CEH v13 adds AI-related material, but candidates should avoid treating AI as a separate magical domain. Attackers can use AI to accelerate research, create content, analyze data, or automate parts of an attack. Defenders can use it for analysis and response. The security questions remain familiar: what data is trusted, what action is permitted, what can be manipulated, and what evidence is available?
AI-assisted workflows still require validation. A generated command can be wrong. A model can invent an explanation. Ethical hackers remain responsible for what they execute and report.
CEH and PenTest+ overlap but are not identical.
Candidates often compare CEH with CompTIA PenTest+. Both cover offensive-security concepts, but they come from different certification ecosystems and organize their objectives differently. CEH has a long-standing tool-and-technique orientation across a wide range of attack domains, while PenTest+ places significant emphasis on planning, scoping, analysis, and reporting alongside technical execution.
The comparison is useful because it reminds candidates that professional penetration testing is more than exploitation. Authorization, scope, evidence, communication, and remediation guidance are part of the job.
Digital forensics is the natural view from the other side
Offensive-security knowledge becomes more valuable when candidates understand how activity is detected and investigated. Computer Hacking Forensic Investigator approaches compromise from the evidence side: acquiring, preserving, analyzing, and reporting digital evidence. CEH candidates do not need full forensic depth, but thinking about traces left behind improves both attack understanding and defensive awareness.
How to prepare for CEH v13 and the 312-50 exam
Start with the current objectives and build a lab where you can practice legally. Use vulnerable virtual machines and intentionally insecure applications. Perform reconnaissance, scans, service enumeration, web testing, password attacks in controlled scenarios, wireless exercises where permitted, and basic post-exploitation analysis. For each action, write down what evidence it creates and what defensive control might detect it.
CEH v13 preparation can help organize revision, but hands-on practice should remain tied to the current EC-Council objective map. Tool familiarity without conceptual understanding is fragile because interfaces and versions change.
Scope and authorization should be part of every lab scenario. Before touching a target, define which systems are permitted, which techniques are prohibited, the testing window, evidence-handling expectations, and the stop conditions. That habit prevents candidates from learning offensive techniques as if execution were independent of professional responsibility. It also makes reporting clearer because every finding can be tied back to an agreed objective.
Reporting practice deserves more attention than it usually receives. After a lab, write a short finding with evidence, affected asset, risk, reproduction steps, and remediation. Avoid claiming more than the evidence proves. A vulnerability may be present without having been exploited in the real environment, and a successful exploit in a lab does not automatically establish business impact. Ethical hacking becomes professional security work when technical results are translated into accurate, actionable findings.
Finally, build tool independence. Perform reconnaissance with more than one method, compare scanner output with manual verification, and learn what network or application behavior each tool is observing. This makes CEH knowledge resilient when tools change and reduces the tendency to treat a command as an answer. The exam is easier when candidates understand the security objective behind the utility.
Keep a small technique journal during labs. For each exercise, record the prerequisite, the observable evidence, the likely defensive control, and the remediation. This turns a large CEH syllabus into reusable patterns. Port scanning becomes a visibility problem, credential attacks become an identity-control problem, and web exploitation becomes an input-validation or authorization problem. That compression makes revision much more manageable.
The best CEH preparation connects attack and defense
CEH v13 is most useful when candidates study attacks as cause-and-effect chains. Reconnaissance discovers information, enumeration reveals services or identities, vulnerabilities create opportunities, exploitation gains access, post-exploitation expands impact, and defensive controls attempt to interrupt or detect the chain.
That mindset turns a broad syllabus into a coherent model. Instead of memorizing hundreds of tools, candidates learn to ask what an attacker is trying to achieve, what evidence supports the next step, what risk the action creates, and what a defender could do about it. That is the durable knowledge behind the certification.
As a final check, explain every major technique without naming a tool. If you can describe the objective, prerequisite, evidence, and defensive response in plain language, you understand the concept rather than only the interface.
ExamCollection provides the complete prep materials in vce files format which include ECCouncil CEH certification exam dumps, practice test questions and answers, video training course and study guide which help the exam candidates to pass the exams quickly. Fast updates to ECCouncil CEH certification exam dumps, practice test questions and accurate answers vce verified by industry experts are taken from the latest pool of questions.


ECCouncil CEH Video Courses
Top ECCouncil Certifications

Top ECCouncil Certification Exams
Site Search:




I have looked at the study guide here and tried to compare it with the one my instructor gave me, and this is just super good. As a student who is preparing in a group for the CEH exams, I find this dumps here easy to understand too. Thanks, ExamCollection!
@don charles, from my point of understanding, no you don’t need it. Please try to go through the CEH questions and answers on dumps here. However, the scripting skills may come in handy depending on why you need this certificate.
I have gone through the dumps, and they are just perfect. I found the answers to the CEH exam questions that I had during practice. My only question is on vulnerability scan. Is it true that one needs to master software programing of hacking? Do I have to do a script writing to understand it?