



Premium File
319 Q&A
$76.99$69.99
IAPP CIPP-E Exam Questions & Answers, Accurate & Verified By IT Experts
Instant Download, Free Fast Updates, 99.6% Pass Rate
CIPP-E Premium File: 319 Questions & Answers
Last Update: Sep 06, 2026
CIPP-E Training Course: 30 Video Lectures
$74.99
IAPP CIPP-E Exam Screenshots
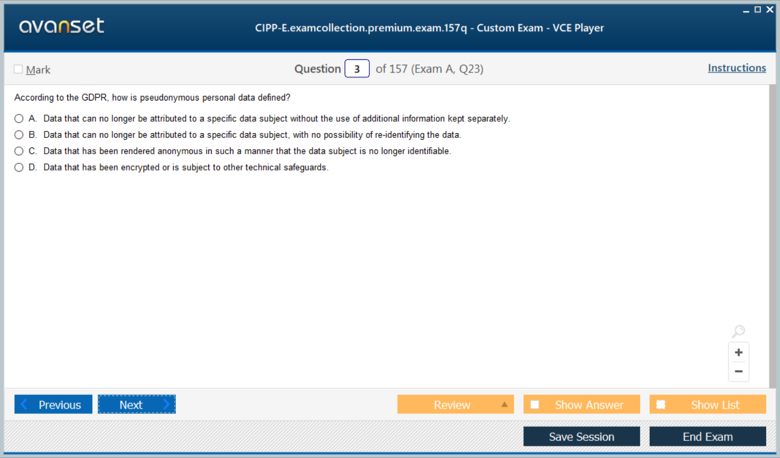
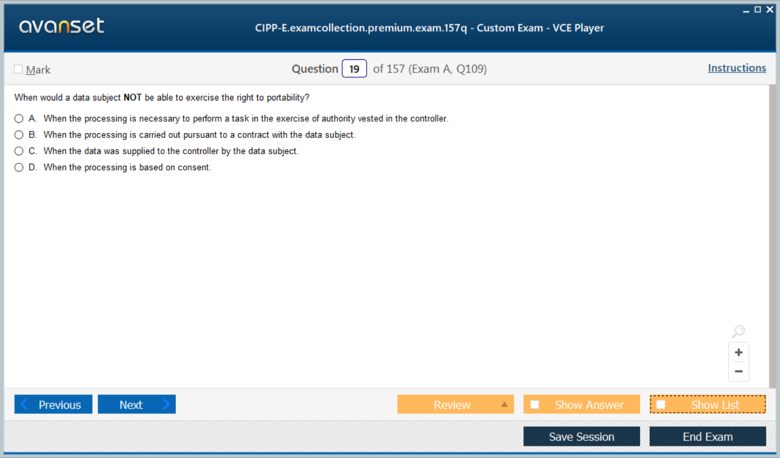
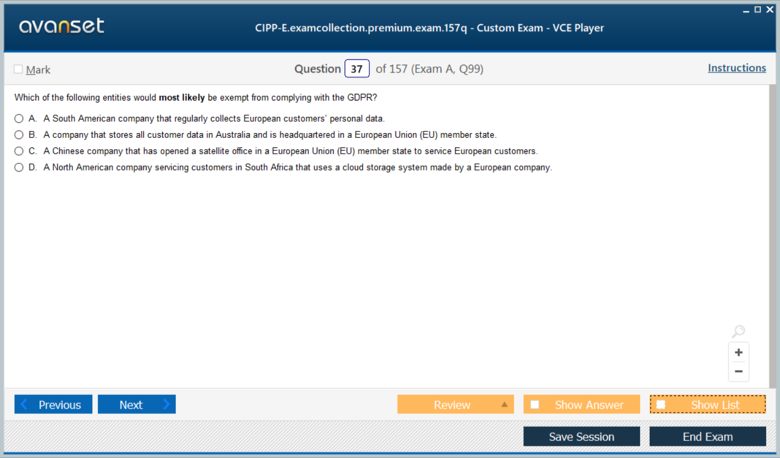
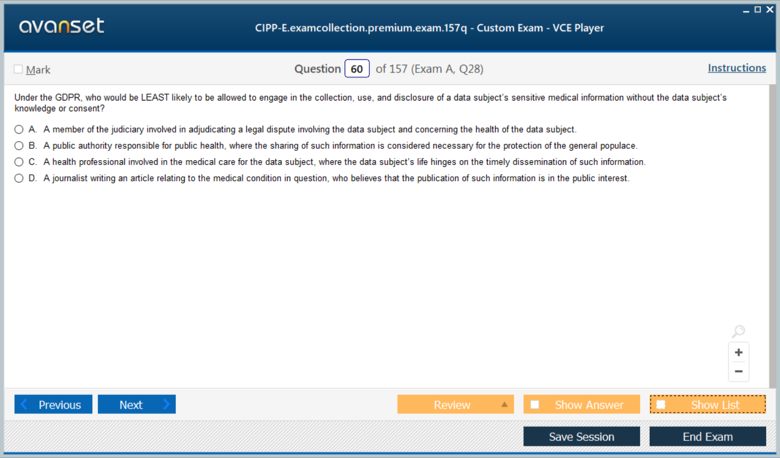
IAPP CIPP-E Practice Test Questions in VCE Format
| File | Votes | Size | Date |
|---|---|---|---|
File IAPP.pass4sure.CIPP-E.v2026-08-13.by.eleanor.116q.vce |
Votes 1 |
Size 343.17 KB |
Date Aug 13, 2026 |
File IAPP.examlabs.CIPP-E.v2021-10-20.by.blake.94q.vce |
Votes 1 |
Size 255.88 KB |
Date Oct 20, 2021 |
File IAPP.test4prep.CIPP-E.v2021-08-26.by.wanglei.78q.vce |
Votes 1 |
Size 216.04 KB |
Date Aug 26, 2021 |
File IAPP.vceplayer.CIPP-E.v2021-04-27.by.brahim.55q.vce |
Votes 1 |
Size 162.73 KB |
Date Apr 27, 2021 |
File IAPP.examdumps.CIPP-E.v2020-07-22.by.ethan.42q.vce |
Votes 2 |
Size 139.59 KB |
Date Jul 22, 2020 |
IAPP CIPP-E Practice Test Questions, Exam Dumps
IAPP CIPP-E (Certified Information Privacy Professional/Europe (CIPP/E)) exam dumps vce, practice test questions, study guide & video training course to study and pass quickly and easily. IAPP CIPP-E Certified Information Privacy Professional/Europe (CIPP/E) exam dumps & practice test questions and answers. You need avanset vce exam simulator in order to study the IAPP CIPP-E certification exam dumps & IAPP CIPP-E practice test questions in vce format.
CIPP/E is IAPP’s European privacy certification, with the General Data Protection Regulation at the center of the current blueprint and related European institutions, laws, transfer rules, and compliance practices around it. The exam is not a recital-memory contest. It tests whether candidates can take facts about an organization, processing activity, or data flow and determine the roles, principles, legal basis, rights, accountability duties, and enforcement implications.
A strong study framework starts with scope and role. Ask whether the GDPR applies territorially and materially, whether the organization is a controller, joint controller, or processor, what categories of data are involved, why processing occurs, where the data moves, and who is affected. Those decisions determine most of the later analysis.
CIPP/E candidates need context for how European data protection developed and how EU institutions, national authorities, courts, and human-rights principles interact. The GDPR sits within a wider legal environment that includes communications, cybersecurity, and newer digital regulation. Understanding that structure helps explain why data protection is treated as a rights-based compliance system rather than only a security requirement.
Do not spend all study time on historical detail, but know enough to place the GDPR in its institutional setting. A regulator’s authority, consistency mechanisms, court decisions, and national implementation can affect interpretation. The relationship between privacy, security, and legislation can provide useful background, provided the current IAPP material remains the source for European exam scope.
Territorial scope can reach organizations outside the EU in defined circumstances, while material scope identifies processing that falls inside or outside the regulation. Once scope is established, role classification becomes critical. Controllers determine purposes and essential means; processors act on behalf of controllers under defined instructions; joint control can arise when decisions are shared.
Practice with platform ecosystems and outsourced services. Identify who decides the purpose of processing, who selects material means, who merely provides infrastructure, and where responsibilities overlap. Contract labels are evidence but not the final answer if actual behavior differs. Role analysis affects notices, contracts, rights handling, records, security, breach duties, and liability.
Lawfulness, fairness, transparency, purpose limitation, data minimization, accuracy, storage limitation, integrity and confidentiality, and accountability are not isolated slogans. They provide a structured test for a processing activity. A project can have a plausible legal basis and still violate minimization or transparency; a secure database can still retain personal data longer than necessary.
Build a principle review for a loyalty program or employee analytics tool. Write the purpose, data fields, source, recipients, retention, security, and user communication, then evaluate each principle. The discipline is similar to organizational privacy practice, but the CIPP/E candidate must tie the analysis to European legal requirements and accountability evidence.
Consent is only one legal basis. Contract, legal obligation, vital interests, public task, and legitimate interests can be relevant depending on the situation, while special-category data generally requires an additional condition. Candidates should understand the characteristics and limits of each basis rather than choose consent by default.
Use scenarios where the preferred business basis is unavailable. An employer may face power imbalance; a service cannot label every optional analytics purpose as contract necessity; legitimate interests requires a structured assessment. For sensitive information, identify both the ordinary legal basis and the special-category condition. This two-layer reasoning is a frequent point of confusion.
Access, rectification, erasure, restriction, portability, objection, and rights related to automated decision-making have conditions and exceptions. Candidates should know what triggers each right, how identity is verified, how deadlines work, and how requests interact with processors or complex systems. Rights should be studied as operational events, not just a memorized list.
Compare the legal rule with privacy-program operations. A controller may understand that a right exists but still fail if data cannot be located or if downstream systems are not included. Mapping the request from intake to search, legal review, action, response, and evidence shows why accountability depends on process design.
Personal data moving beyond the European Economic Area can require an approved transfer mechanism and, depending on the context, additional assessment and safeguards. Candidates should understand adequacy, contractual mechanisms, binding corporate rules, derogations, and the practical evaluation of destination-country risks without treating every transfer as identical.
Draw a cloud architecture with controllers, processors, subprocessors, support access, and backup locations. Mark each transfer and identify the mechanism that might support it. Then consider government-access risk, encryption, key control, minimization, and contractual commitments. Transfer analysis becomes much clearer when it follows real data movement rather than a standalone list of legal instruments.
Records of processing, data-protection impact assessments, privacy by design and default, processor due diligence, security measures, training, policies, and data-protection officer responsibilities all support accountability. The common thread is evidence: an organization should be able to show why a risky processing activity was allowed and which safeguards were selected.
DPIAs are especially useful study vehicles because they combine purpose, necessity, proportionality, risks to individuals, safeguards, consultation, and approval. Build one for biometric access or large-scale profiling. If the residual risk remains high, understand when escalation or regulator consultation may become relevant.
Direct marketing, cookies or tracking, workplace monitoring, video surveillance, biometrics, connected devices, and AI combine core GDPR duties with sector or context-specific rules. Candidates should resist the urge to memorize one universal answer. The facts—relationship, expectation, channel, sensitivity, scale, and legal environment—determine the analysis.
AI is a good example of overlapping governance. AIGP addresses broader responsible-AI lifecycle controls, while CIPP/E asks how personal-data processing within an AI system complies with European data-protection law. Privacy and AI governance may share inventories and assessments, but the obligations and legal tests should remain distinct.
Current preparation must account for a changing European landscape. IAPP explicitly updates CIPP/E material as European privacy and technology regulation changes, so the current Body of Knowledge and Exam Blueprint should govern final preparation. Older study guides can still explain stable GDPR concepts, but they may miss newer regulatory context, enforcement developments, or technology issues reflected in the active exam.
Across the wider IAPP certifications program, CIPP/E is the legal and jurisdictional layer. CIPT extends privacy into technology design, while CIPM operationalizes programs. A CIPP/E candidate should know where those disciplines intersect without drifting away from European legal analysis.
Finish with complex fact patterns: a U.S. SaaS provider offering services to EU users, an employer deploying monitoring, a retailer using behavioral advertising, and a health platform training an AI model. For each, determine scope, role, legal basis, sensitive-data issues, transparency, rights, transfers, security, assessments, and likely accountability evidence. The sequence is far more valuable than memorizing article numbers without application.
Data protection officers and representative roles should be understood by trigger and independence, not by title alone. Determine when a DPO is required, what expertise and resources the role needs, how conflicts of interest are avoided, and how the DPO advises and monitors without becoming the owner of every processing decision. Accountability still rests with the controller or processor; appointing a specialist does not transfer legal responsibility away from management.
Children’s data and vulnerable individuals can heighten fairness, transparency, and design concerns. Age-appropriate information, parental authorization where relevant, profiling, behavioral advertising, and high-risk services require careful analysis. The candidate should be able to identify when ordinary notice language or interface choices are inadequate for the audience even before considering sector-specific rules.
Enforcement study should connect supervisory-authority powers to the organization’s evidence. Regulators can investigate, obtain information, order corrective action, restrict processing, and impose administrative fines within the legal framework. Scenario questions become easier when candidates ask what the authority would request: records, assessment reasoning, security evidence, contracts, notices, consent records, or proof that rights requests were handled correctly.
Processor governance deserves practical attention because modern services rely on cloud, SaaS, analytics, and support providers. Controllers must choose processors providing sufficient guarantees, establish required contractual terms, understand subprocessors, and monitor material changes. Processors have their own direct obligations as well. Draw the chain of parties in a cloud service and label controller, processor, subprocessor, transfer, and responsibility at each boundary.
Data protection by design and default should influence default settings, collection fields, access, retention, and feature architecture. The word “default” is important: users should not need expert knowledge to prevent unnecessary exposure. Practice reviewing a new product before launch and identify which privacy choices can be solved structurally rather than through another notice. Design decisions often provide stronger compliance than relying on users to manage complex settings later.
Case law and regulatory guidance can change how stable statutory text is interpreted, so study updates by issue rather than trying to memorize every decision. Keep a short change log for transfers, cookies and tracking, employee monitoring, AI, biometrics, and enforcement. When a new development appears, ask which existing principle or obligation it changes. This preserves the GDPR framework while keeping preparation current.
Records of consent, legitimate-interest assessments, DPIAs, processor reviews, transfer assessments, and rights responses should be treated as connected accountability evidence. During revision, pick one processing activity and assemble the full evidence package that would support it. This shows how legal basis, transparency, contracts, security, transfers, and rights fit together around one real operation rather than existing as independent GDPR chapters.
Go to testing centre with ease on our mind when you use IAPP CIPP-E vce exam dumps, practice test questions and answers. IAPP CIPP-E Certified Information Privacy Professional/Europe (CIPP/E) certification practice test questions and answers, study guide, exam dumps and video training course in vce format to help you study with ease. Prepare with confidence and study using IAPP CIPP-E exam dumps & practice test questions and answers vce from ExamCollection.
Purchase Individually
IAPP CIPP-E Video Course
Top IAPP Certifications

Site Search:

SPECIAL OFFER: GET 10% OFF

Pass your Exam with ExamCollection's PREMIUM files!
SPECIAL OFFER: GET 10% OFF
Use Discount Code:
MIN10OFF
A confirmation link was sent to your e-mail.
Please check your mailbox for a message from support@examcollection.com and follow the directions.

Download Free Demo of VCE Exam Simulator
Experience Avanset VCE Exam Simulator for yourself.
Simply submit your e-mail address below to get started with our interactive software demo of your free trial.
@faith51, yes, suppose their dumps for CIPP/E exam will be of the same high quality ws the rest materials provided there...cool web platform ☺
hey?? When will the dumps for CIPP/E exam be uploaded????need them asap. Disappointed with those that I had found in the internet….
@adam, I’m also in the queue))))))))) need the most valid and actual practice questions and answers for CIPP/E exam ……and know that EC is the right place…..so, hope will get soon,,,, training their dumps in the VCE soft is smth unreal. Always ready and passed from the 1st attempt!!!
@adam, yes, I also highly appreciate the material provided there…..and waiting for IAPP CIPP/E exam dumps…the ones I found on the internet is undoubtedly useful in this exam. i practiced with it several times and passed with great results. wish you the best!
has anyone found the best practice tests for CIPP/E exam……. are they useful? Still, I’m waiting for the material from this website, it’s the most actual and valid…..i know what i’m saying……
Well….i’m taking the exam soon and need the most updated material…so needed in vce files for this CIPP/E assessment….examcollection team…please assist and provided the latest ones!!
Interested in preparing CIPP/E exam
just want to get an idea of the course and exam
interesting!