



Premium File
158 Q&A
$76.99$69.99
Novell 050-733 Exam Questions & Answers, Accurate & Verified By IT Experts
Instant Download, Free Fast Updates, 99.6% Pass Rate
158 Questions & Answers
Last Update: Oct 30, 2026
$69.99
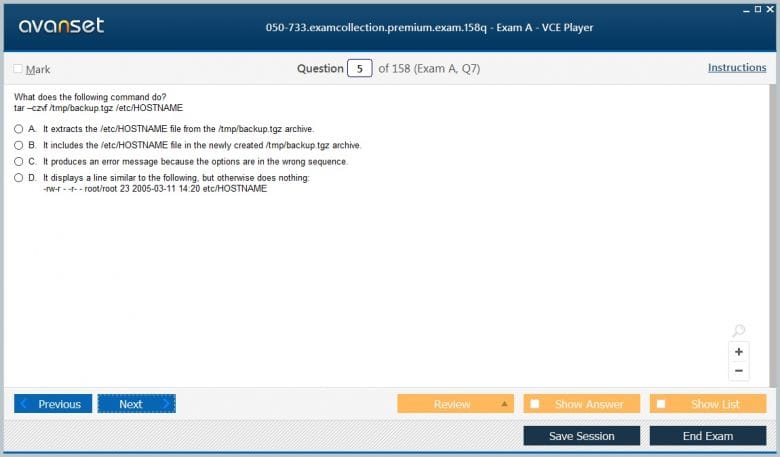
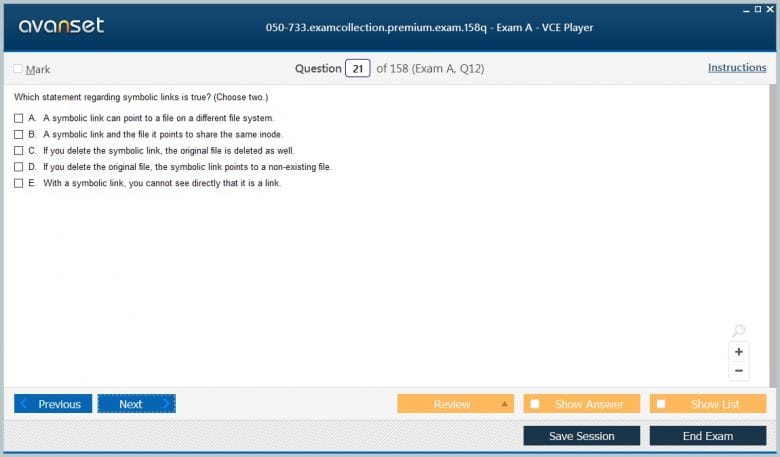
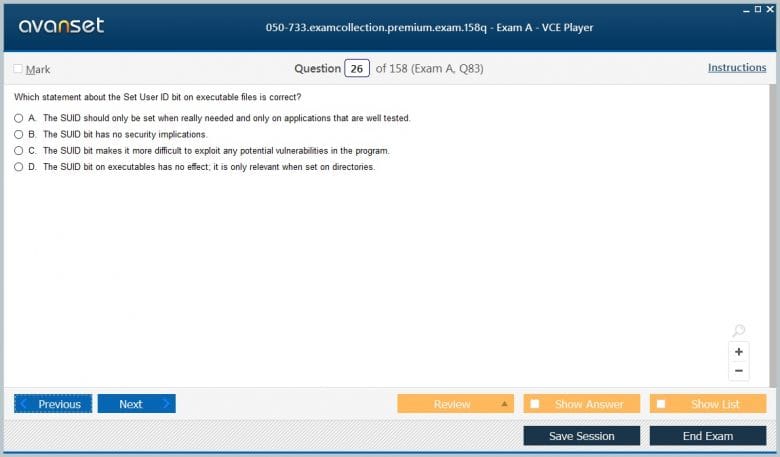
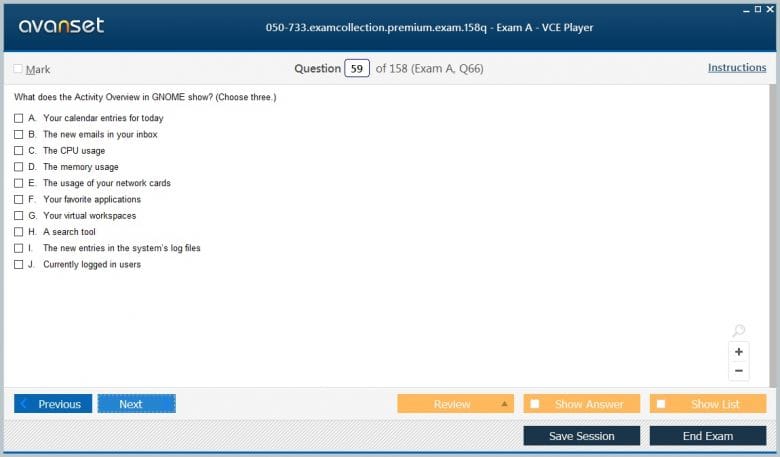
Novell 050-733 Exam Screenshots
Novell 050-733 Practice Test Questions in VCE Format
| File | Votes | Size | Date |
|---|---|---|---|
File Novell.Train4sure.050-733.v2026-08-20.by.Matty.80q.vce |
Votes 3 |
Size 79.1 KB |
Date Aug 21, 2026 |
File Novell.Prep4sure.050-733.v2016-07-10.by.Greg.45q.vce |
Votes 14 |
Size 42.24 KB |
Date Jul 11, 2016 |
Novell 050-733 Practice Test Questions, Exam Dumps
Novell 050-733 (SUSE Certified Linux Administrator 12) exam dumps vce, practice test questions, study guide & video training course to study and pass quickly and easily. Novell 050-733 SUSE Certified Linux Administrator 12 exam dumps & practice test questions and answers. You need avanset vce exam simulator in order to study the Novell 050-733 certification exam dumps & Novell 050-733 practice test questions in vce format.
SLES 12 makes the 050-733 exam a useful marker in the evolution of enterprise Linux administration. The code belongs to the legacy SUSE Certified Linux Administrator era within the broader Novell ecosystem, while SUSE now maintains a modern administrator path around current SLES releases. The historical value of 050-733 comes from the transition it captures, especially systemd, Btrfs-oriented recovery, and changing network and lifecycle tooling.
SLES 12 nevertheless marked an important operational transition. Compared with the earlier SLES 11 generation, administrators encountered systemd as the service and boot-management framework, Btrfs and snapshot-oriented administration became more prominent, and networking and lifecycle tooling continued to evolve. The exam therefore captures both enduring Linux fundamentals and release-specific changes that shaped later enterprise Linux administration.
The historical Novell certification catalog also contains the earlier SUSE Linux Administrator 11 exam. Comparing the two is useful because it shows exactly where stable administrator responsibilities survive a platform transition and where operational procedures change.
One of the defining SLES 12 changes is the move to systemd. Instead of treating startup mainly as a sequence of legacy init scripts and runlevels, systemd manages units with explicit dependencies, targets, activation behavior, and status information. Administrators need to understand what a unit represents, how it is enabled for future boots, how it is started immediately, and how failures are reported.
Distinguish state from configuration. A service can be active now but not enabled for the next boot, or enabled but failing to start because a dependency or configuration is broken. Checking only one command can therefore give an incomplete picture. Inspect unit state, recent logs, dependency failures, sockets, and the application's own configuration.
Practice converting operational questions into systemd questions: what starts this service, what must be available first, which target pulls it in, what happened on the last start, and what changed immediately before failure? This model scales better than memorizing a list of service commands.
Even as management frameworks change, the command line remains central. Administrators still need to navigate files, search content, inspect processes, redirect output, build pipelines, and automate repeatable work. The concepts behind Linux input, output, and pipes are therefore as important for SLES 12 as they were for earlier releases.
Shell scripting becomes valuable when a task must be repeated consistently. Variables, tests, loops, exit status, quoting, functions, and safe input handling allow simple operational checks to become utilities. Bash scripting should be practiced with small administrative jobs such as verifying mounts, checking service state, parsing logs, or validating that expected users and groups exist.
Automation should fail clearly. A script that silently continues after an important command fails can create more damage than manual administration. Check exit codes, validate assumptions, quote variables correctly, and write output that helps the next administrator understand what happened.
SLES 12 made Btrfs and snapshot-based administration more visible, especially for system volumes. A snapshot is not the same as an independent backup, but it can provide a fast way to compare or roll back filesystem state when used appropriately. Administrators need to understand what is captured, where snapshot data lives, and what failures a local snapshot cannot protect against.
Storage still begins with block devices, partitions, volume management, filesystems, and mount points. Use filesystem and block-device tools to identify the real layer that is full or unavailable. Confirm persistent mount configuration before rebooting. Where LVM is used, understand physical volumes, volume groups, and logical volumes before resizing.
Plan recovery before change. A package update or configuration edit that can be rolled back quickly is less risky, but only if the administrator knows the correct snapshot state and has tested the recovery mechanism. Critical data still needs an independent backup strategy because a failed disk or corrupted storage pool can remove both live data and local snapshots.
SUSE uses RPM packaging with Zypper and YaST as important administration tools. Candidates should be able to query installed packages, manage repositories, refresh metadata, install and remove software, and apply updates while understanding dependency resolution. Repository configuration is part of the trust and support model, not merely a download list.
When package operations fail, separate connectivity, metadata, signature trust, dependency conflicts, and product-subscription questions. Verify which repositories are enabled and which package versions they expose before forcing an installation. A workaround that bypasses dependency or trust checks can leave the system in a state that is harder to support.
Release-specific lifecycle rules matter. SLES 12 procedures should not be assumed to match current SLES 15 module, extension, or update workflows. The durable skill is being able to inspect the configured software sources and understand what the package manager is trying to resolve.
SLES 12 networking can be administered through SUSE tools as well as standard Linux diagnostics. Regardless of interface, know the resulting address, prefix, route, DNS settings, and interface state. Then verify reachability in layers: local interface, local gateway, routed destination, name resolution, transport port, and application response.
Do not confuse a temporary diagnostic change with a permanent fix. Adding a route or address interactively can test a hypothesis, but the correct release-appropriate persistent configuration still has to be applied. Document the intended topology so a later automated or manual change does not silently undo the repair.
Network failures also intersect with services and firewall rules. If a daemon is listening on the correct address but remote clients cannot connect, inspect routes and packet-filter policy before editing the application. If the port is not listening locally, fix the service first rather than opening more firewall rules.
Troubleshooting should proceed from observable state rather than from the configuration file an administrator expects the system to be using. Confirm the running kernel view, active routes, mounted filesystems, loaded units, open sockets, package versions, and current resource pressure. Then compare that state with the intended persistent configuration. This distinction is especially important after emergency changes, because a temporary fix may remain active until reboot while the underlying configuration is still wrong.
Accounts, groups, file ownership, and permission modes remain fundamental. Know how primary and supplementary groups affect access, how umask influences new files, and how setuid, setgid, and sticky-bit behavior changes specific access patterns. Administrative privilege should be granted deliberately and reviewed rather than shared through common root credentials.
Design a shared directory for a team and test creation, modification, and deletion by multiple users. Then inspect the effect of default group ownership and permission masks. This exercise exposes common errors that are easy to miss when permissions are studied only as octal numbers.
Account lifecycle also affects security. Disable or remove unused access, protect SSH keys and administrative credentials, and review services that run under privileged identities. A local permission model can be correct while a weak service account still creates an unnecessary path to the system.
SLES 12 administrators need to work comfortably with the logging model around systemd while still recognizing traditional log files used by applications and system components. The goal is correlation: identify when a failure occurred, what component reported it first, and what related event happened immediately before it.
Use time-bounded queries during incident analysis. Looking at every message since boot can hide the relevant sequence. Follow one service start, one authentication attempt, or one network change across the journal and application logs. Record timestamps and error identifiers before making changes so the evidence is not lost.
Logs also support security monitoring. Repeated failed authentication, unexpected privilege use, service crashes, or firewall drops can reveal behavior that ordinary availability monitoring misses. Protect log integrity and ensure rotation or retention settings do not remove evidence too quickly.
Patch management, least privilege, service minimization, secure remote access, file permissions, auditability, and packet filtering all contribute to system security. The fundamentals of iptables and Linux firewalls remain useful for understanding how traffic is matched and allowed or denied, even though firewall tooling evolves across Linux releases.
Build policy from required services. Identify which hosts need to reach each daemon, on which interfaces and ports, and whether administration should be isolated from ordinary application traffic. A permissive rule that restores connectivity is useful as a temporary diagnostic but should not become the final policy without understanding what it exposes.
Security also means keeping the platform within a supported lifecycle. Historical SLES 12 lab work should be separated from production decisions, and unsupported software should not be exposed casually. Use current SUSE guidance for present-day hardening and updates.
A productive lab compares SLES 11-era and SLES 12-era administration tasks. Start the same service on both, inspect startup configuration, manage a package, configure a network interface, create a filesystem, add users, and collect logs. Note which concepts remain identical and which tools or defaults changed. That comparison builds transferable understanding.
Then map those concepts to the current SUSE Certified Administrator path. Broader discussion of Linux certifications can help place SUSE alongside other vendor and distribution credentials, but the current SUSE certification catalog should decide which exam code and release are active.
050-733 is a valuable historical marker because it sits at a real systems-administration transition. The lasting lesson is not a particular command. It is the ability to understand service dependencies, storage state, software sources, network behavior, permissions, logs, and security well enough to adapt when the platform underneath those responsibilities changes.
Go to testing centre with ease on our mind when you use Novell 050-733 vce exam dumps, practice test questions and answers. Novell 050-733 SUSE Certified Linux Administrator 12 certification practice test questions and answers, study guide, exam dumps and video training course in vce format to help you study with ease. Prepare with confidence and study using Novell 050-733 exam dumps & practice test questions and answers vce from ExamCollection.
Purchase Individually
Site Search:

SPECIAL OFFER: GET 10% OFF

Pass your Exam with ExamCollection's PREMIUM files!
SPECIAL OFFER: GET 10% OFF
Use Discount Code:
MIN10OFF
A confirmation link was sent to your e-mail.
Please check your mailbox for a message from support@examcollection.com and follow the directions.

Download Free Demo of VCE Exam Simulator
Experience Avanset VCE Exam Simulator for yourself.
Simply submit your e-mail address below to get started with our interactive software demo of your free trial.