



Premium File
62 Q&A
$76.99$69.99
CIW 1D0-571 Exam Questions & Answers, Accurate & Verified By IT Experts
Instant Download, Free Fast Updates, 99.6% Pass Rate
62 Questions & Answers
Last Update: Oct 26, 2026
$69.99
CIW 1D0-571 Exam Screenshots
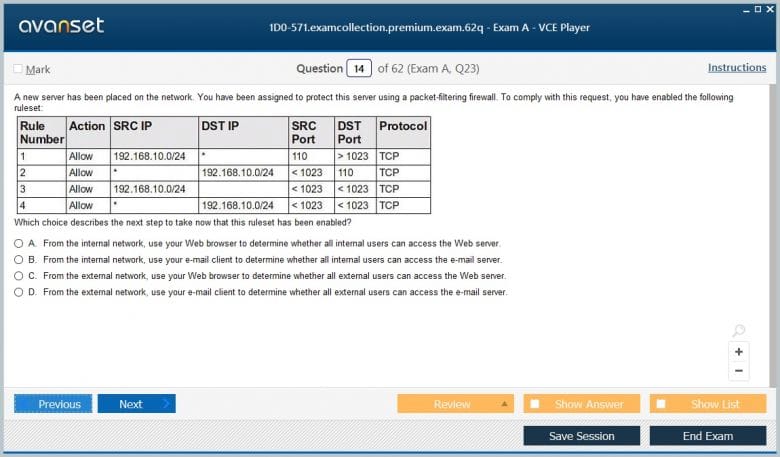
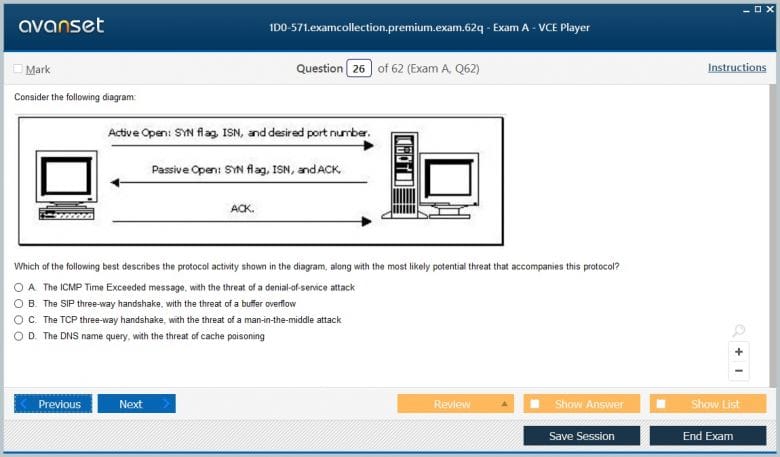
CIW 1D0-571 Practice Test Questions in VCE Format
| File | Votes | Size | Date |
|---|---|---|---|
File CIW.Test-king.1D0-571.v2026-09-15.by.Zoey.39q.vce |
Votes 5 |
Size 99.79 KB |
Date Sep 19, 2026 |
File CIW.ActualTests.1D0-571.v2012-09-20.by.getitcert.62q.vce |
Votes 11 |
Size 478.85 KB |
Date Sep 20, 2012 |
Archived VCE files
| File | Votes | Size | Date |
|---|---|---|---|
File CIW.Pass4Sure.1D0-571.v2011-08-18.by.DGH.62q.vce |
Votes 1 |
Size 730.74 KB |
Date Aug 18, 2011 |
CIW 1D0-571 Practice Test Questions, Exam Dumps
CIW 1D0-571 (CIW v5 Security Essentials) exam dumps vce, practice test questions, study guide & video training course to study and pass quickly and easily. CIW 1D0-571 CIW v5 Security Essentials exam dumps & practice test questions and answers. You need avanset vce exam simulator in order to study the CIW 1D0-571 certification exam dumps & CIW 1D0-571 practice test questions in vce format.
CIW 1D0-571 Web Security Associate retired on December 31, 2021 according to CIW’s official retirement record. CIW continues to offer a Web Security Associate program under a later exam version, so 1D0-571 should be treated as a historical code rather than a current scheduling target. Its central subject—protecting networks and web-facing systems from unauthorized activity—remains highly relevant.
The modern attack surface is larger than the one candidates faced when 1D0-571 was active. Cloud identities, SaaS applications, APIs, containers, remote endpoints, software dependencies, and CI/CD systems all create paths to sensitive data. Yet current CIW course material still emphasizes recognizable fundamentals: policy, threats, authentication, encryption, protocols, firewalls, VPNs, attack detection, and incident response.
The legacy code belongs within CIW certifications. It also connects historically with the older 1D0-470 Security Professional, while the current CIW Network Technology Associate remains a useful foundation because defenders cannot secure network traffic they do not understand.
Organizations cannot protect everything equally. Asset inventory identifies systems, data, identities, services, and dependencies that support business operations. Classification then helps determine which assets require stronger access, encryption, monitoring, retention, or recovery controls. A forgotten internet-facing server can be more dangerous than a heavily monitored critical system because nobody owns its risk.
Threat modeling adds context by asking who might attack, what they want, which paths are exposed, and what controls already exist. The objective is not to predict every attacker action. It is to identify credible abuse cases early enough that architecture and operations can reduce the impact.
Risk decisions should be documented. Accepting a risk, transferring it, mitigating it, or avoiding it are all legitimate choices when made knowingly. Security work becomes ineffective when every finding is labeled critical without considering exposure and consequence.
Authentication establishes identity; authorization determines allowed actions. A secure web application enforces both on the server. Hiding administrative buttons in the browser does not prevent a user from directly calling an endpoint. Every sensitive request needs an authorization decision based on the authenticated identity and the target resource.
Passwords should be protected with modern hashing practices and complemented by multifactor authentication where appropriate. Account recovery deserves equal attention because a strong login can be bypassed by a weak reset process. Rate limiting, anomaly detection, and protection against credential stuffing also matter for internet-facing services.
Sessions and tokens need lifecycle controls. Secure cookies, expiration, rotation, logout behavior, revocation, and protection against cross-site attacks all affect whether a valid login remains safe. Long-lived tokens can become durable attacker credentials if copied from logs, browsers, or compromised devices.
TLS protects data in transit, but a secure connection depends on protocol versions, certificate validity, trusted issuers, hostname verification, and safe key management. Users often see only the browser lock icon, while administrators must manage the full certificate lifecycle and ensure services reject invalid peers where mutual trust is required.
Encryption at rest protects storage media and backups, but applications still need access to plaintext at some point. Permissions and key-management systems therefore remain critical. Keys should not be stored beside encrypted data in a way that gives the same compromised account access to both.
Hashing and digital signatures serve different purposes from encryption. Hashes help verify integrity, while signatures can prove origin and integrity when keys are protected. Security education is strongest when candidates understand which property a cryptographic mechanism provides rather than memorizing algorithm names.
Web security requires enough networking knowledge to understand what services are reachable and how they communicate. TCP and UDP, common application protocols, DNS, routing, and network address translation all influence exposure. An unexpected listening service can create risk even when the primary web application is correctly configured.
Protocol layering also supports troubleshooting. If DNS fails, the user may report that the website is down even when the server is healthy. If TLS negotiation fails, TCP connectivity may still be fine. Separating layers lets defenders identify the actual control or dependency that is broken.
The broader OSI and network-security relationships help explain why defenses appear at multiple layers. Firewalls, application gateways, endpoint controls, and identity policy solve different parts of the same communication problem.
A firewall is most useful when the organization knows which paths should exist. Rules should identify source, destination, protocol, port, direction, and business purpose. Broad “any-to-any” access weakens segmentation and makes later audits difficult because nobody can tell which traffic is actually required.
Host firewalls add protection close to the workload, while network firewalls and cloud security controls enforce boundaries between segments. The discussion of iptables and Linux firewall fundamentals demonstrates the same principle at the operating-system level: filtering is strongest when policy is explicit and minimal.
Segmentation also limits blast radius. If a web server is compromised, it should not automatically reach every internal database, administrative interface, and workstation. Separate zones and narrow service-to-service rules make attacker movement harder and provide clearer monitoring points.
Virtual private networks encrypt traffic across untrusted networks and can authenticate users, devices, or sites. Traditional remote-access VPNs often place a user logically inside the enterprise network, which can create excessive reach if internal segmentation is weak.
Modern access designs increasingly combine identity, device posture, and application-specific policy. The concepts in VPN architecture and tunneling remain useful because secure remote access still depends on authentication, route control, encryption, and understanding which traffic enters the tunnel.
VPN infrastructure itself needs hardening and patching because it is usually internet-facing and privileged. Logging should show who connected, from where, for how long, and which failures occurred without recording sensitive credential material.
Attackers can manipulate URLs, headers, cookies, form fields, files, API bodies, and browser behavior. Applications should validate input according to business rules, encode output for the destination context, enforce authorization on every protected object, and use safe APIs for database access and operating-system interaction.
SQL injection remains a classic example because it occurs when data is treated as executable query syntax. Preventing SQL injection requires parameterized queries, least-privileged database access, and careful handling of dynamic query requirements. Input filtering alone is not a reliable primary defense.
Cross-site scripting, cross-site request forgery, insecure file upload, broken access control, and vulnerable dependencies create different trust-boundary failures. Security testing should include authenticated workflows and business logic rather than rely only on unauthenticated scanning.
Logs can reveal failed logins, suspicious requests, privilege changes, new administrative accounts, unusual outbound connections, and changes to critical files. Centralized collection helps correlation, but security teams should know which events require action. An enormous log archive without rules, retention, and responsible owners does not create effective detection.
Alert severity should reflect business context and confidence. A single failed login is usually normal; thousands across many accounts may indicate credential stuffing. A new administrator account during a planned deployment differs from one created at an unusual time by an unexpected identity. Detection improves when identity, asset, and change information are available together.
Threat hunting and proactive review can discover behavior that static alerts miss, but they depend on trustworthy telemetry. Time synchronization, consistent host identifiers, preserved audit logs, and known baselines make investigations far more reliable.
An incident-response plan should define who can contain systems, revoke accounts, communicate with stakeholders, preserve evidence, and authorize restoration. The structure in a strong incident-response program reflects the need for preparation before an emergency. Teams that improvise authority during a breach lose valuable time.
Containment should be proportionate. Disconnecting a compromised host may stop attacker activity but can also destroy volatile evidence or interrupt a critical service. Responders need enough context to choose actions that reduce harm while preserving investigative value.
Recovery should include root-cause remediation and validation, not simply returning systems to service. If stolen credentials or a vulnerable dependency remain, restoration can recreate the compromise. Post-incident review should identify technical and process improvements without becoming a blame exercise.
Exercises should test communications and evidence handling as well as technical containment. Security incidents may require coordination among engineering, legal, privacy, customer support, leadership, and external partners. Clear escalation paths and preserved timelines help the organization make decisions from verified facts instead of fragmented chat messages and assumptions.
Continuing education should follow the same evidence-driven approach. New vulnerabilities and attack techniques matter most when teams can connect them to their own assets, identities, dependencies, and controls. Security knowledge stays useful when it changes configuration, detection, architecture, or response practice rather than remaining a list of headlines.
1D0-571 retired because certification programs and technology evolve, not because its subjects stopped mattering. Current defenders still need policy, authentication, cryptography, network protocols, firewalls, VPNs, application security, monitoring, and incident response. What changes is the environment in which those controls are applied.
Cloud services move many controls into identity policies and APIs. DevOps pipelines make build systems part of the production trust chain. Remote work makes endpoint posture more important. Modern web applications depend on third-party code and services that require supply-chain awareness. A current study plan should extend the legacy foundation into these newer areas.
For candidates, the practical message is simple: do not prepare for 1D0-571 as though it were live. Use current CIW Web Security Associate information for scheduling and exam objectives. Use the retired code as a historical map of durable security fundamentals that continue to underpin modern defensive work.
Go to testing centre with ease on our mind when you use CIW 1D0-571 vce exam dumps, practice test questions and answers. CIW 1D0-571 CIW v5 Security Essentials certification practice test questions and answers, study guide, exam dumps and video training course in vce format to help you study with ease. Prepare with confidence and study using CIW 1D0-571 exam dumps & practice test questions and answers vce from ExamCollection.
Purchase Individually
Site Search:

SPECIAL OFFER: GET 10% OFF

Pass your Exam with ExamCollection's PREMIUM files!
SPECIAL OFFER: GET 10% OFF
Use Discount Code:
MIN10OFF
A confirmation link was sent to your e-mail.
Please check your mailbox for a message from support@examcollection.com and follow the directions.

Download Free Demo of VCE Exam Simulator
Experience Avanset VCE Exam Simulator for yourself.
Simply submit your e-mail address below to get started with our interactive software demo of your free trial.
1D0-571 practice questions and answers are among the top materials I used to prepare for my exam. and they did a great job I sharpening my knowledge in all areas of the exam… i didn’t even struggle to pass! A lot of thanks to examcollection for this gift!!!
@matt_owens, yes, you are in the right direction! these CIW 1D0-571 vce files will straighten your path to passing your exam easily. study them well but don’t also forget to check out other materials as well. nothing will stand in your way if you do this… all the best!
i have never used this site before but now I am using the CIW 1D0-571 exam dumps for my preparation… am i in the right direction guys? i will appreciate some advice
@Aiden, i passed my exam earlier today… these dumps for 1d0-571 exam are still valid! their contents really helped in making the exam questions familiar to me, i've seen only a few new ones but i managed all of them too because i also read the study guide from cover to cover. but in large part exactly exam dumps made handling the exam much easier… i would encourage you to use them
Are 1D0-571 braindumps still valid? who has used them recently?
my journey to being CIW certified was made a lot easier by practicing with the 1D0-571 questions and answers I found here. they were very efficient with time and very effective during my exam! examcollection surely did a great job on these materials busy candidates can find refuge in them!!!