



Premium File
159 Q&A
$76.99$69.99
Symantec 250-428 Exam Questions & Answers, Accurate & Verified By IT Experts
Instant Download, Free Fast Updates, 99.6% Pass Rate
159 Questions & Answers
Last Update: Oct 21, 2026
$69.99
Symantec 250-428 Exam Screenshots
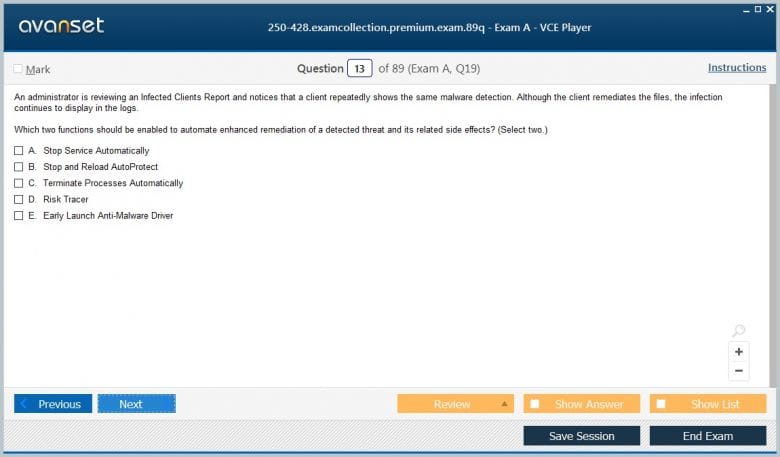
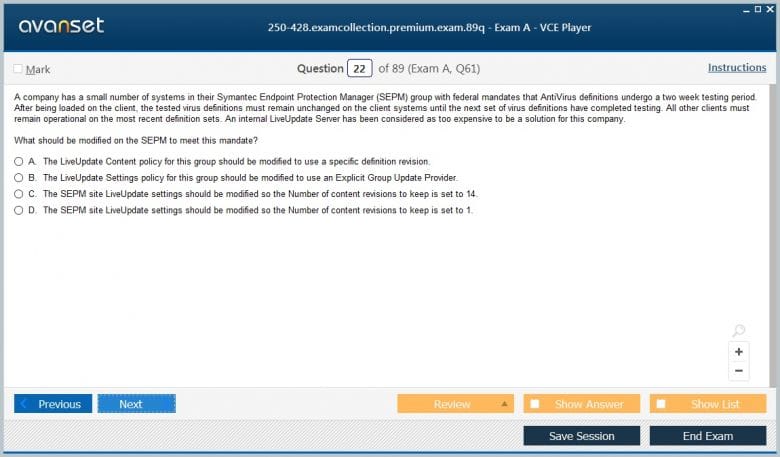
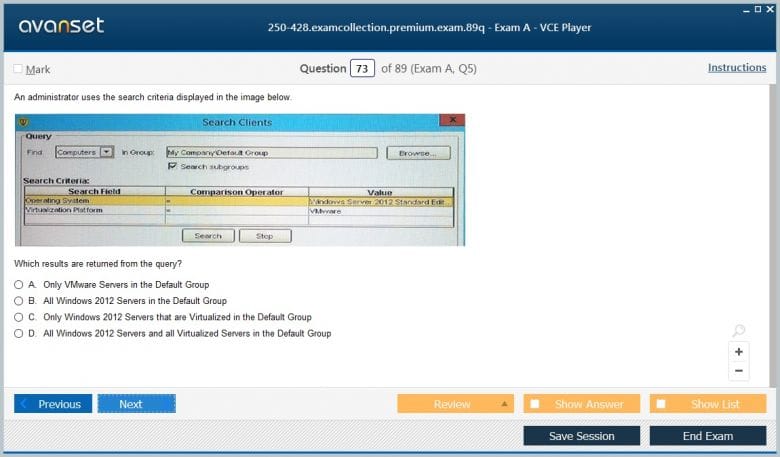
Symantec 250-428 Practice Test Questions in VCE Format
| File | Votes | Size | Date |
|---|---|---|---|
File Symantec.real-exams.250-428.v2026-09-29.by.ella.80q.vce |
Votes 1 |
Size 616.89 KB |
Date Sep 29, 2026 |
File Symantec.Braindumps.250-428.v2019-08-03.by.Ray.73q.vce |
Votes 5 |
Size 543.13 KB |
Date Aug 08, 2019 |
Symantec 250-428 Practice Test Questions, Exam Dumps
Symantec 250-428 (Administration of Symantec Endpoint Protection 14 (Broadcom)) exam dumps vce, practice test questions, study guide & video training course to study and pass quickly and easily. Symantec 250-428 Administration of Symantec Endpoint Protection 14 (Broadcom) exam dumps & practice test questions and answers. You need avanset vce exam simulator in order to study the Symantec 250-428 certification exam dumps & Symantec 250-428 practice test questions in vce format.
250-428 is the legacy Administration of Symantec Endpoint Protection 14 exam. Broadcom’s current certification catalog has moved to exam 250-605 for Symantec Endpoint Protection 14.x Admin R2, while the product itself remains actively maintained: Broadcom published Symantec Endpoint Protection 14.4 in 2026. That makes 250-428 historically important but no longer the current certification identifier.
The older exam covered the durable administrative responsibilities behind Endpoint Protection: installing and managing Symantec Endpoint Protection Manager, organizing clients, controlling communication and content updates, configuring protection policies, monitoring threats, delegating administration, and maintaining service resilience. Those concepts remain relevant because endpoint security still depends on consistent policy, current protection content, trustworthy management communication, and disciplined response.
The wider Symantec exam portfolio includes server, email, and other security technologies. Endpoint Protection focuses on managed endpoint controls and the operational systems around them. Candidates should study 250-428 as a legacy version of an active product discipline and avoid assuming that an old exam objective list represents every capability in today’s 14.x releases.
Symantec Endpoint Protection Manager coordinates client policy, content distribution, reporting, administrative access, and operational configuration. Candidates should understand how clients communicate with SEPM and why communication failures can create stale policy or visibility gaps. When endpoints appear unmanaged, the investigation should separate client health, network connectivity, certificate or trust issues, server configuration, and database or service problems.
The management plane itself needs protection. Administrative roles should follow least privilege, console access should be controlled, and recovery procedures should be documented. A compromised or unavailable management system can affect a large endpoint population, so security and resilience of SEPM are part of endpoint defense.
Database health and management-server performance can affect what administrators see. If reporting lags or services are overloaded, endpoints may still enforce cached policy while the console presents incomplete freshness. Troubleshooting should therefore distinguish enforcement state on the client from visibility state in SEPM. That distinction prevents unnecessary policy changes when the real issue is management-plane health.
Client groups can mirror business units, device types, sensitivity, or operational ownership, while location awareness can change behavior depending on network context. These features reduce the need to configure every endpoint individually, but they make hierarchy design important. A poorly designed group tree can cause inherited policy to reach systems that were not intended to receive it.
Administrators should be able to trace why a client has a particular policy. When troubleshooting, verify group membership, location state, inheritance, and any exceptions before changing the control itself. Clear structure makes incidents easier to resolve and reduces the risk of solving a local problem with a global policy change.
Location awareness should be tested against the real network states endpoints encounter: corporate LAN, VPN, home network, public wireless, and disconnected operation. Misclassification can apply the wrong firewall or protection behavior at exactly the moment a device leaves the trusted network. Controlled testing across those transitions is more reliable than assuming a location rule will match as designed.
Endpoint protection depends on timely security content, yet large environments must manage bandwidth and network boundaries. Administrators should understand LiveUpdate behavior, management-server distribution, group update providers, and other methods used to get current content to clients. The correct design depends on site topology, connectivity, client count, and tolerance for delay.
Validation should focus on freshness, not simply configuration. A system can be assigned the right update method and still fail to receive current content. Monitoring definitions and client status helps reveal broken distribution paths before an outbreak exposes the gap. Security content is an operational dependency that needs health monitoring like any other service.
Remote and intermittently connected devices create another challenge. Laptops may spend long periods away from corporate networks, so update architecture must account for internet-based access or other supported methods. Administrators should monitor age of definitions across the fleet and identify populations that repeatedly miss updates rather than assuming mobile devices eventually catch up.
Antimalware is only one layer. SEP 14-era administration includes intrusion prevention, firewall controls, reputation and behavior-based protections, application and device controls, and other capabilities depending on deployment and licensing. Candidates should understand the purpose of each control and how overlapping policies can affect user activity and troubleshooting.
The article on detecting malware provides useful conceptual context because prevention and detection depend on different signals. Signature-based recognition, behavioral indicators, reputation, and exploit protection each contribute evidence. Administrators should avoid assuming that one engine can address every endpoint threat.
Policy interaction should be tested because one technology can affect another. A firewall rule may block a management or update path, application control may interfere with a security tool, or aggressive remediation may disrupt a legitimate process. Administrators should isolate which control produced an outcome and avoid disabling multiple layers at once during troubleshooting.
Host firewall and IPS controls can stop attacks close to the endpoint, but incorrect rules can also interrupt legitimate communication. Administrators need to understand policy order, network services, application behavior, and how clients move between networks. Staged deployment and logging can reveal unintended effects before enforcement reaches the whole fleet.
Troubleshooting should identify the exact traffic or behavior being blocked. Broad exclusions may restore connectivity quickly but weaken protection. Narrow rule changes, documented rationale, and later review preserve the security intent. This mirrors the policy discipline required in broader network security.
When policies change, administrators should compare client-side logs with SEPM-side reporting to confirm the intended rule actually reached the endpoint. Cached or stale policy can make troubleshooting confusing because console configuration and endpoint behavior may temporarily disagree. Verification closes that gap.
Organizations may need to restrict executable behavior, removable media, or device classes for security and compliance reasons. Application and device control policies can enforce those decisions, but the business impact must be understood. Blocking a device category without mapping operational dependencies can disrupt legitimate workflows in support, manufacturing, healthcare, or other environments.
Good administrators work with business owners to define permitted behavior and test representative systems. Exceptions should identify specific requirements rather than create broad bypasses. Endpoint security is strongest when policy is both technically enforceable and operationally sustainable.
SEPM reporting and monitoring help administrators recognize malware activity, policy violations, outdated clients, and other conditions. The goal is not to maximize event volume; it is to identify patterns that require action. Repeated detections on one host, a sudden population of unmanaged clients, or consistent update failures may each indicate a different operational problem.
When a true incident occurs, endpoint evidence should feed the wider incident-response lifecycle. Containment may involve isolating systems or changing policy, while recovery requires confidence that malicious persistence is removed and protection is current. Endpoint administration and incident response should reinforce each other.
Operational metrics can reveal structural problems before a major incident. Rising counts of offline clients, repeated remediation failures, or large groups on outdated software versions point to lifecycle issues that deserve administrative work. Endpoint security is not only about reacting to malware; it is also about keeping the protective fleet consistently healthy.
Large deployments may use multiple management servers and databases for resilience or geographic distribution. Candidates should understand the purpose of replication and failover and the difference between high availability and backup. Replication can copy bad configuration or corruption just as effectively as good state; backups provide a separate recovery capability.
Recovery planning should include configuration, database state, certificates, communication settings, and the steps clients will follow after restoration. Testing matters because an untested backup is only an assumption. Endpoint protection remains effective during disruption only when the management architecture has a realistic recovery plan.
Disaster-recovery exercises should verify that restored management components can re-establish trusted communication with existing clients. Recovery is incomplete if the server starts but endpoints cannot authenticate, receive policy, or upload status. Include certificates and communication material in the recovery plan rather than treating them as incidental configuration.
Broadcom’s current exam catalog lists 250-605 for Symantec Endpoint Protection 14.x Admin R2, not 250-428. At the same time, SEP itself remains current, including the 14.4 release line. This distinction is important: an old exam code does not mean the product is obsolete, and a current product does not make every historical exam objective current.
Candidates maintaining older environments can still learn from 250-428, especially its emphasis on SEPM, client communication, policy, content, monitoring, and resilience. The related Data Center Security exam shows a different host-protection model, while Email Security.cloud administration covers another layer. Together they illustrate why enterprise security is built from coordinated controls rather than one endpoint product.
Current SEP releases can introduce new operating-system support, management behavior, and protection features that were not part of the 250-428 era. Teams studying the legacy objectives should therefore separate conceptual learning from configuration authority. Use the old material to understand architecture and terminology, then verify procedures against current Broadcom release notes and product documentation before making changes.
For practical study, build a small managed-client lab and observe policy delivery, content updates, firewall behavior, detections, and reporting together. Seeing how the management server and client state differ during disconnects or update delays creates a much stronger mental model than reading each feature separately.
Go to testing centre with ease on our mind when you use Symantec 250-428 vce exam dumps, practice test questions and answers. Symantec 250-428 Administration of Symantec Endpoint Protection 14 (Broadcom) certification practice test questions and answers, study guide, exam dumps and video training course in vce format to help you study with ease. Prepare with confidence and study using Symantec 250-428 exam dumps & practice test questions and answers vce from ExamCollection.
Purchase Individually
Top Symantec Certification Exams
Site Search:

SPECIAL OFFER: GET 10% OFF

Pass your Exam with ExamCollection's PREMIUM files!
SPECIAL OFFER: GET 10% OFF
Use Discount Code:
MIN10OFF
A confirmation link was sent to your e-mail.
Please check your mailbox for a message from support@examcollection.com and follow the directions.

Download Free Demo of VCE Exam Simulator
Experience Avanset VCE Exam Simulator for yourself.
Simply submit your e-mail address below to get started with our interactive software demo of your free trial.
is this dump valid?
any one pass recently with premium dump ? Please let us know
Is this dump valid?
This dumps valid.
is this a valid dump?
need 250-428 exam dumps
Is the premium dump valid?