



Premium File
176 Q&A
$76.99$69.99
CyberArk CAU201 Exam Questions & Answers, Accurate & Verified By IT Experts
Instant Download, Free Fast Updates, 99.6% Pass Rate
176 Questions & Answers
Last Update: Sep 21, 2026
$69.99
CyberArk CAU201 Exam Screenshots
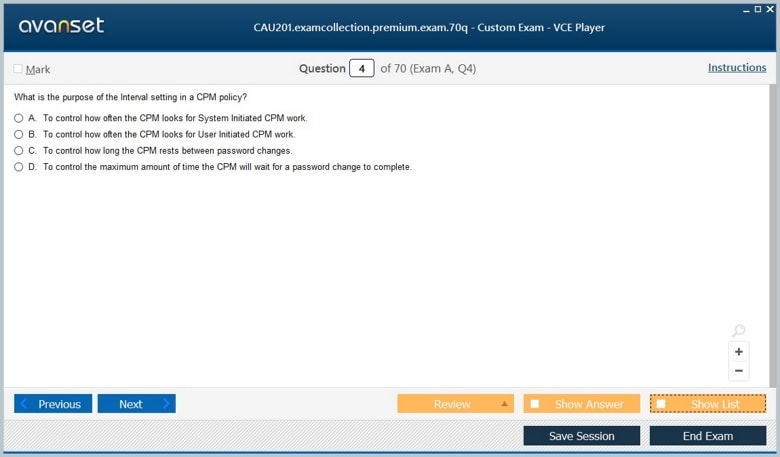
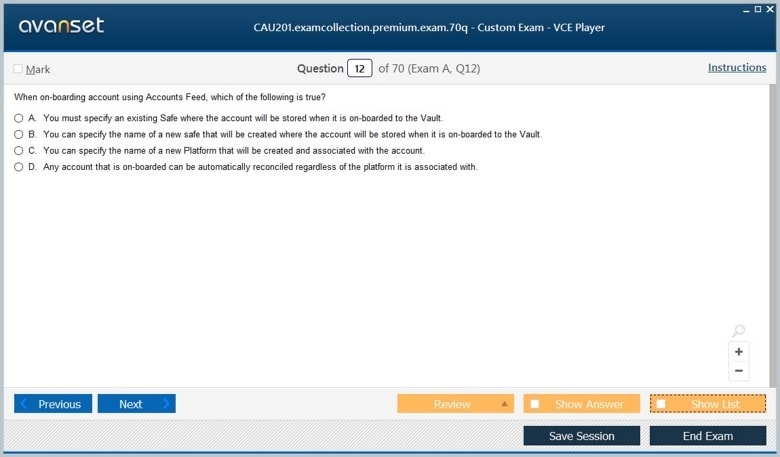
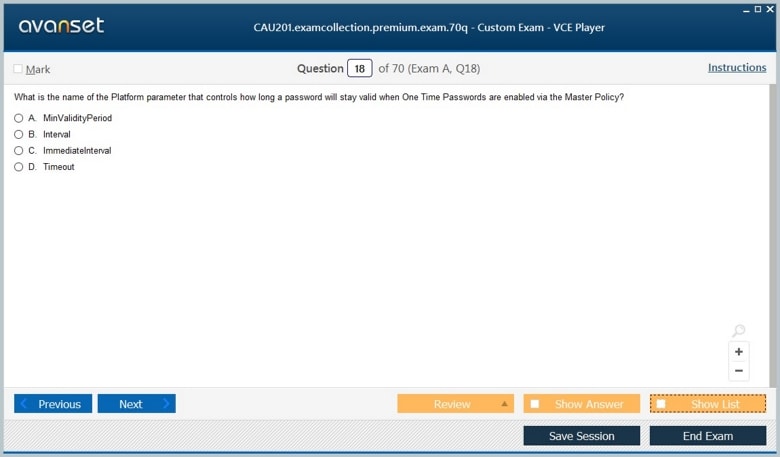
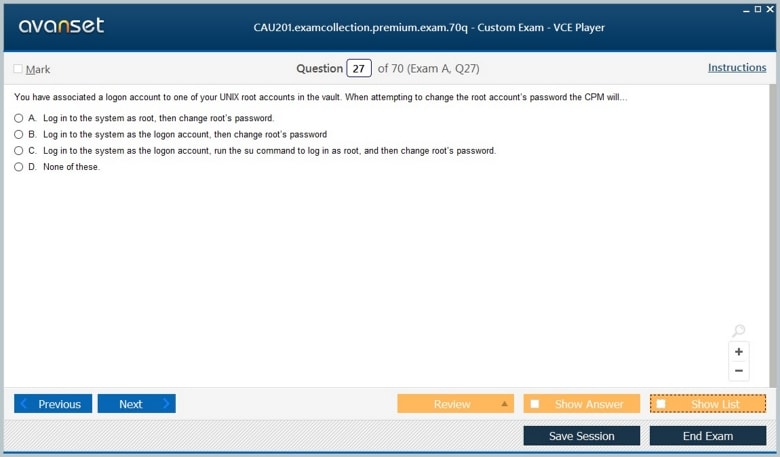
CyberArk CAU201 Practice Test Questions in VCE Format
| File | Votes | Size | Date |
|---|---|---|---|
File CyberArc.examlabs.CAU201.v2026-09-01.by.ellis.103q.vce |
Votes 1 |
Size 1.72 MB |
Date Sep 01, 2026 |
File CyberArc.examlabs.CAU201.v2022-02-10.by.katie.92q.vce |
Votes 1 |
Size 1.67 MB |
Date Feb 10, 2022 |
File CyberArc.practicetest.CAU201.v2021-12-27.by.maria.83q.vce |
Votes 1 |
Size 1.49 MB |
Date Dec 27, 2021 |
File CyberArc.examanswers.CAU201.v2021-11-10.by.alexander.68q.vce |
Votes 1 |
Size 1.31 MB |
Date Nov 10, 2021 |
File CyberArc.vceplayer.CAU201.v2021-04-26.by.finley.39q.vce |
Votes 1 |
Size 46.16 KB |
Date Apr 28, 2021 |
File CyberArc.realtests.CAU201.v2020-02-24.by.antoni.37q.vce |
Votes 2 |
Size 44.14 KB |
Date Feb 24, 2020 |
File CyberArc.Actualtests.CAU201.v2019-10-03.by.Raymond.34q.vce |
Votes 3 |
Size 35.18 KB |
Date Oct 09, 2019 |
File CyberArc.Braindumps.CAU201.v2019-04-15.by.Giulia.18q.vce |
Votes 3 |
Size 21.01 KB |
Date Apr 17, 2019 |
CyberArk CAU201 Practice Test Questions, Exam Dumps
CyberArk CAU201 (CyberArk Defender) exam dumps vce, practice test questions, study guide & video training course to study and pass quickly and easily. CyberArk CAU201 CyberArk Defender exam dumps & practice test questions and answers. You need avanset vce exam simulator in order to study the CyberArk CAU201 certification exam dumps & CyberArk CAU201 practice test questions in vce format.
CAU201 is an older CyberArk Defender exam identifier associated with day-to-day operation of privileged access environments. It is no longer listed in CyberArk’s current Pearson VUE exam lineup. The live Privileged Access Management Defender exam is PAM-DEF, so current candidates should use CAU201 material for durable PAM concepts while validating present objectives against the current Defender credential.
That transition does not make the older material useless. Privileged access management still revolves around discovering privileged identities, vaulting credentials, rotating passwords or secrets, controlling access, brokering sessions, recording sensitive activity, applying policy, monitoring risk, and recovering from operational failures. What changes over time is the product interface, architecture detail, feature set, and exam blueprint.
The CyberArk Defender PAM pathway is the natural current context. Candidates should think in terms of maintaining a production PAM service: protecting the credentials that can change systems, ensuring authorized people can use them when needed, and creating enough control and evidence that privileged activity is accountable.
A privileged credential may administer an operating system, database, network appliance, cloud service, application, or security platform. Because the impact of misuse is high, organizations need more than a directory account and password policy. They need inventory, ownership, controlled storage, rotation, access rules, session oversight, and procedures for emergencies.
The first challenge is completeness. Unknown privileged accounts cannot be protected by the platform. Discovery should therefore lead to classification: human administrator, service account, application credential, local account, shared account, emergency identity, and so on. Each category has different dependencies and different tolerance for automated rotation.
The principles behind identity lifecycle management still apply, but privileged identities deserve additional scrutiny because an error can either expose critical access or interrupt critical services. Defender operators need to balance security with availability.
Centralizing credentials creates an opportunity to remove direct knowledge of passwords from users and applications, but the security benefit depends on policy. Who can retrieve a credential? Who can request access? Is approval required? Are sessions brokered instead of passwords revealed? What happens outside business hours? How is emergency access handled?
Authorization should follow role and task rather than convenience. A support engineer may need access to a limited group of systems, while a platform administrator may need broader configuration authority. Separating operational access from administrative control of the PAM platform itself reduces the chance that one compromised identity can bypass every safeguard.
The role-based access-control model is a useful general reference because it emphasizes explicit assignments, scoped permissions, and review. The exact CyberArk objects differ, but the reasoning is the same.
Automatic rotation is one of the strongest PAM controls because it reduces the life of a stolen password, but rotation can create outages when services, scripts, scheduled tasks, or applications depend on the credential in unexpected ways. Before onboarding an account, operators should understand how the credential is used and whether dependent systems can retrieve updated secrets automatically.
Reconciliation and recovery processes matter when the platform loses synchronization with the target. A Defender operator should understand the difference between changing a password through the normal workflow and recovering an account whose stored credential no longer matches the system. The objective is to restore controlled state without creating an undocumented bypass.
Secrets-management concepts discussed in secure secrets management reinforce the same principle: credentials should be stored, rotated, delivered, and audited in ways that reduce human handling and long-lived exposure.
A strong PAM design can broker privileged sessions so users do not need to know the underlying credential. Session controls can reduce credential exposure, enforce connection methods, and create a record of high-risk activity. Operators need to understand both the security value and the operational dependencies of the session infrastructure.
When a privileged session fails, troubleshooting should identify whether the problem is authorization, target connectivity, credential validity, connection component configuration, user mapping, policy, or session infrastructure. Changing multiple controls at once may restore access while making the original fault impossible to diagnose.
Session evidence also supports incident response. The incident-response discipline of preserving timelines and accountable actions is directly relevant when investigators need to determine who used privileged access, which systems were reached, and what occurred during the session.
A PAM deployment depends on vault services, web interfaces, password-management components, session infrastructure, directories, target systems, certificates, and network paths. Security is weakened when operators treat availability as somebody else’s problem. If the platform is unreliable, teams may create unmanaged emergency workarounds that persist after the incident.
Defender operators should monitor service health, capacity, credential-management failures, session errors, integration problems, certificates, backups, and administrative changes. They also need tested recovery procedures. A backup that has never been restored is an assumption rather than a recovery capability.
Configuration management is equally important. Changes to platforms, safes, policies, connection components, or integrations should be approved, documented, tested, and reversible. The same reasoning found in security auditing applies: high-impact changes need a reliable trail.
Many PAM problems begin during onboarding. An account is added without a clear owner, platform assignment is wrong, dependencies are not documented, rotation is enabled too aggressively, or a service credential is treated like a human account. The platform may appear functional until a password change or incident exposes the hidden dependency.
A mature onboarding record should capture the account purpose, owner, target system, credential type, rotation expectations, dependencies, access group, approval model, session method, validation test, and rollback plan. The specific fields vary, but the principle is simple: someone who did not perform the original onboarding should still be able to understand how the control is supposed to work.
Candidates can practice by onboarding a fictional administrative account and then introducing failures: target unavailable, password changed outside the vault, owner leaves, new approval requirement, service dependency discovered, or session brokering disabled. Each scenario tests whether the control is operationally resilient.
The current CyberArk certification structure separates Defender, Sentry, and Guardian responsibilities more explicitly than older combined learning paths. Defender validates day-to-day maintenance and operations, while PAM-SEN focuses on deployment and configuration at the Sentry level. That distinction helps candidates decide which older CAU201 topics remain directly relevant.
Older terminology or interface details should be verified before memorization. CyberArk has expanded from traditional privileged access security into a broader identity-security platform, and product names evolve. The durable study target is the operating model: discover privileged access, place it under control, enforce policy, rotate credentials safely, broker and record sessions, monitor health, and retain accountable evidence.
Use CAU201 as historical preparation material, not as proof that the code is currently bookable. CyberArk’s current Pearson VUE list does not include CAU201 and does include PAM-DEF. Current candidates should organize study around the live PAM Defender objectives while carrying forward the operational reasoning that made CAU201 useful.
Routine review is another Defender responsibility that older exam material can underemphasize. Privileged access should be periodically checked for stale accounts, orphaned ownership, excessive safe membership, unused platforms, failed rotations, and emergency privileges that were never removed. These reviews reduce the gap between the intended architecture and the environment that actually exists months later. A system can start secure and drift into risk through ordinary operational change.
Service accounts deserve special handling because they combine privilege with availability. Before changing a password, the operator should know which service, scheduled task, application pool, script, or integration consumes it. Where the platform can update dependencies automatically, that capability should be tested. Where it cannot, the rotation process needs coordination and rollback. Treating service accounts exactly like human administrator accounts is a common path to production incidents.
Emergency access should also be designed before an emergency. Organizations need a controlled way to reach critical systems when normal PAM components, directories, or networks are unavailable. Those credentials should be strongly protected, their use should be exceptional and attributable, and the organization should rotate or review them after use. Break-glass access that nobody has tested is not resilience; it is a hope that the credential still works.
Finally, Defender operators should measure whether the program is improving. Useful operational measures include unmanaged privileged accounts discovered, failed password-management jobs, accounts overdue for rotation, session failures, emergency-access events, stale owners, and time to resolve platform incidents. Metrics are valuable when they expose control weakness and drive action, not when they merely produce a dashboard with reassuring green indicators.
Candidates should also understand how ownership changes are handled. A privileged account may outlive the administrator or application team that created it, so the PAM process needs a way to reassign responsibility, verify continued business need, and remove obsolete access. Orphaned privileged accounts are dangerous precisely because routine teams assume someone else is still accountable for them.
This ownership discipline is easy to overlook during exam study, but it is central to real PAM operations because unmanaged responsibility eventually becomes unmanaged privilege.
Go to testing centre with ease on our mind when you use CyberArk CAU201 vce exam dumps, practice test questions and answers. CyberArk CAU201 CyberArk Defender certification practice test questions and answers, study guide, exam dumps and video training course in vce format to help you study with ease. Prepare with confidence and study using CyberArk CAU201 exam dumps & practice test questions and answers vce from ExamCollection.
Purchase Individually
Top CyberArk Certifications

Top CyberArk Certification Exams
Site Search:

SPECIAL OFFER: GET 10% OFF

Pass your Exam with ExamCollection's PREMIUM files!
SPECIAL OFFER: GET 10% OFF
Use Discount Code:
MIN10OFF
A confirmation link was sent to your e-mail.
Please check your mailbox for a message from support@examcollection.com and follow the directions.

Download Free Demo of VCE Exam Simulator
Experience Avanset VCE Exam Simulator for yourself.
Simply submit your e-mail address below to get started with our interactive software demo of your free trial.